
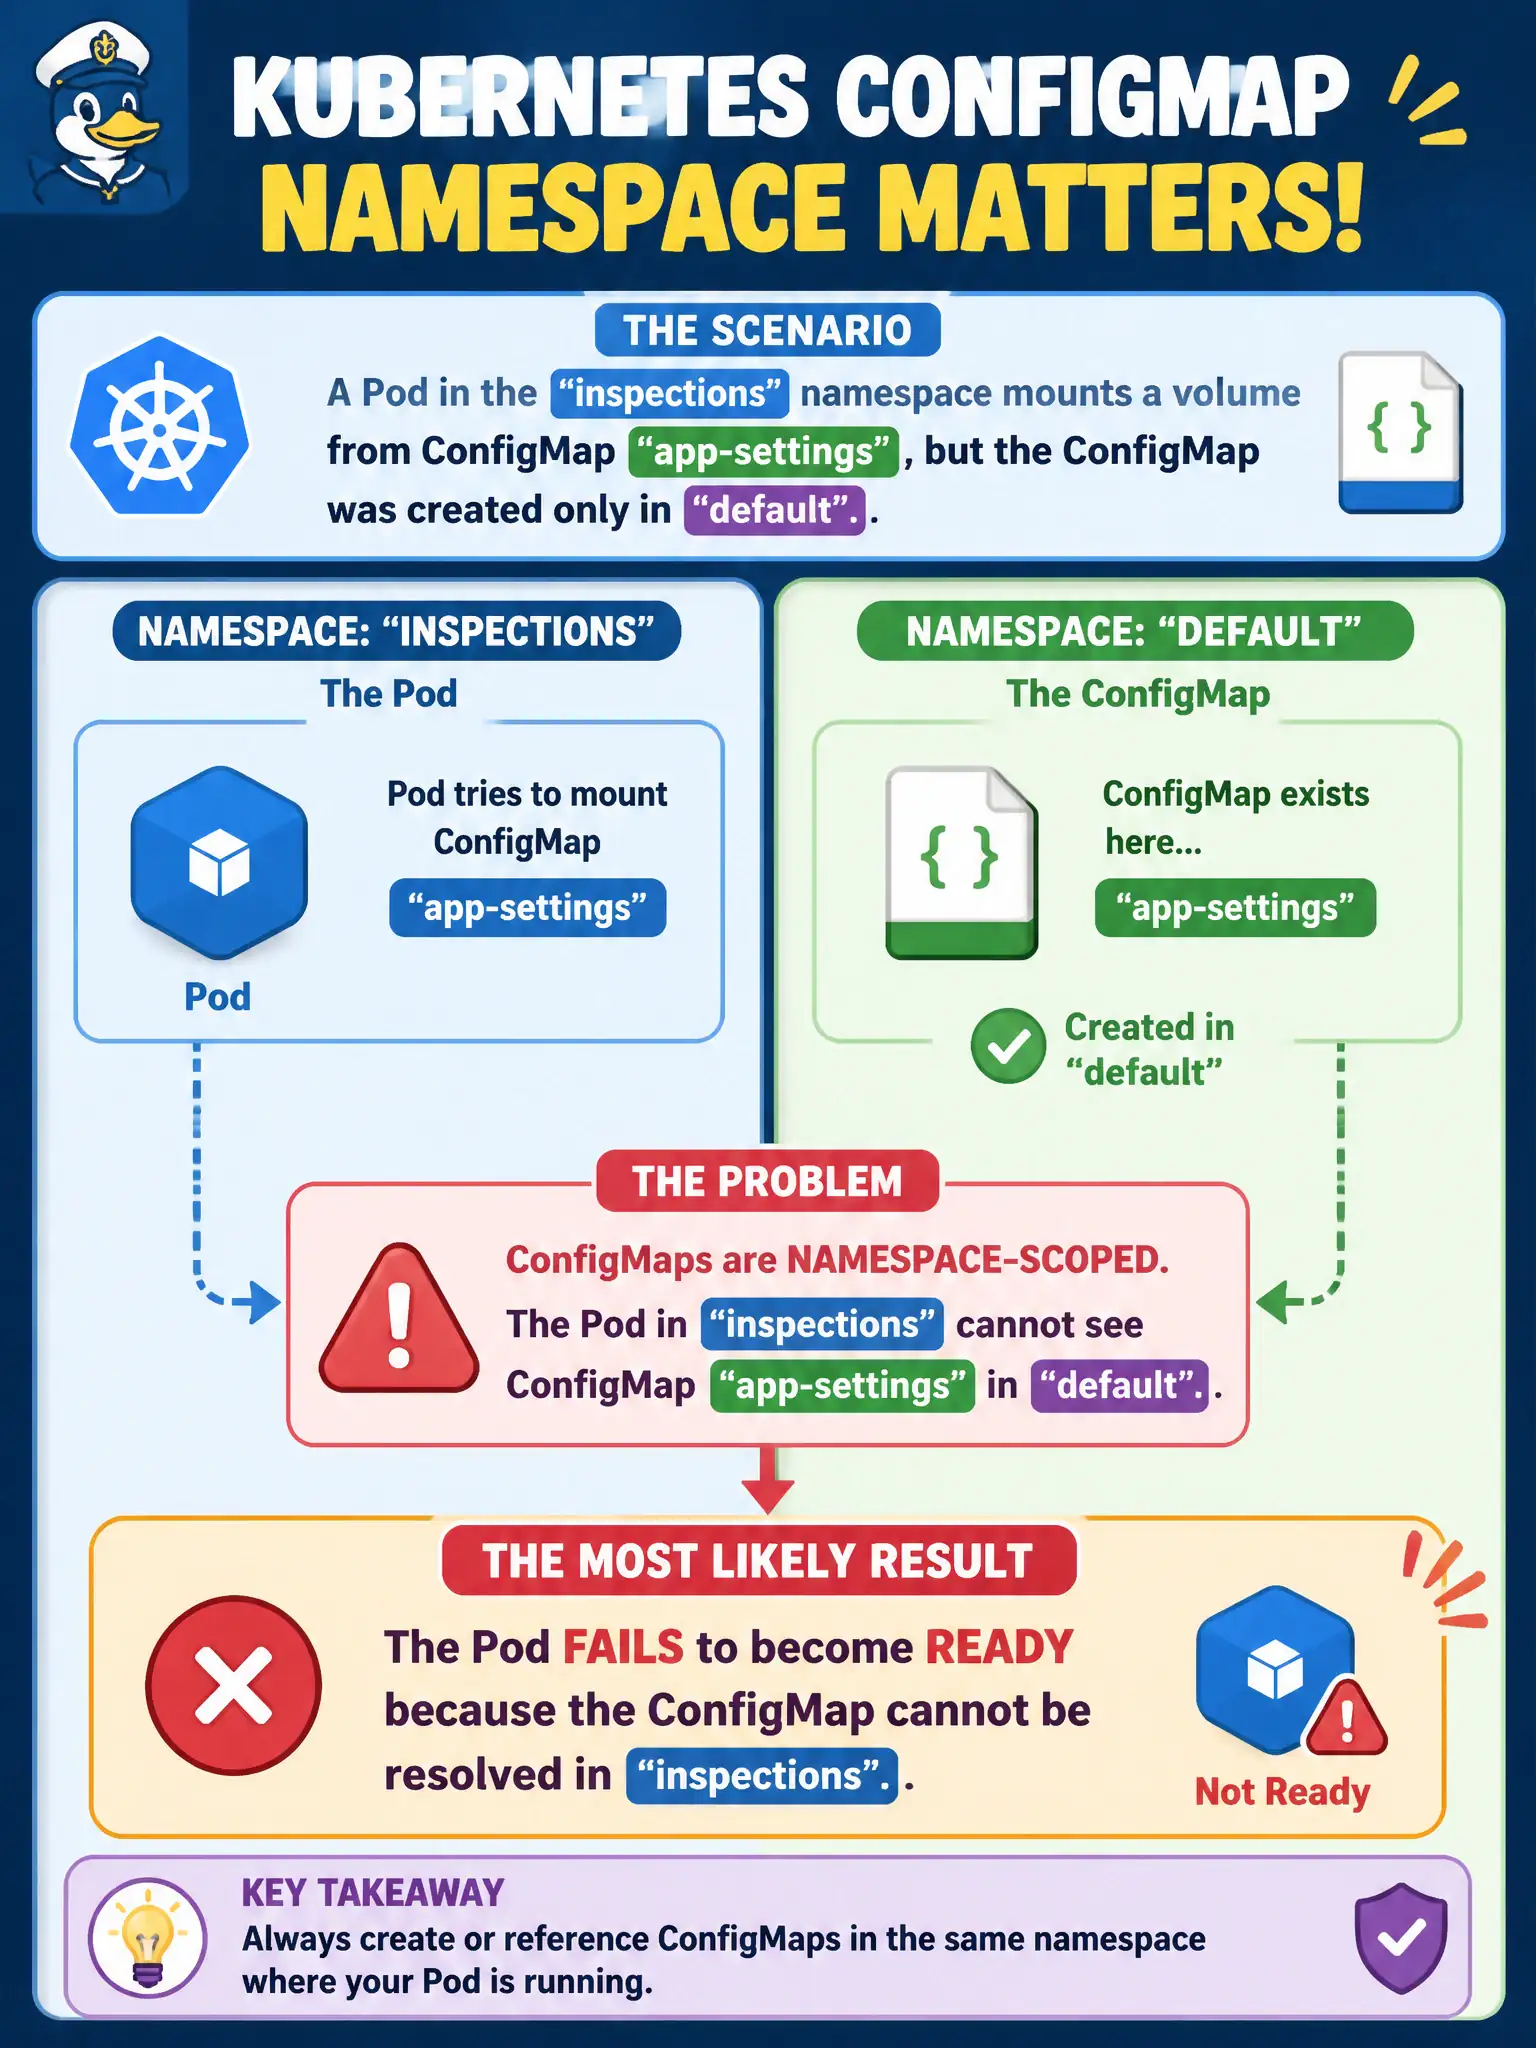
A Pod in the inspections namespace mounts a volume from ConfigMap app-settings, but the ConfigMap was created only in default. What is the most likely result?
Select an answer to reveal the explanation.
Short Explanation
ConfigMaps are like office binders that stay on their own floor—namespaces don't share them. If the Pod runs in inspections but the ConfigMap lives only in default, the mount reference misses. Create or copy the ConfigMap in the same namespace as the Pod.
Full Explanation
A Pod in the inspections namespace that mounts a volume from ConfigMap app-settings created only in default most likely fails to become Ready because ConfigMaps are namespaced and cannot be resolved across namespaces. The Pod in inspections cannot see the ConfigMap in default, so the required volume mount fails. Municipal teams must create the ConfigMap in the consumer namespace or otherwise distribute the data intentionally.
Claiming Kubernetes automatically copies the ConfigMap into inspections when the Pod is admitted invents cross-namespace copying that does not occur. Claiming the volume mounts empty and the container still starts with defaults from the image understates the usual failure mode for required ConfigMap volumes. Claiming kube-proxy rewrites the mount to pull ConfigMap data across namespaces fails because kube-proxy is not a ConfigMap distribution mechanism.
Exam caveat: marking a ConfigMap volume optional can allow startup with warnings, but required mounts block readiness when the object is missing. Operational check: kubectl get configmap app-settings -n inspections, create it there if missing, restart the Pod, and confirm Ready becomes true with the mount populated.