
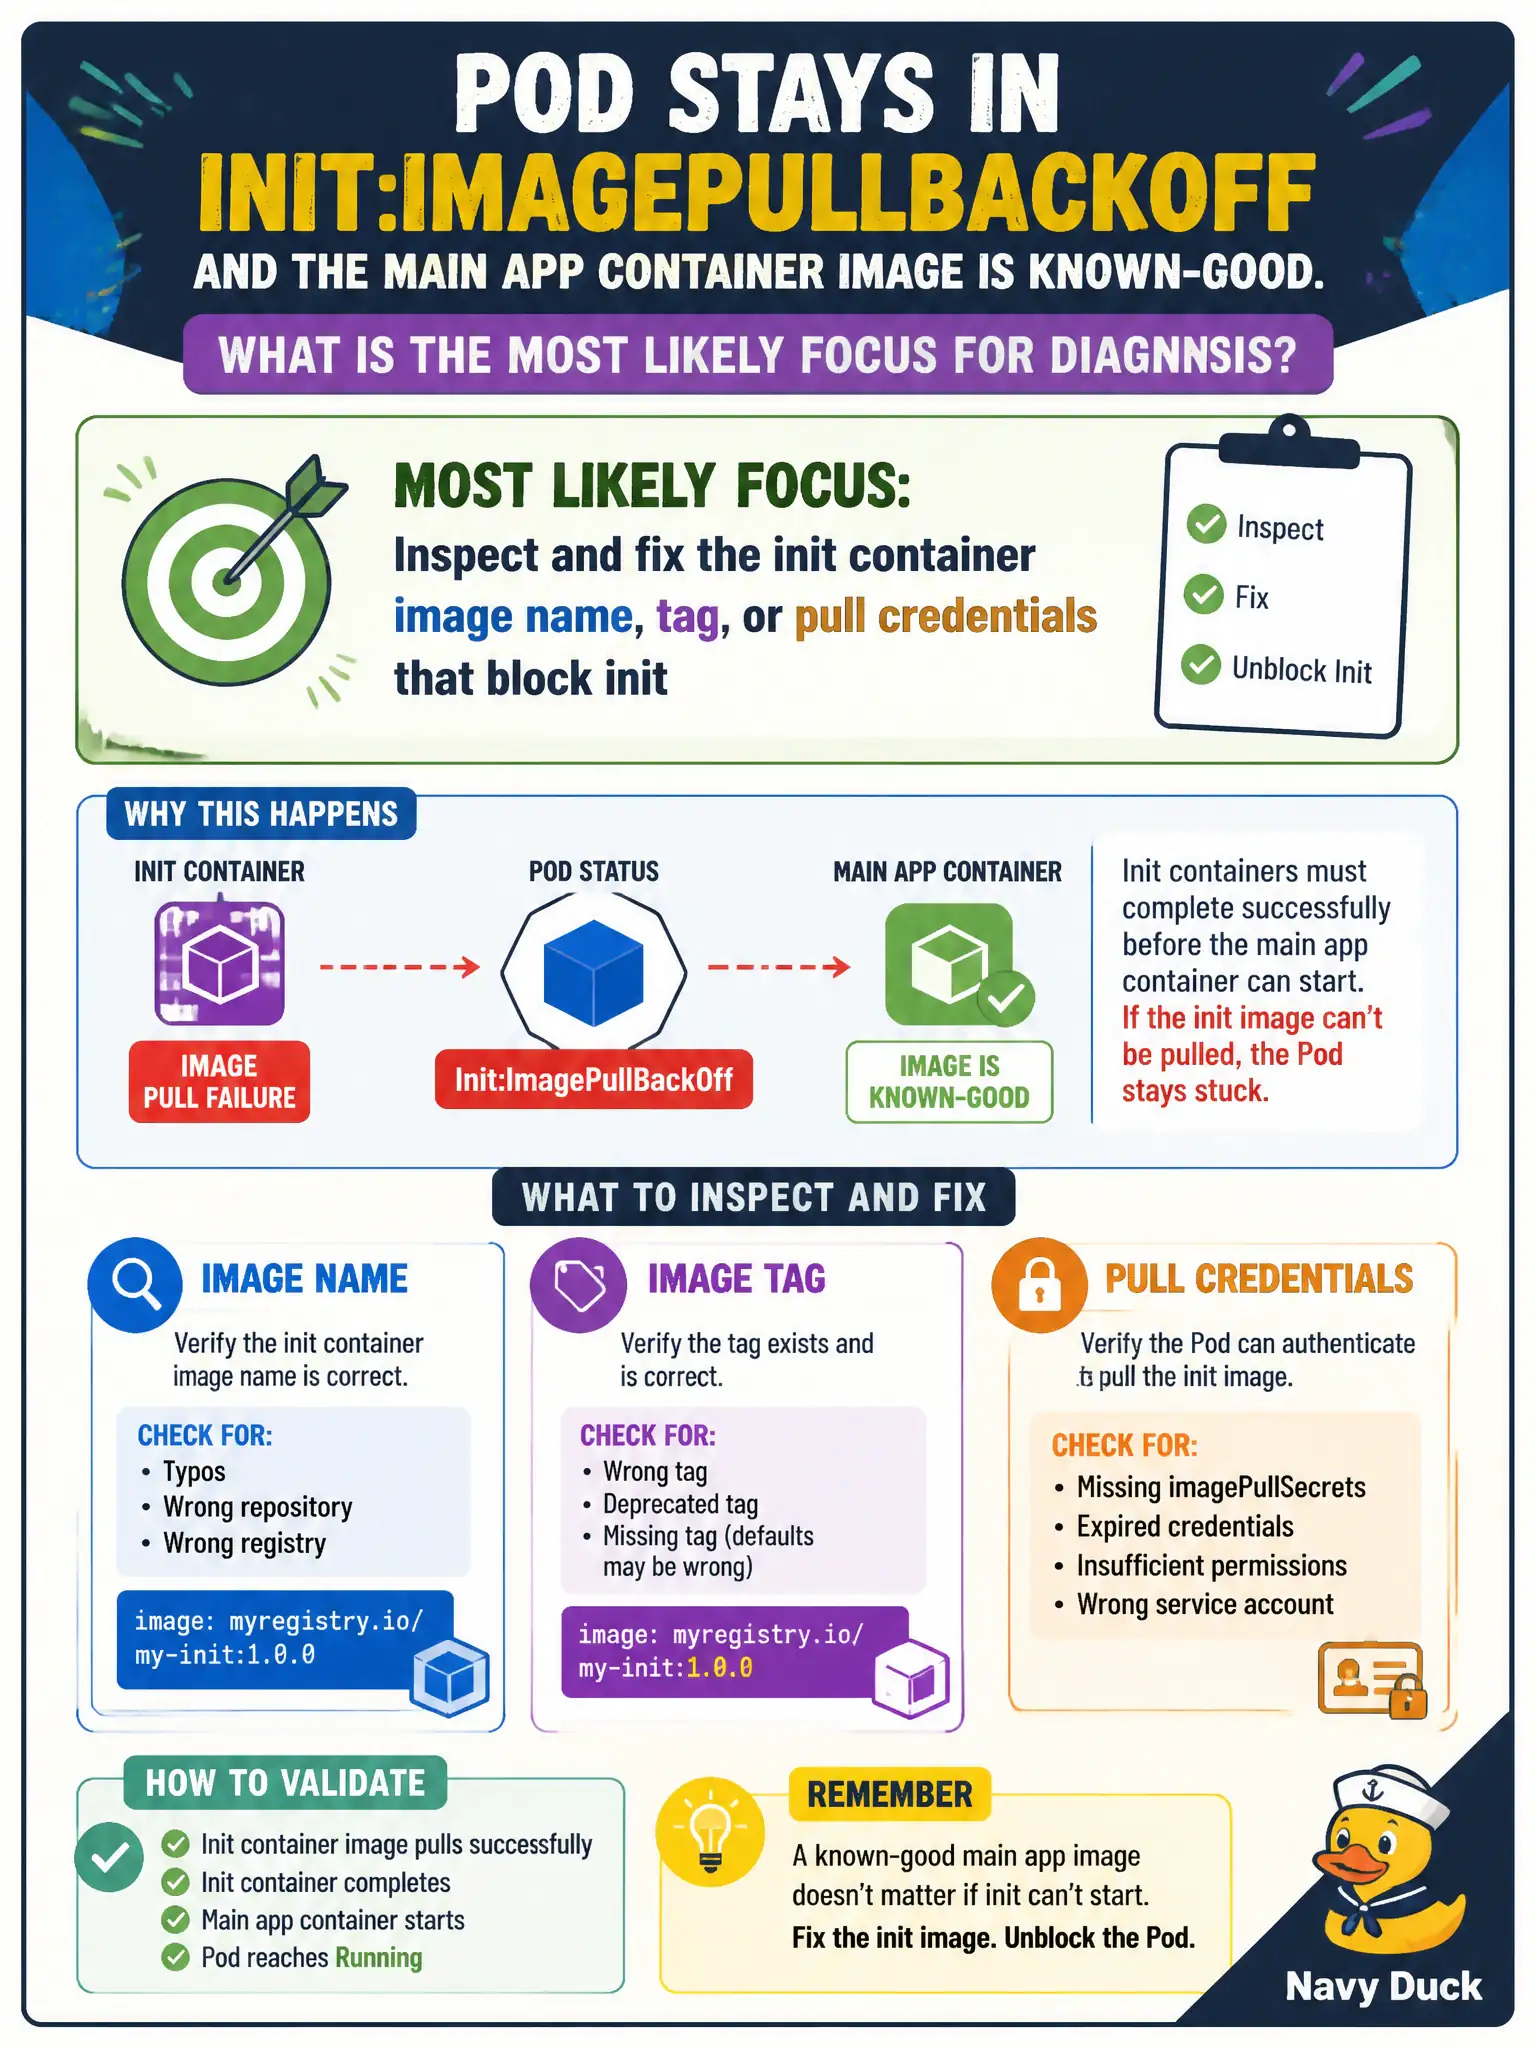
A Pod stays in Init:ImagePullBackOff and the main app container image is known-good. What is the most likely focus for diagnosis?
Select an answer to reveal the explanation.
Short Explanation
If the warm-up act’s costume never arrives, the show never starts—even if the headliner’s outfit is fine. Init:ImagePullBackOff points at the init image or its pull access, not the Service type.
Full Explanation
If a Pod remains in Init:ImagePullBackOff while the main application container image is known-good, the most likely diagnostic focus is the init container’s image name, tag, or pull credentials. Init images are pulled and executed before application containers start; a typo, wrong registry host, or missing imagePullSecret for the init image leaves the Pod stuck even though the app image would pull successfully on its own.
Increasing Deployment replicas does not skip the init phase—each new Pod repeats the same failing init pull. Removing readinessProbes does not cure ImagePullBackOff, which is a pull failure, not a probe failure. Changing the Service type to NodePort does not unlock image pulls; Services are unrelated to registry authentication.
Exam caveat: kubectl describe pod Events distinguish init versus app pull errors. imagePullSecrets on the Pod apply to all containers, including init containers.
Operational check: kubectl describe pod and inspect init container events; kubectl get events --field-selector reason=Failed; fix the init image reference or Secret; confirm Init becomes Complete and the application starts. In municipal environments, document the chosen pattern in the service runbook so on-call engineers apply the same kubectl checks during incidents, and keep the change tied to the application Deployment or Job rather than ad-hoc node mutation.