
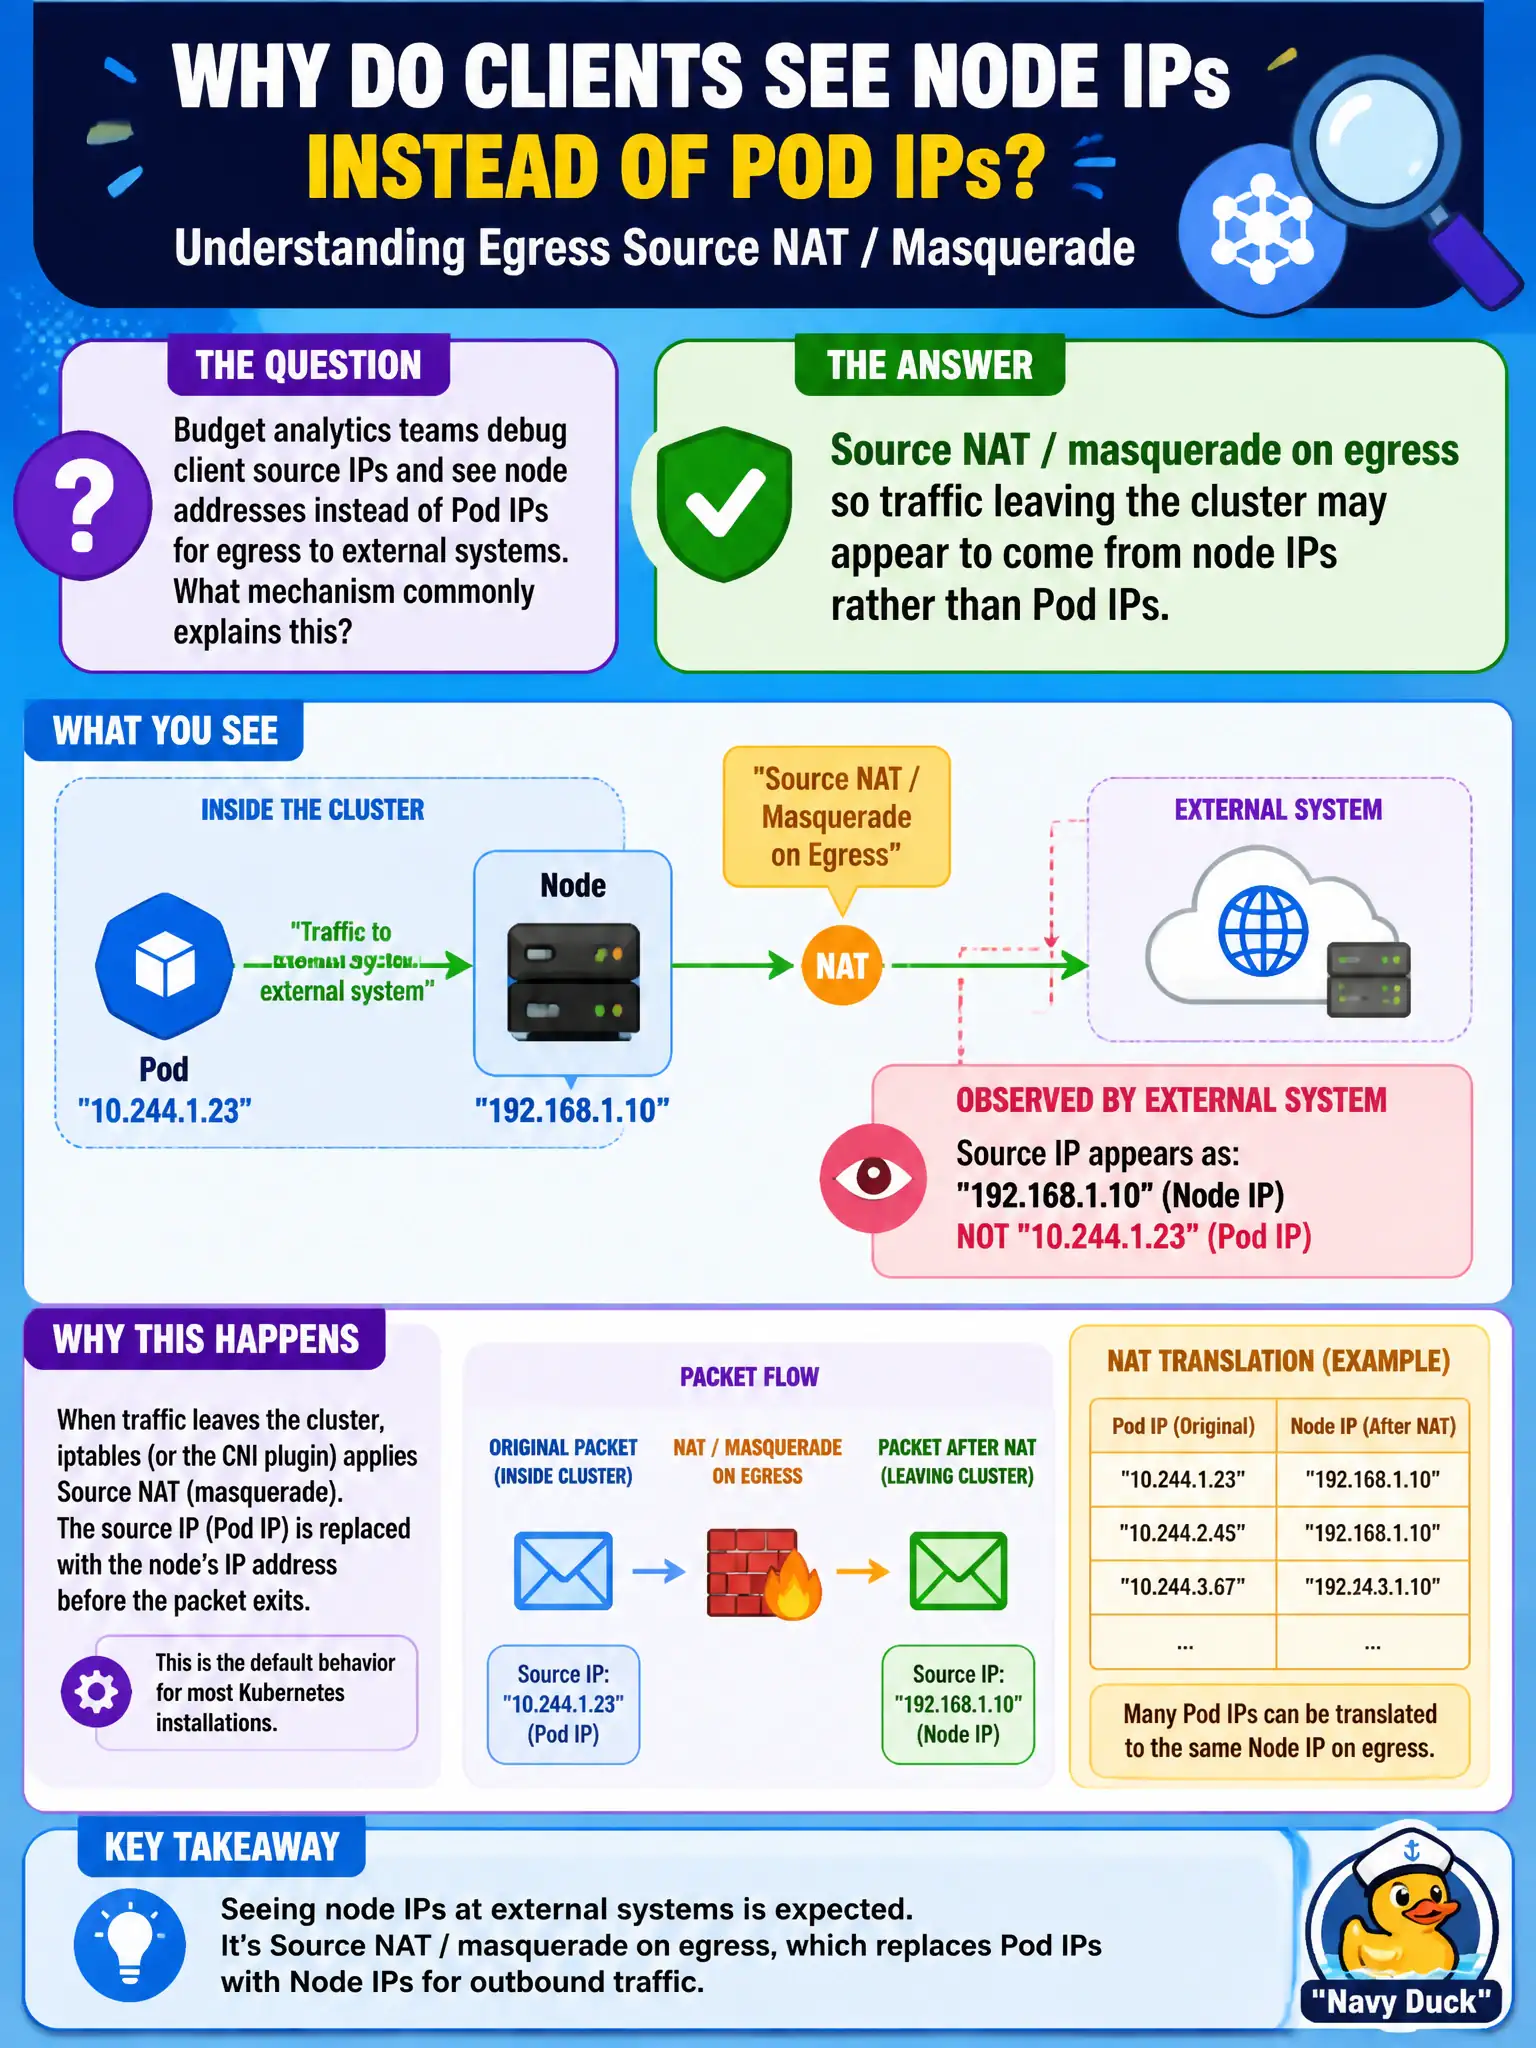
Budget analytics teams debug client source IPs and see node addresses instead of Pod IPs for egress to external systems. What mechanism commonly explains this?
Select an answer to reveal the explanation.
Short Explanation
Pods often leave the building wearing the node’s jacket—SNAT/masquerade. External systems see the node IP, not the Pod’s private number.
Full Explanation
Source NAT / masquerade on egress commonly makes traffic leaving the cluster appear to come from node IPs rather than Pod IPs. Budget analytics teams debugging client source IPs for external systems should expect pods to leave the building wearing the node's jacket unless special egress networking preserves Pod identity. kubelet does not replace every Pod IP with the Service ClusterIP in application logs only as the mechanism for egress source addresses seen by external peers. NetworkPolicy logging does not rewrite source IPs to 127.0.0.1 for privacy as the usual explanation of node-sourced egress. Gateway API status conditions do not publish client IPs into etcd each minute as an egress SNAT mechanism. Exam caveat: Some CNIs offer egress gateways or public Pod IPs. On standard masquerade setups, external ACLs must allow node CIDRs. Operational check: Capture source IPs at the external system, correlate to node IPs, document SNAT behavior for budget integrations, and adjust firewall allowlists accordingly. In municipal production practice, record the finding in the incident ticket with command output snippets, confirm the fix under change control, and re-validate the user-facing civic service before closing the change window.