
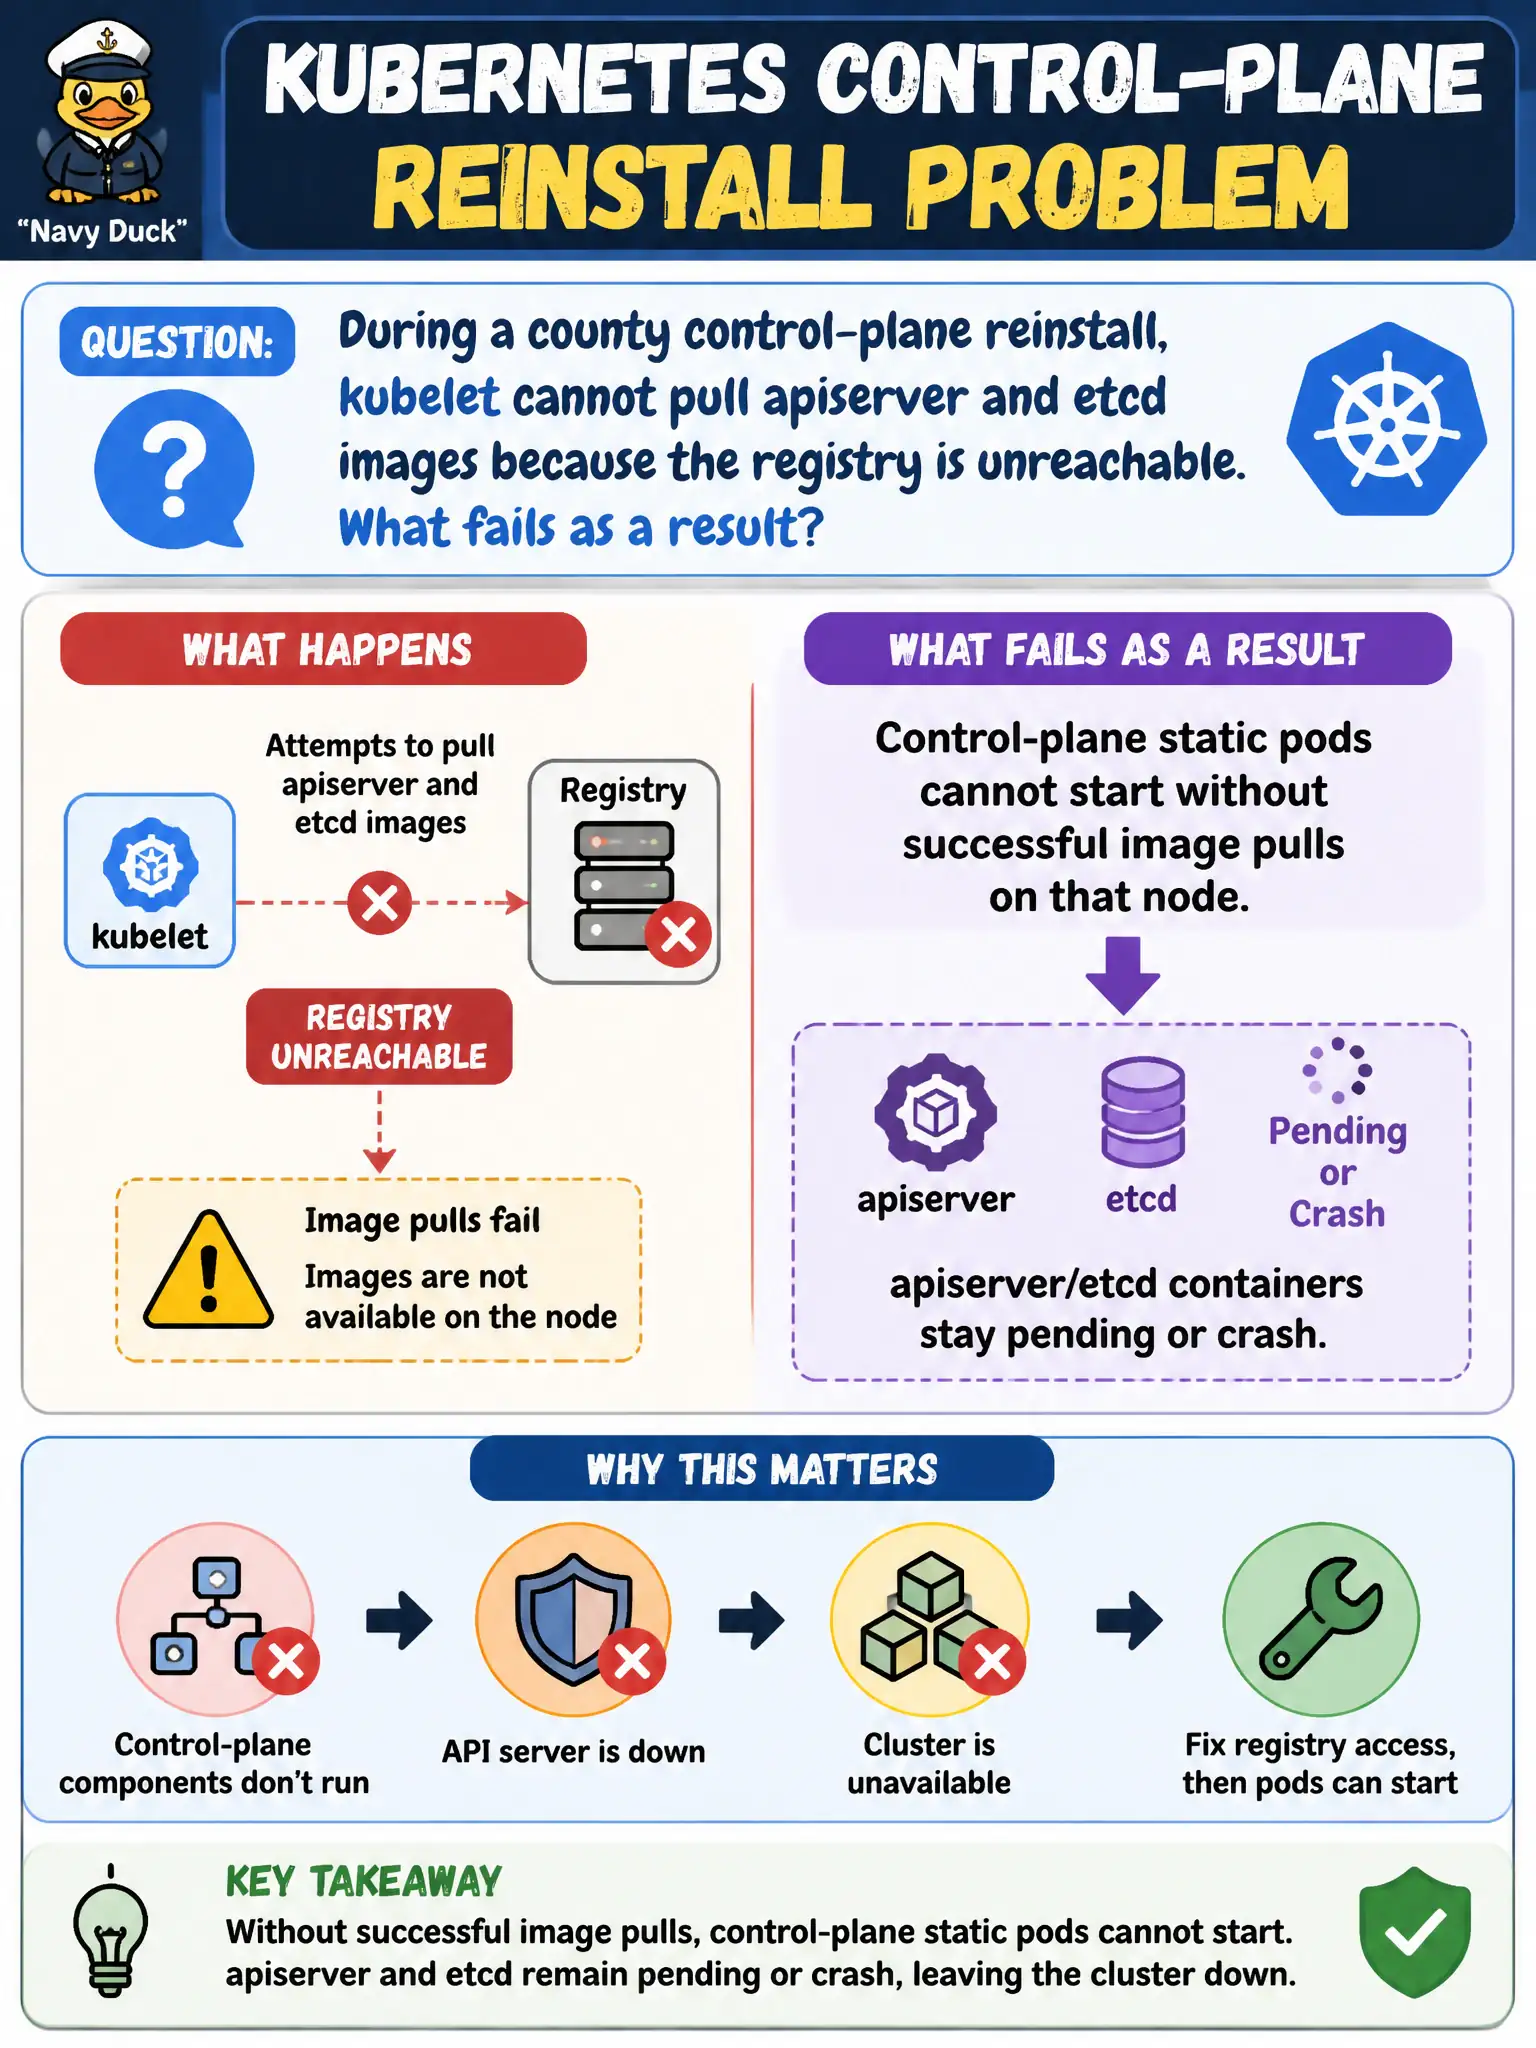
During a county control-plane reinstall, kubelet cannot pull apiserver and etcd images because the registry is unreachable. What fails as a result?
Select an answer to reveal the explanation.
Short Explanation
Static pods still need real container images from a registry—no image, no apiserver. A registry outage during reinstall leaves those control-plane pods stuck until pulls succeed.
Full Explanation
Control-plane static pods still need container images pulled from a registry or a pre-cached mirror. During a county control-plane reinstall, if kubelet cannot pull apiserver and etcd images because the registry is unreachable, those static pods cannot start—containers stay ImagePullBackOff, pending, or crash awaiting successful pulls. Registry reachability is therefore a hard dependency for bringing the control plane back. Image pull failures are not limited to Ingress TLS secrets; they directly block static control-plane pods that must run those images on the node. Registry outages do not automatically fall back to running control-plane binaries from CoreDNS ConfigMaps; that recovery mechanism does not exist. kubectl top cannot start apiserver static pods without container images; metrics tooling is unrelated to whether pulls succeed for static pods. Exam caveat: Air-gapped city clusters need a local registry or documented image mirrors in the install runbook. Distinguish ImagePullBackOff on static pods from apiserver logical errors once containers are actually running. Operational check: Restore registry, DNS, or proxy access from the control-plane node, verify crictl pulls succeed for required tags, watch static pods become Running, then validate kubectl against the restored municipal API.