
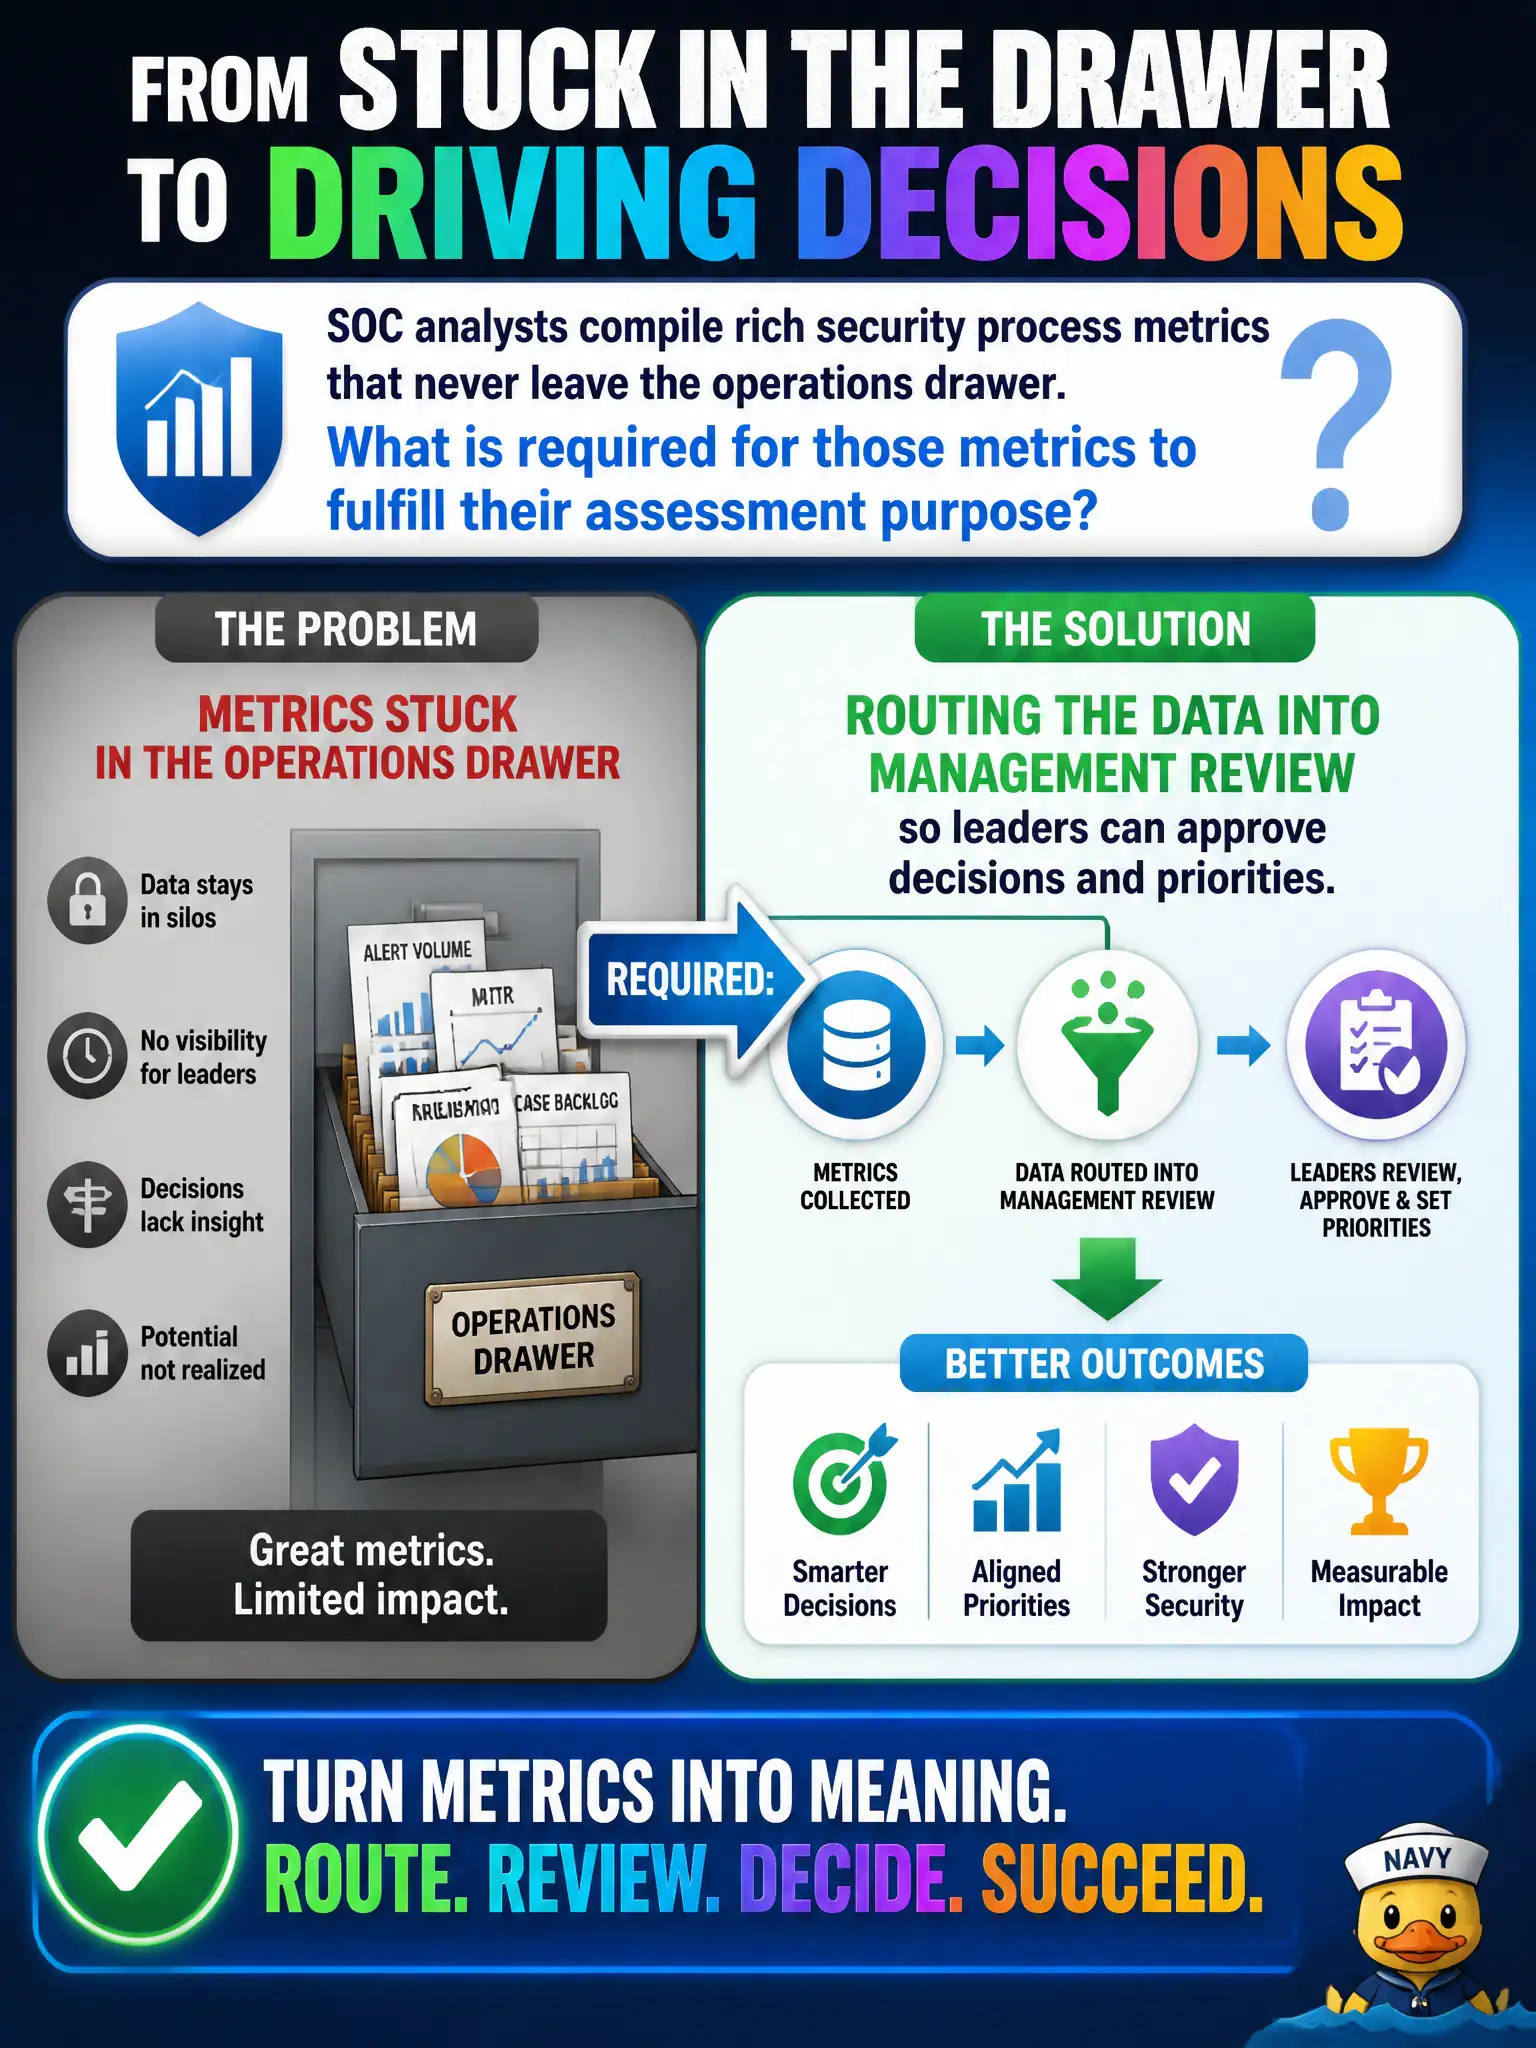
SOC analysts compile rich security process metrics that never leave the operations drawer. What is required for those metrics to fulfill their assessment purpose?
Select an answer to reveal the explanation.
Short Explanation
Metrics trapped in a SOC drawer are like unread lab results—useful only when a doctor acts. Push them into management review. Hiding them, dumping pcaps online, or swapping posters for data skips that step.
Full Explanation
Security process data supports governance only when management reviews and acts on it. SOC analysts who compile rich metrics that never leave the operations drawer have produced operational telemetry without fulfilling the assessment/governance purpose of informing decisions and priorities. Routing that data into management review so leaders can approve decisions, funding, and risk acceptance closes the loop Domain 6 expects between measurement and oversight.
Keeping metrics SOC-only so executives remain uninvolved intentionally breaks governance. Publishing raw packet captures to social media is an inappropriate disclosure that creates confidentiality and investigative harm without enabling sound management decisions. Replacing metrics with motivational posters substitutes slogans for evidence.
Exam caveat: Collection without management review is incomplete. Prefer answers that escalate process data into formal management review when the stem notes metrics trapped in operations.
Operational check: Establish a recurring management review agenda with KPI/KRI packs from the SOC, require documented decisions and priority changes, restrict raw telemetry to authorized channels, and track whether reviewed metrics actually drive funded actions.