
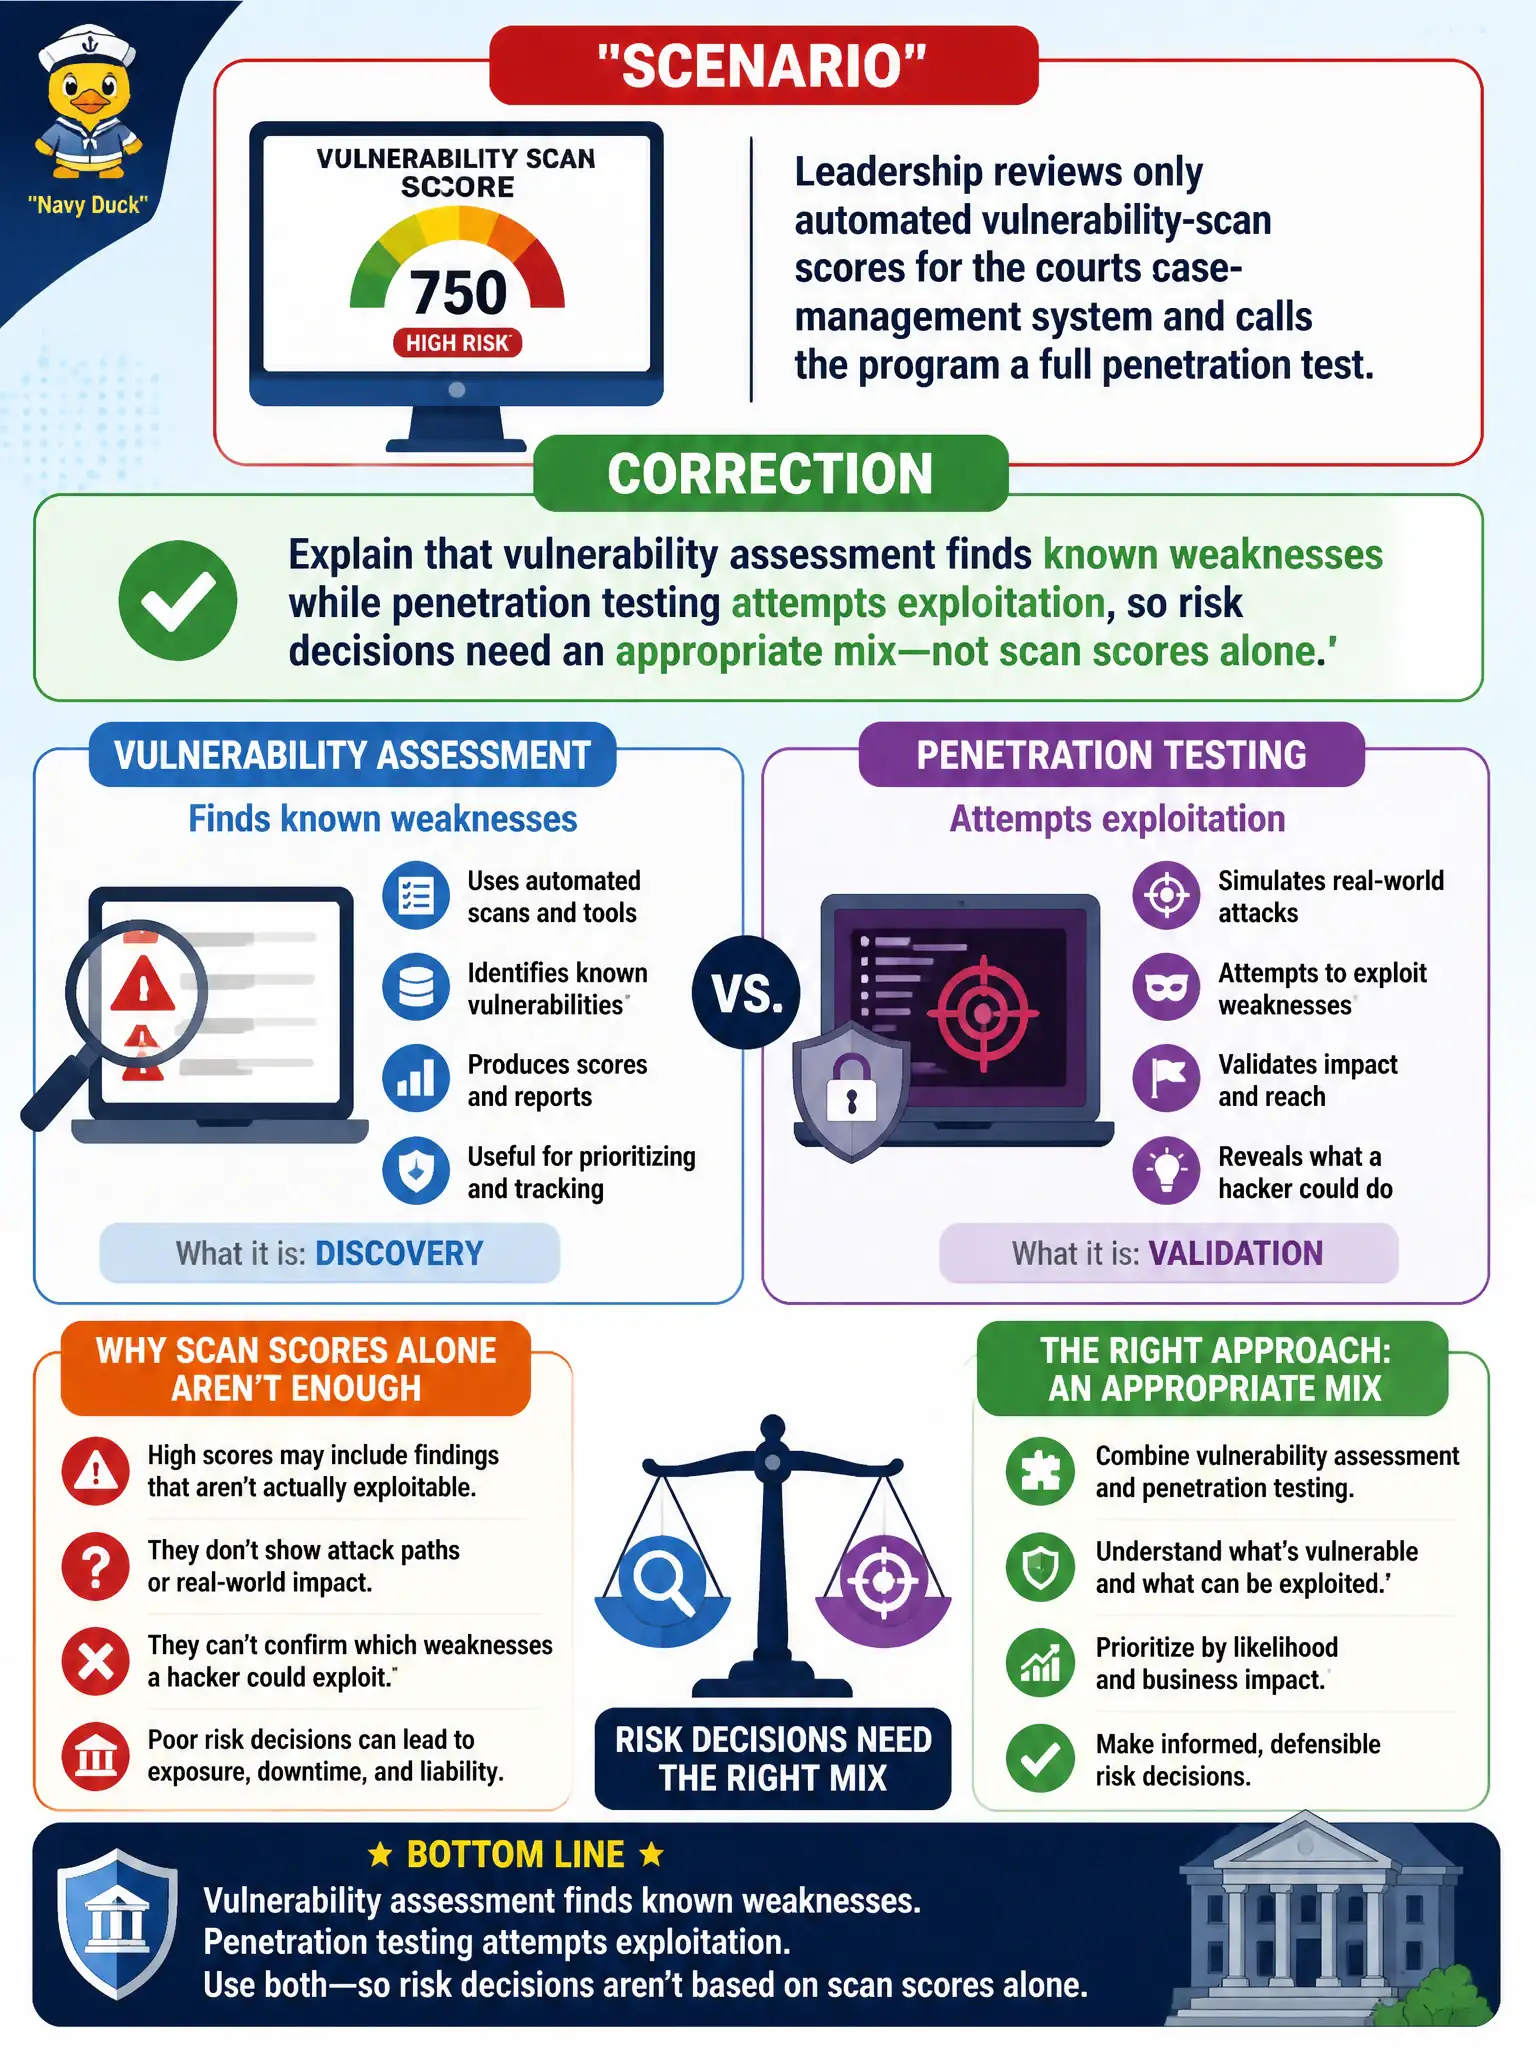
Leadership reviews only automated vulnerability-scan scores for the courts case-management system and calls the program a full penetration test. What correction should the assessor make?
Select an answer to reveal the explanation.
Short Explanation
A scan is a checklist of weak locks; a pentest tries the picks. Courts systems need the right mix for the risk—not a rebrand of scan scores. Treating them as identical, quitting scans, or dumping raw CVEs publicly misses the point.
Full Explanation
Vulnerability assessment and penetration testing are related but distinct Domain 6 control tests. Vulnerability assessment identifies known deficiencies (often via scanners and credentialed checks); penetration testing attempts exploitation under agreed rules to evaluate whether weaknesses can be abused and what impact follows. Leadership that reviews only automated scan scores for a courts case-management system and labels that a ‘full penetration test’ conflates the two. The assessor should correct that misunderstanding: risk decisions need an appropriate mix—scan-driven discovery plus adversarial exploitation where warranted—not scan scores alone rebranded as pentesting.
Agreeing that scanners fully replace adversarial testing in every context perpetuates the error and leaves exploitability, chaining, and business impact unvalidated for sensitive court data. Recommending never to scan again because scans and pentests are identical is doubly wrong: they are not identical, and scanning remains a valuable continuous discovery control. Advising publication of raw scanner CVE lists to the public as the only report creates unnecessary exposure and still fails to provide exploitation context or prioritized remediation guidance for the courts.
Exam caveat: Memorize the VA vs. pentest distinction. Exam items often punish equating CVSS lists with penetration testing. Prefer answers that explain the difference and call for an appropriate mix based on risk.
Operational check: Present leadership with a simple matrix—VA finds known issues; pentest validates exploitability—propose a risk-based annual pentest scope for the case-management system plus quarterly authenticated scanning, and never publish raw CVE dumps as the sole external report.