
Leadership hires an outside firm to review the city access-control policy implementation for gaps, without requesting a formal regulated attestation report. Which assessment type best fits?
Select an answer to reveal the explanation.
Short Explanation
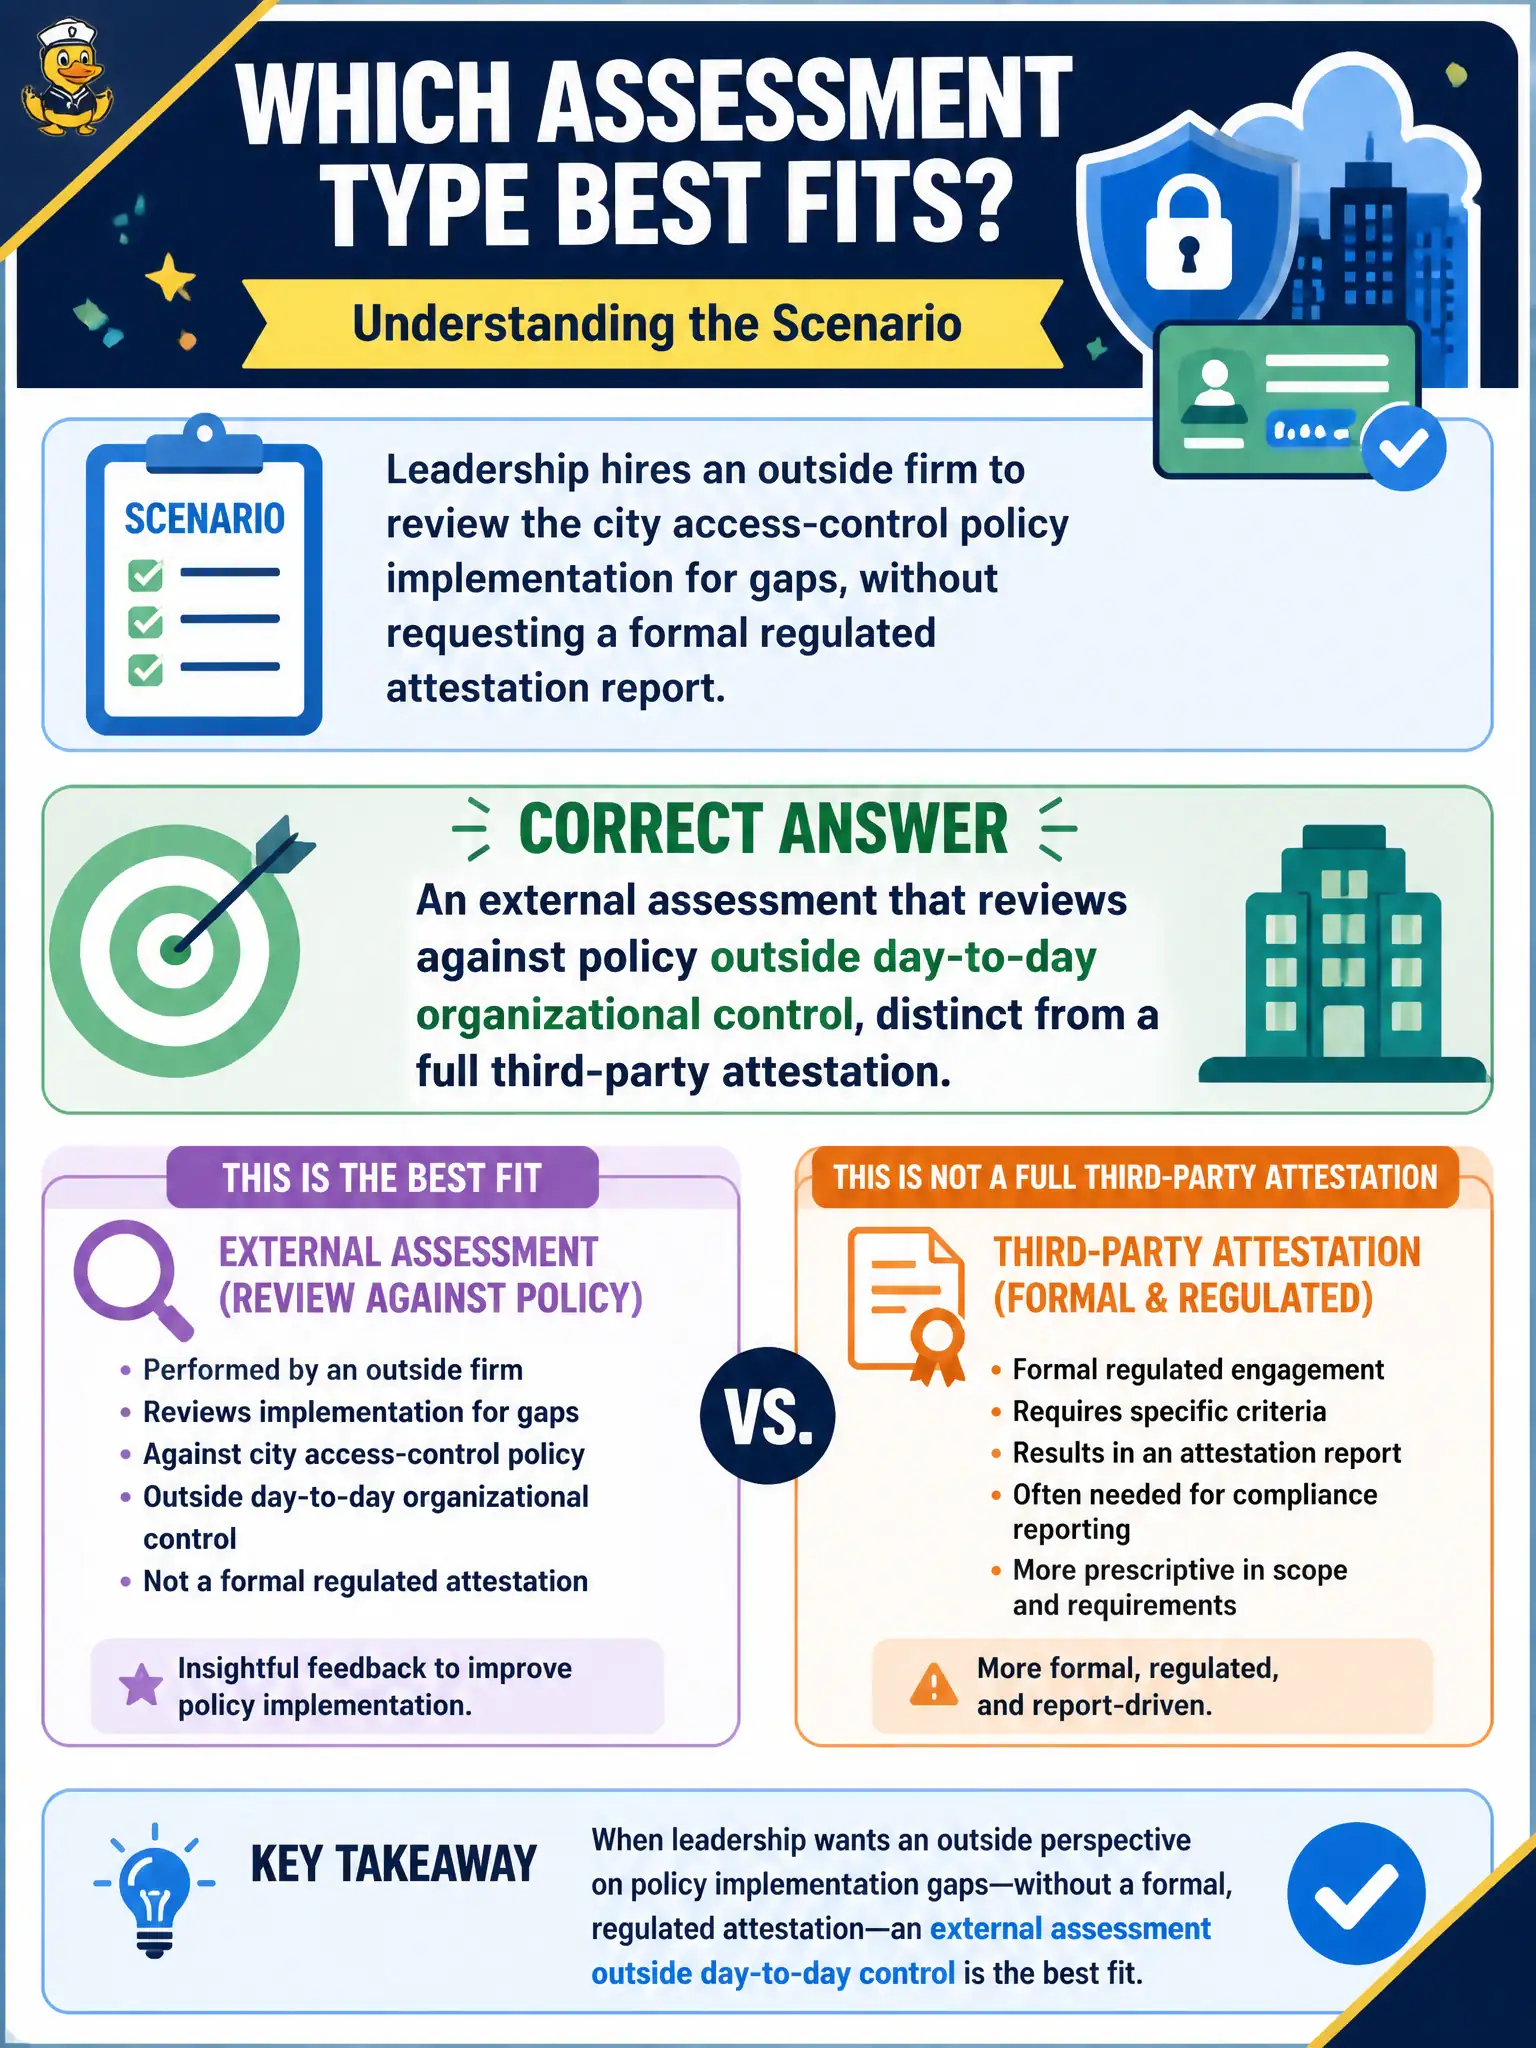
Somebody from outside the org walks the policy and points at gaps—but you are not buying a stamped PCI attestation. That is external assessment: fresh eyes, not necessarily a formal third-party cert letter.
Full Explanation
An external assessment uses people and processes outside day-to-day organizational control to review controls or policy implementation and report gaps. Hiring an outside firm to examine city access-control policy implementation—without buying a formal regulated attestation—fits that external-assessment pattern: independence and fresh scrutiny, distinct from a stamped third-party attestation artifact such as a PCI ROC.
Internal continuous control monitoring by city staff only contradicts the outside-firm element of the stem. Assuming any outsider automatically produces a PCI ROC confuses generic external review with a specific regulated attestation role and report. A tabletop exercise that never examines technical or administrative controls is a discussion drill, not a policy-implementation assessment by an external reviewer.
Exam caveat: “external” ≠ “attestation”; CISSP expects you to separate independence of the reviewer from whether a formal third-party opinion letter is in scope. Operational check: write a statement of work that clarifies deliverables (gap report versus attestation), protect production data during the review, track remediation of findings, and decide separately whether a regulated attestation is later required for payment or other frameworks.