
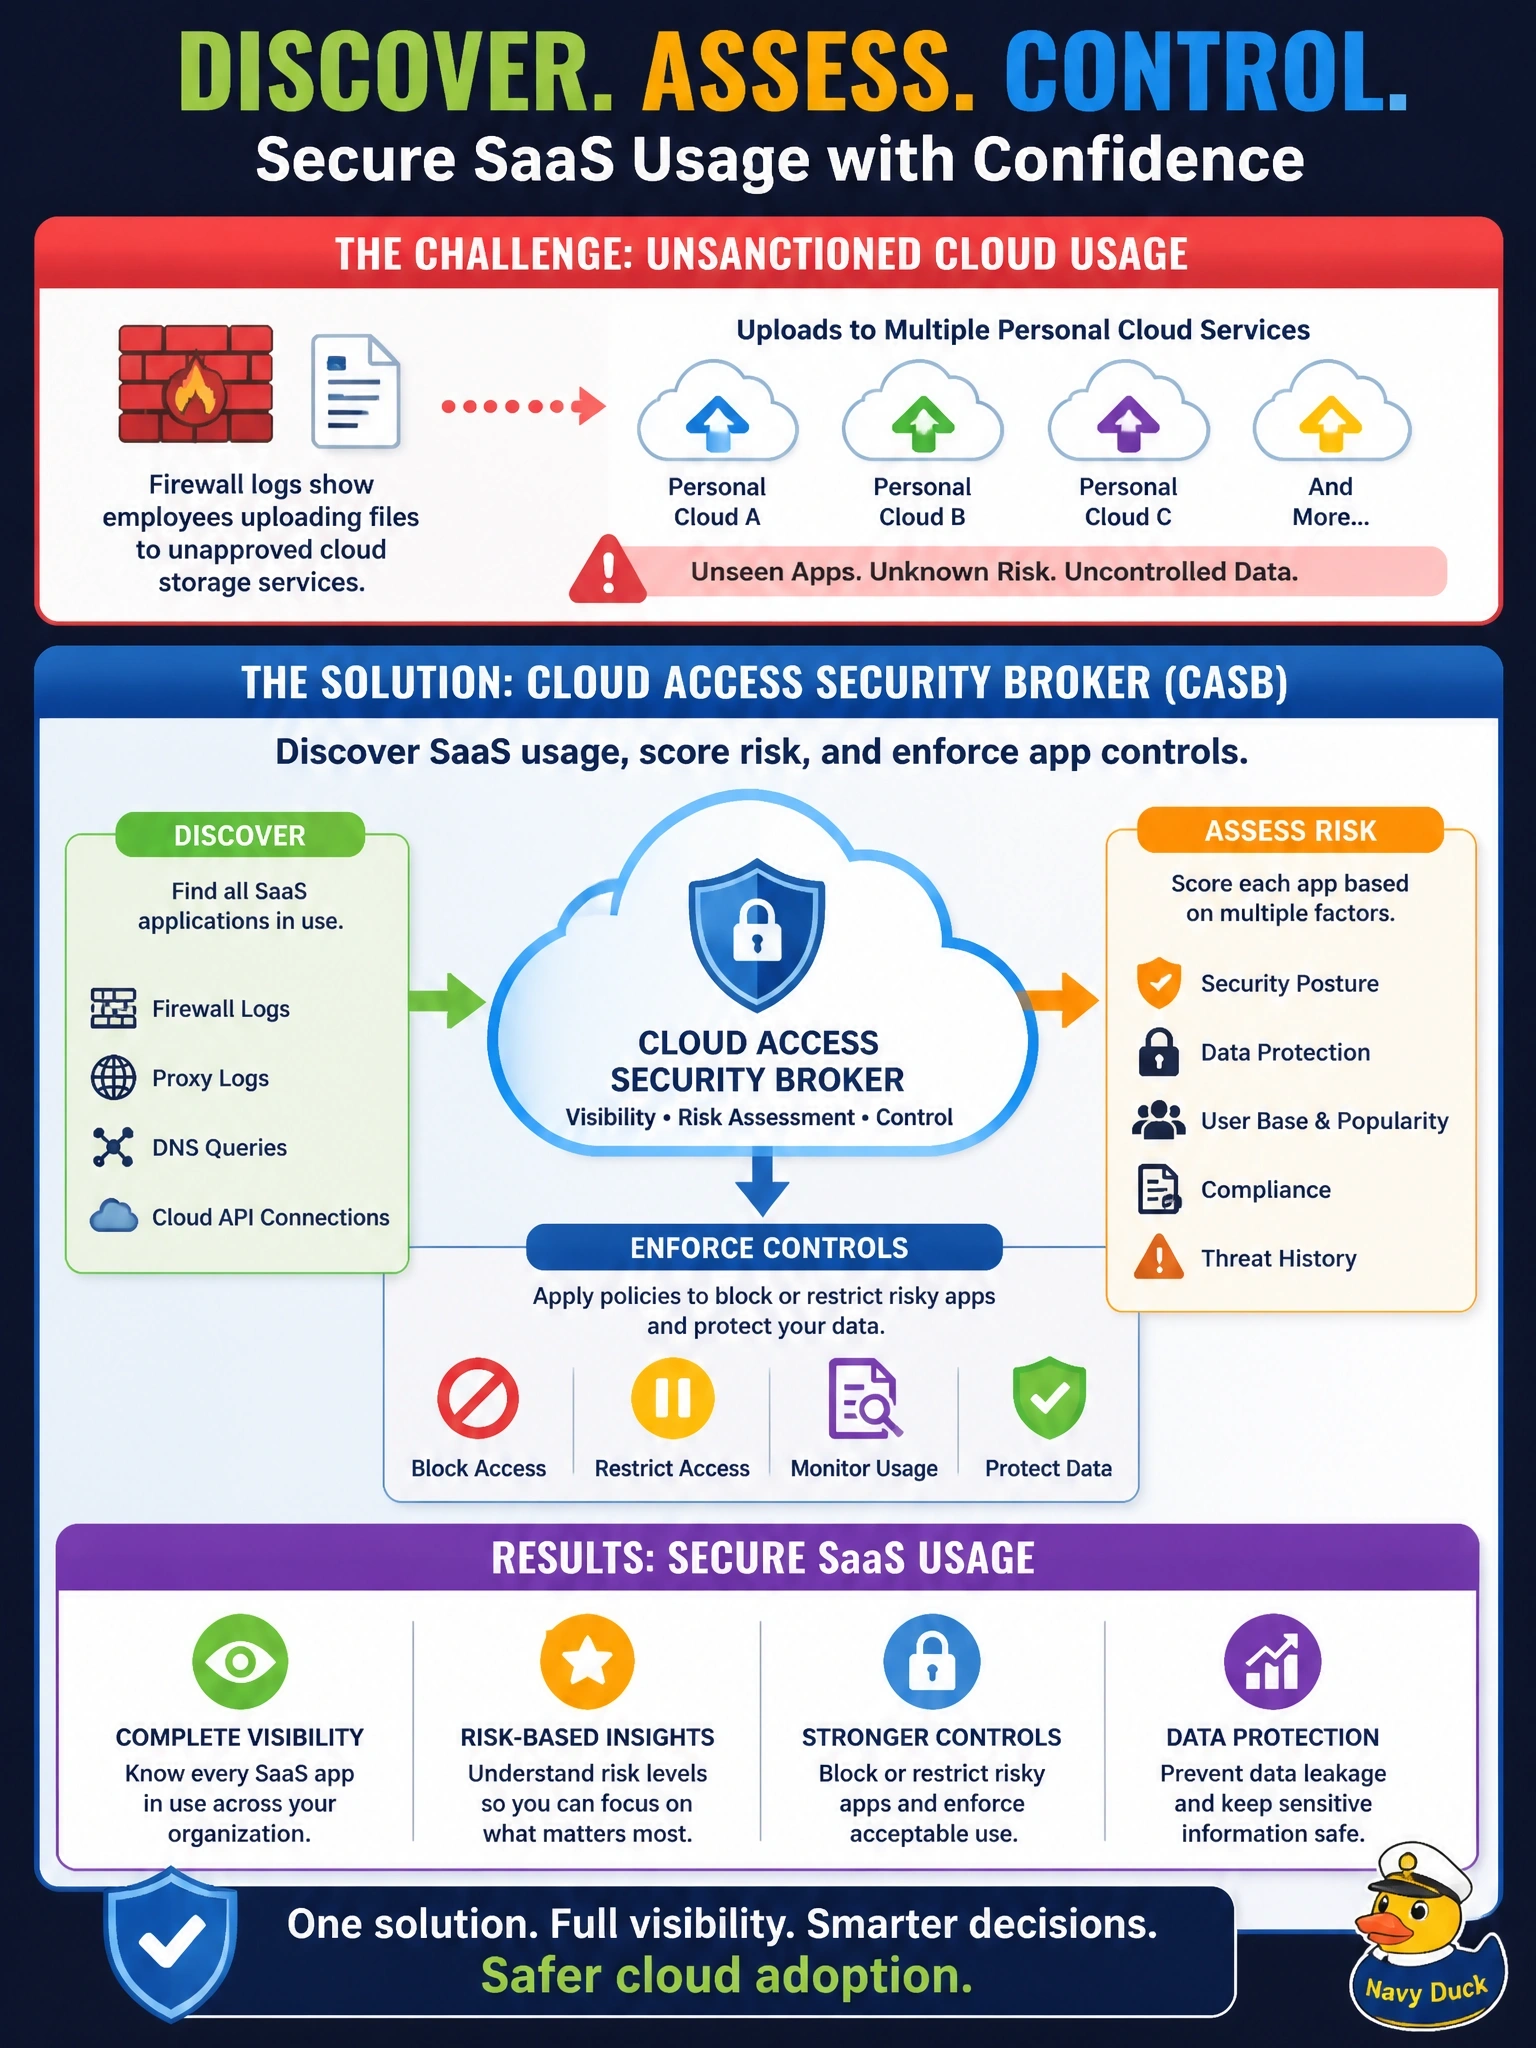
Firewall logs show employees uploading files to several personal cloud storage services the company never approved. Leadership wants the security team to discover which SaaS applications are in use, rate each one's risk, and then block or restrict the risky ones. Which type of security solution is designed for this requirement?
Select an answer to reveal the explanation.
Short Explanation
Shadow IT is like finding out half your staff rent their own storage units across town. A CASB is the tool that finds those units, tells you which ones are risky, and lets you lock them out. The trap is grabbing a cloud tool that protects your infrastructure — this problem is about other people's SaaS apps your users wander into.
Full Explanation
A cloud access security broker sits between users and cloud services to provide visibility, data security, threat protection and compliance for SaaS use. Its shadow IT discovery function analyzes proxy, firewall or DNS traffic to identify which cloud applications users reach, attaches a risk rating to each based on attributes such as data handling and certifications, and then lets administrators sanction, restrict or block applications. That discover, assess and control cycle is exactly what leadership asked for. A web application firewall protects the company's own web applications from inbound attacks such as injection; it has no view of employees' outbound use of third-party SaaS. A cloud workload protection platform secures the organization's own compute workloads in IaaS, including VMs and containers, and does not inventory or govern external SaaS applications. A cloud security posture management tool audits the configuration of the company's own cloud accounts against best practice, which again says nothing about unsanctioned apps employees use. Exam caveat: in Cisco's current portfolio, Secure Access includes CASB functions such as app discovery and control, so expect the capability to appear under that product name. Operational check: review the discovered application report, confirm risk scores for the storage apps found in the logs, and apply a block or restrict rule to the unsanctioned ones.