
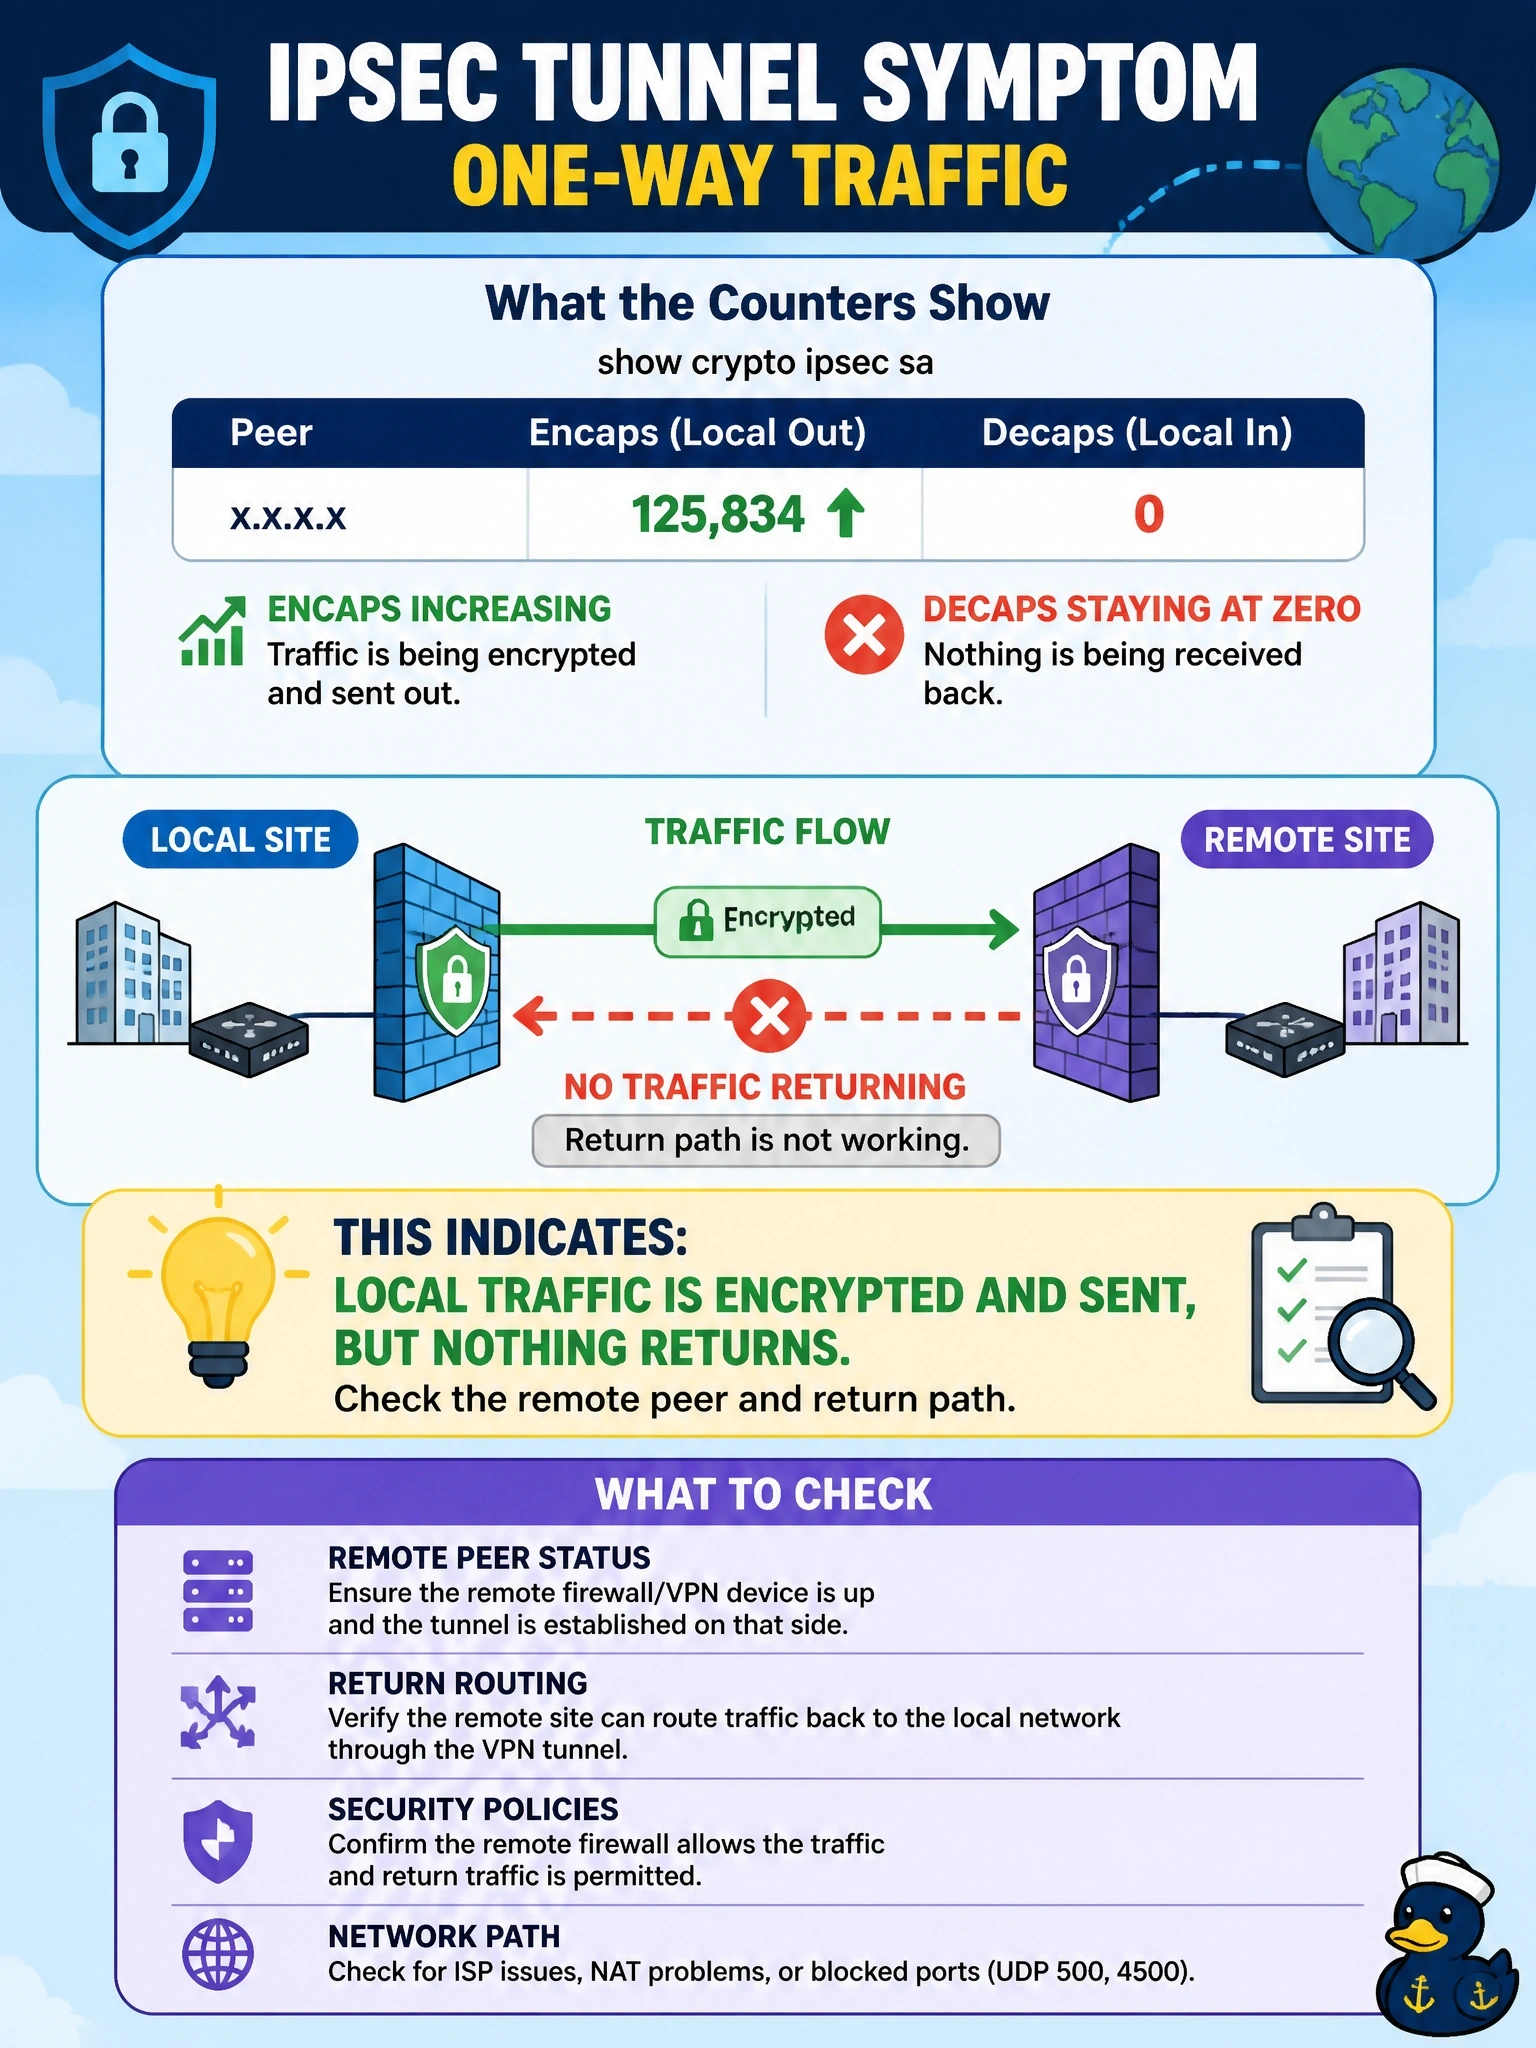
On a Cisco Secure Firewall (FTD), 'show crypto ipsec sa' for a site-to-site tunnel shows the encaps counter increasing steadily while the decaps counter stays at zero. Users at both sites report no connectivity. What does this indicate?
Select an answer to reveal the explanation.
Short Explanation
Think of encaps and decaps like letters sent and letters received. You're mailing plenty, but your mailbox is empty. That points you to the other end or the road back, not to your own outbound setup.
Full Explanation
The IPsec security association counters show packets encrypted and sent, encaps, and packets received and decrypted, decaps. A rising encaps count proves that the local FTD is matching outbound traffic to the security association, encrypting it, and transmitting it, so local NAT exemption and outbound policy are working for that flow. A decaps count of zero means no valid encrypted packets are arriving for that security association. The fault therefore lies on the remote side or in the return path: the remote peer may not be decrypting, may be dropping traffic through its own access control or NAT, may lack a route back, or an intermediate device may drop returning ESP. A failure to decrypt locally would normally show decryption error counters, not a silent zero with no arrivals. A failing local NAT exemption would stop traffic from matching the security association, leaving encaps flat rather than increasing. A security association with counters cannot exist without a completed Phase 1, because the IPsec security association is negotiated under the IKE security association. Exam caveat: always check the counters on both peers; the remote side's view, decaps rising and encaps flat, confirms the direction of the fault. Operational check: on the remote FTD, run packet tracing from its inside host toward the local network and review its security association counters and logs.