
A factory edge switch is supposed to attach as NPV. Its uplink to the core came up as an E port, and the edge requested its own domain ID. NPIV is already enabled on the core. What is the edge missing?
Select an answer to reveal the explanation.
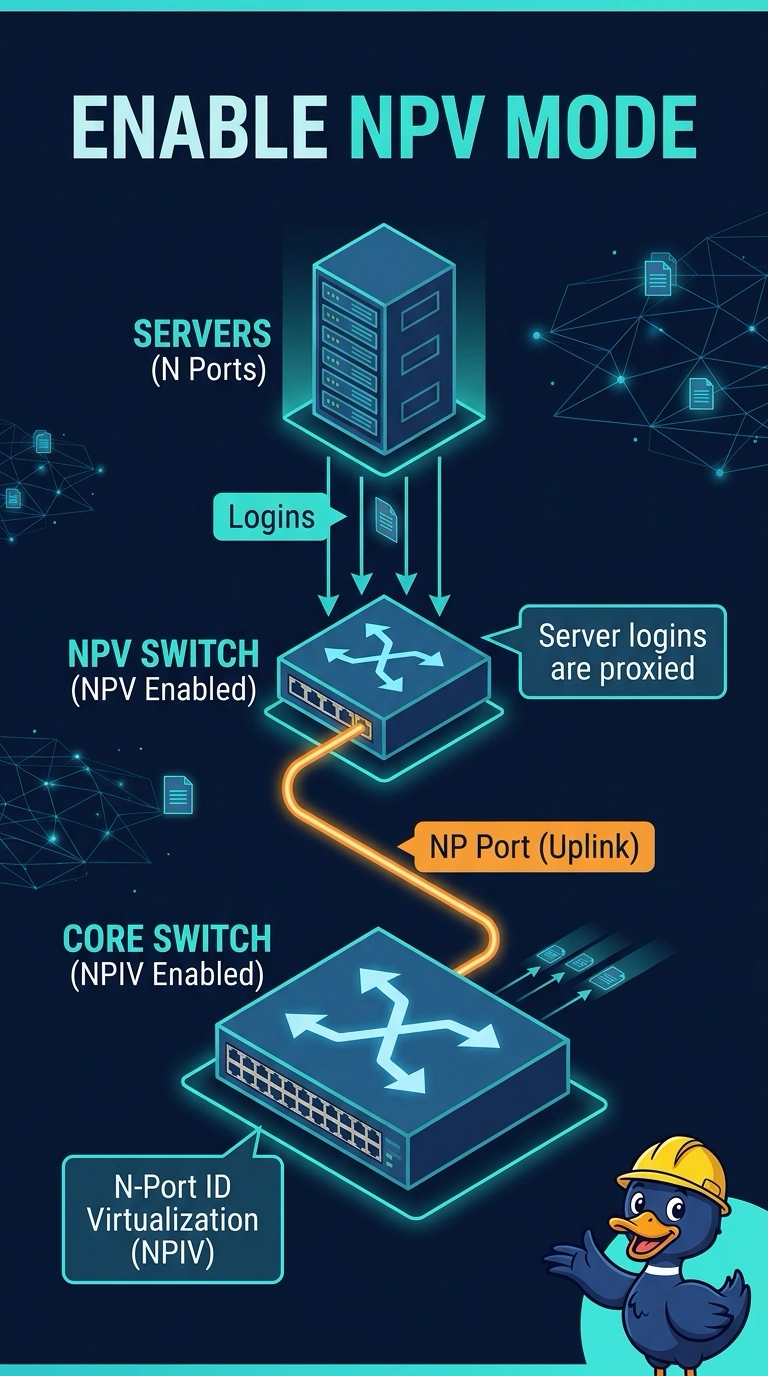
Short Explanation
Your satellite office printed its own street grid instead of using downtown's. An NPV edge proxies server logins on an NP port and does not take a domain ID, but this uplink came up as an E port because NPV mode is off.
Full Explanation
NPV mode changes the edge switch so its uplink to the core is an NP port and the downstream server FLOGIs are forwarded as FDISCs. The core, which already has NPIV, assigns the FCIDs. Without NPV on the edge, the uplink negotiates as an E port and the edge asks for a domain ID of its own, which is what the factory is seeing. Giving it another domain ID keeps it a full switch. That is the opposite of an NPV edge. Default-zone permit lets unzoned devices talk. It does not turn an E port into an NP port, and it is not required for FLOGI. An SD port is a SPAN destination. Replacing the uplink with one would remove the path to the core. Caveat: after NPV is enabled, server logins still fail if the core NPIV feature is later turned off. Here the core is already correct. Operational check: confirm the edge reports NPV mode and the uplink is an NP port, then log a server in and confirm it receives an FCID from the core's domain. Enabling NPV on the edge is disruptive to the logins that edge already has. Do it in a window, then confirm each server receives an FCID from the core domain rather than from the edge.