
A factory IoT network converts an edge MDS to NPV mode so it will not take a Fibre Channel domain ID. Hosts behind that edge never complete FLOGI. NPIV is disabled on the core switch. What must change on the core?
Select an answer to reveal the explanation.
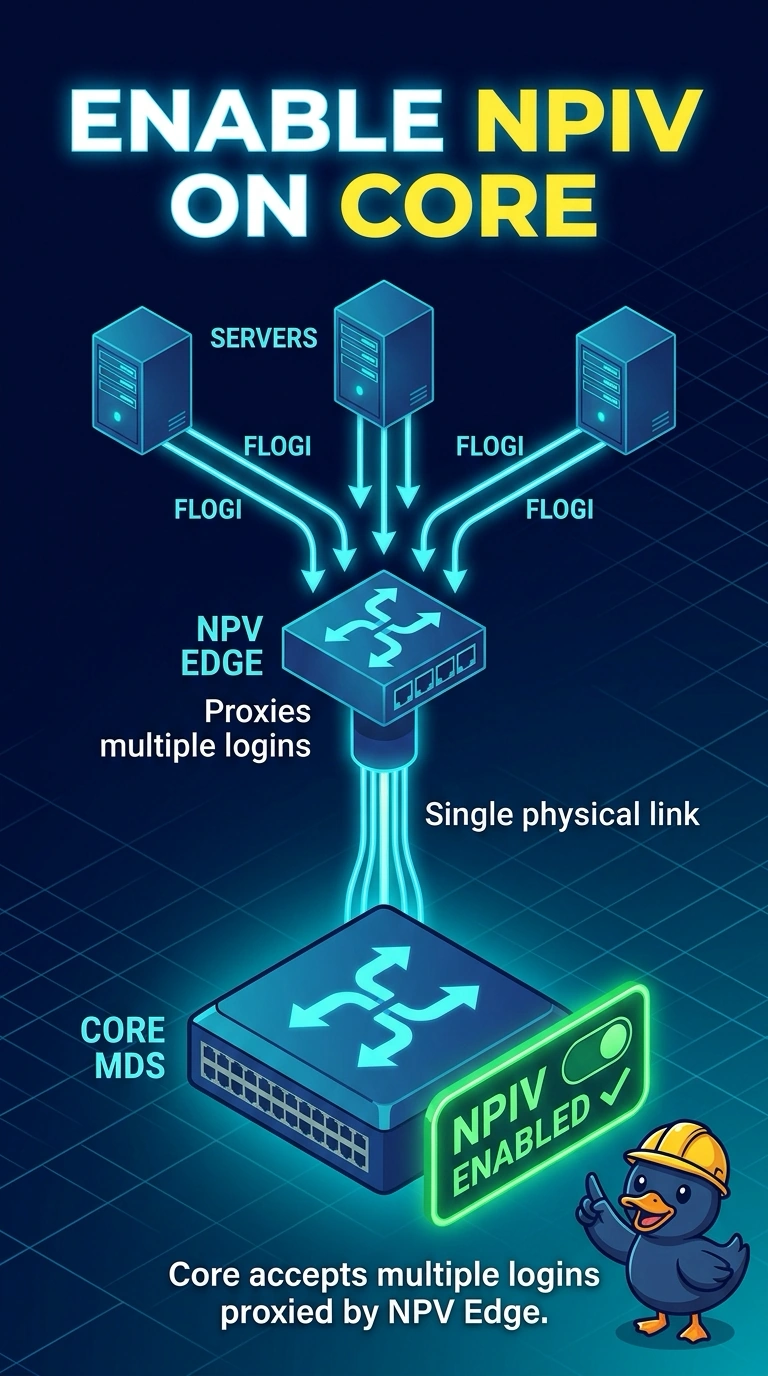
Short Explanation
NPV is a coat check that borrows IDs from the core. You turn on NPIV at the core or those borrowed logins are refused and the factory hosts never finish FLOGI. Handing the edge its own domain ID throws away the reason you chose NPV.
Full Explanation
An NPV edge does not join the fabric as a switch and does not consume a domain ID. It proxies host FLOGIs as additional logins on its NP port. The upstream switch can accept those extra logins only when NPIV is enabled. With NPIV left off, the factory core refuses the proxied logins and the hosts never get FCIDs. Enabling NPIV on the core is the change that matches the design. Assigning a domain ID to the NPV edge undoes NPV. The edge would have to be a full fabric switch again, which reintroduces the domain-ID consumption the team was trying to avoid. CFS distributes selected configuration. It does not filter NPIV logins, and disabling it will not make the core accept them. An empty zoneset does not enable NPIV, on the edge or on the core. Caveat: the NP-to-F link also has to be up, and zoning on the core still has to include the host pWWNs or the logins succeed and the targets stay dark. Operational check: enable NPIV on the core, confirm the edge NP port is up, and verify the hosts appear in the core FLOGI and name-server tables.