
A retailer vPC peer-link fails while the keepalive stays up. The secondary suspends its vPC member ports. A single-attached server on the secondary still shows link up, and it cannot reach anything on the primary. Why is that server port still forwarding at layer 1?
Select an answer to reveal the explanation.
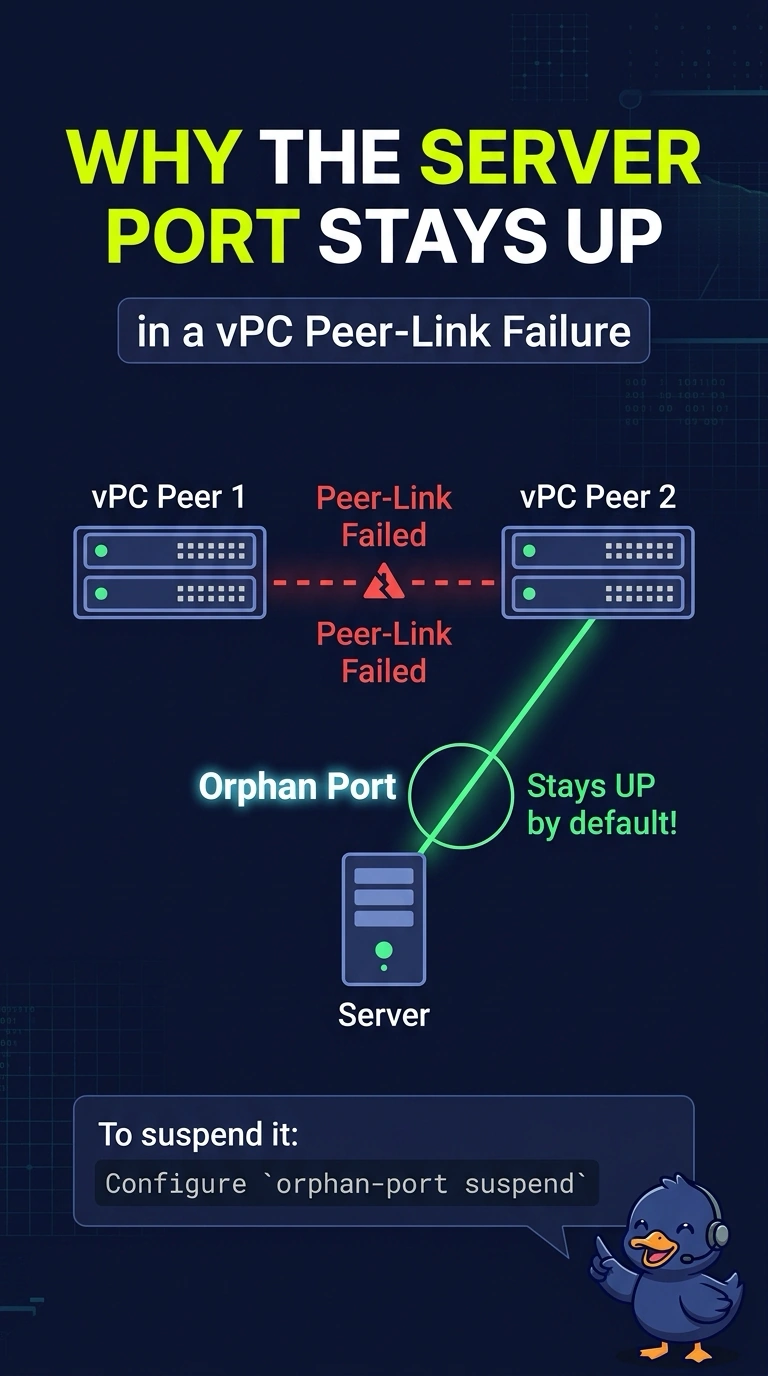
Short Explanation
The side door of the closed shop is still unlocked. When the peer-link fails and the keepalive is up, the secondary suspends vPC member ports and does not suspend an orphan port unless you configured that. Your single-attached server is that orphan, so the link stays up while the path across the peer-link is gone.
Full Explanation
An orphan port is a port that is not a vPC member, typically a single-attached host, and that carries a vPC VLAN. On a peer-link failure with the keepalive still up, the secondary suspends its vPC member ports so those port-channels do not forward on both peers. Orphan ports stay up by default. The host looks connected and cannot cross to the primary, because the peer-link is the path that would have carried that traffic and the secondary also shuts down the SVIs for the vPC VLANs. Configuring orphan-port suspend on that interface makes the secondary shut it with the member ports, which lets a dual-homed NIC fail over. The keepalive is up, so this is not a keepalive failure, and a keepalive failure is not what keeps an orphan port up. The secondary does not keep member ports forwarding in this failure. The stem already says those ports are suspended. Peer-gateway lets a peer route for the other peer's MAC. It is not the feature that decides whether an orphan port stays up. Caveat: if the keepalive were down too, the secondary would assume the primary is gone and would keep its own member ports up. That is a different failure. Operational check: show the orphan ports on the secondary during a peer-link test and confirm this server is on that list.