
A national retailer wants a daily record of which hosts sent the most traffic toward a payment VLAN, including byte counts, without copying every frame to an analyzer. Which record matches?
Select an answer to reveal the explanation.
Short Explanation
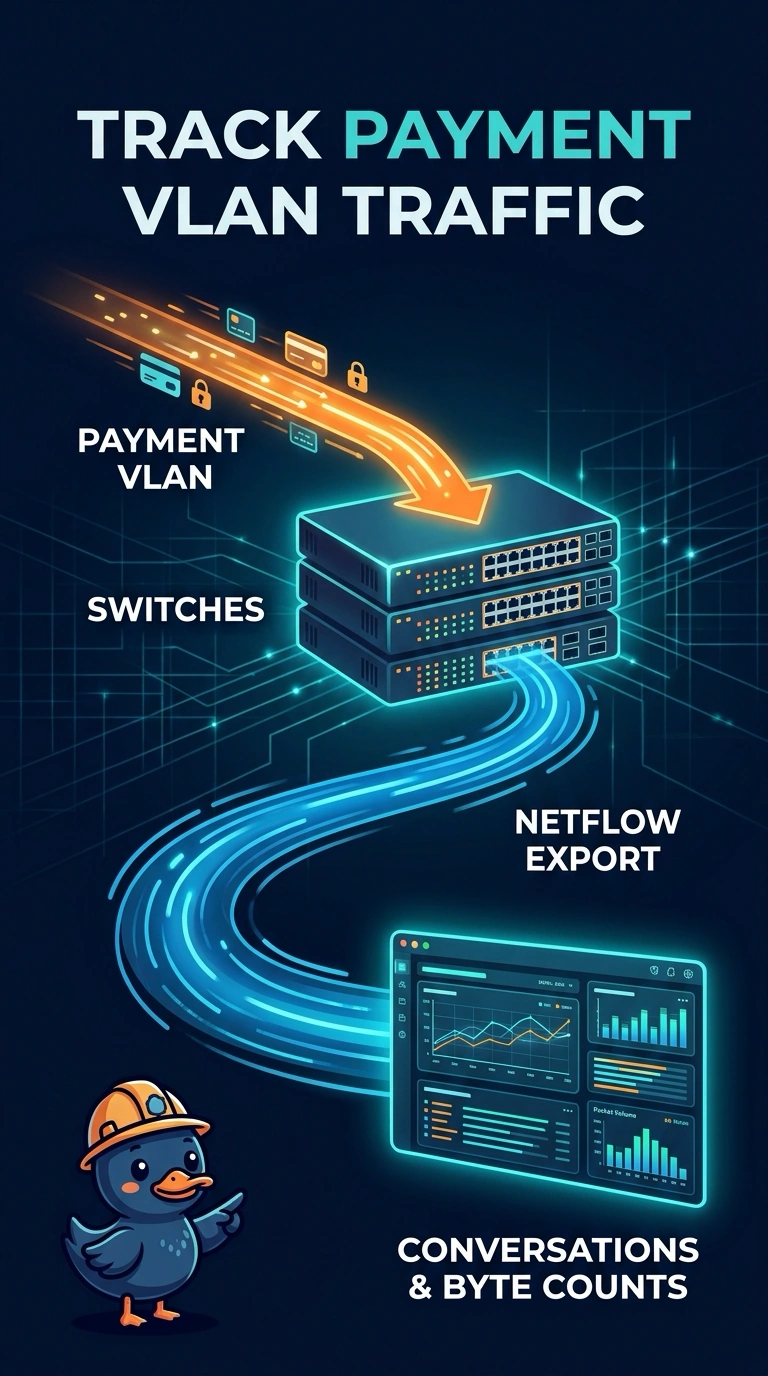
SPAN is a copy machine for frames, and NetFlow is the tally sheet. You want host conversations and byte counts for a day, so a flow export gives you that record without copying every frame to an analyzer. The routing database and a checkpoint do not store those totals.
Full Explanation
NetFlow, and the flow records NX-OS can export, summarize conversations: who spoke to whom, on which ports, and how many packets and bytes moved. That is the daily top-talker record the retailer wants, and it does not require a copy of every frame. SPAN mirrors frames from a source port or VLAN to an analyzer. It is the right tool when the payload or a malformed frame has to be seen, and it is a poor way to rank a whole day's byte counts because the analyzer must receive the traffic itself. OSPF link-state advertisements describe topology and subnets. They do not contain per-host traffic counters. A configuration checkpoint is a snapshot of the running configuration. Counters are operational data, and they are not written into the configuration file. Caveat: flow records sample or summarize, so they will not prove the contents of a single suspicious payload the way a targeted SPAN capture will. Operational check: confirm the flow export is leaving the switches toward the collector, then rank the payment VLAN conversations by bytes for the collection window.