
A campus access point that should tunnel clients to the controller was set to bridge mode. Clients no longer land on the controller's client VLAN. What mode should it use?
Select an answer to reveal the explanation.
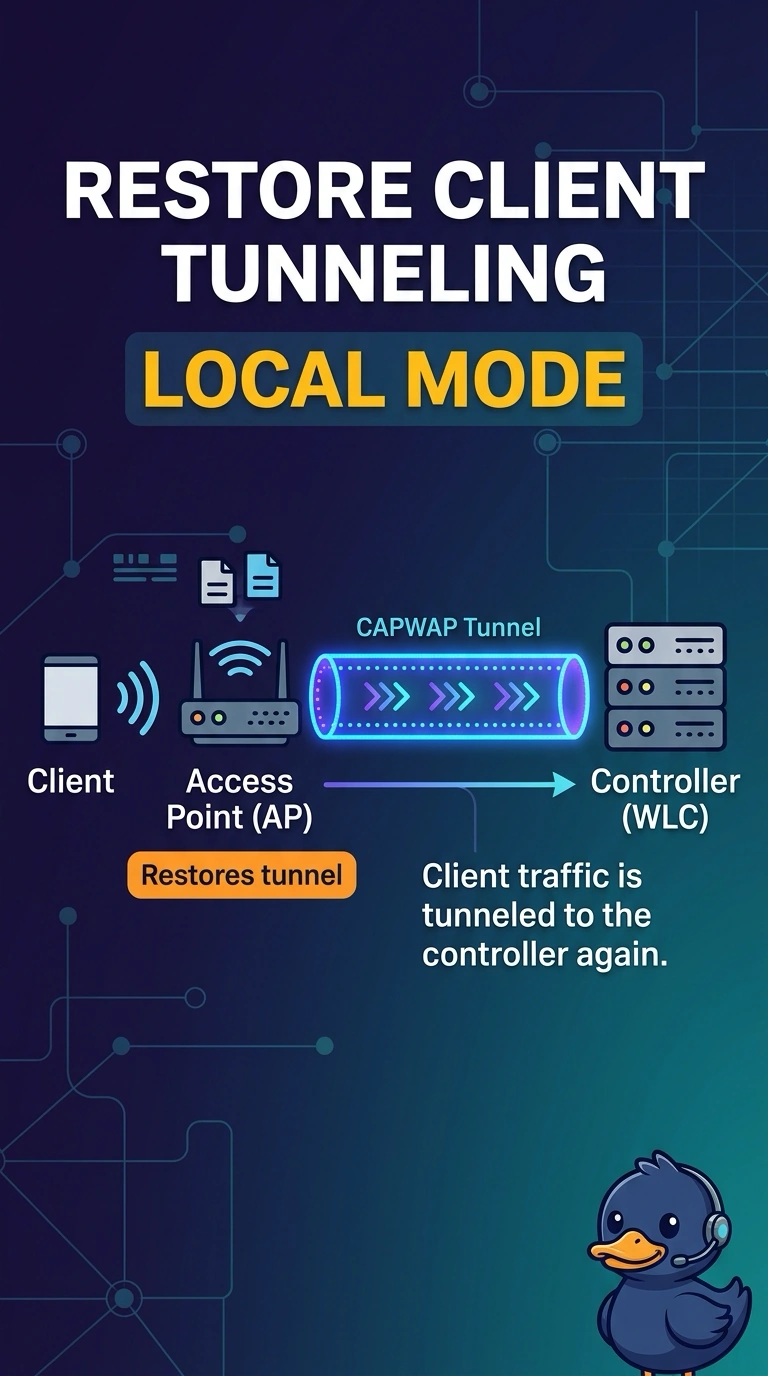
Short Explanation
The access point stopped carrying your clients back to the controller because it was told to bridge them instead. Put it back in local mode. A capture mode will not rebuild that tunnel, and hiding the name will not either.
Full Explanation
Local mode tunnels client traffic to the controller, which is where this campus VLAN lives. Bridge mode keeps client traffic off that tunnel, so clients no longer land on the controller's VLAN. The access point should be put back in local mode. Sniffer mode captures and does not serve clients, so it does not tunnel them to the VLAN. Monitor mode scans and does not serve clients between scans. Hiding the SSID on a bridge does not restore the controller tunnel. The mode is the tunnel decision, not the beacon flag. A campus access point was set to bridge mode and no longer tunnels clients to the controller. It should be local mode. Check one live client after the change and leave the rest of the floor alone until that client matches the result you expected. Exam caveat: a FlexConnect access point that is supposed to switch locally at a branch should not be swept up in this fix. This stem is a campus access point whose VLAN lives at the controller. Operational check: set local mode, rejoin the access point, and confirm a client address comes from the controller's VLAN.