
New access points get an address and never join. They have no static controller and no DHCP option 43. A lookup of CISCO-CAPWAP-CONTROLLER fails because the access points have no DNS domain, and the record exists only under the corporate suffix. What is missing?
Select an answer to reveal the explanation.
Short Explanation
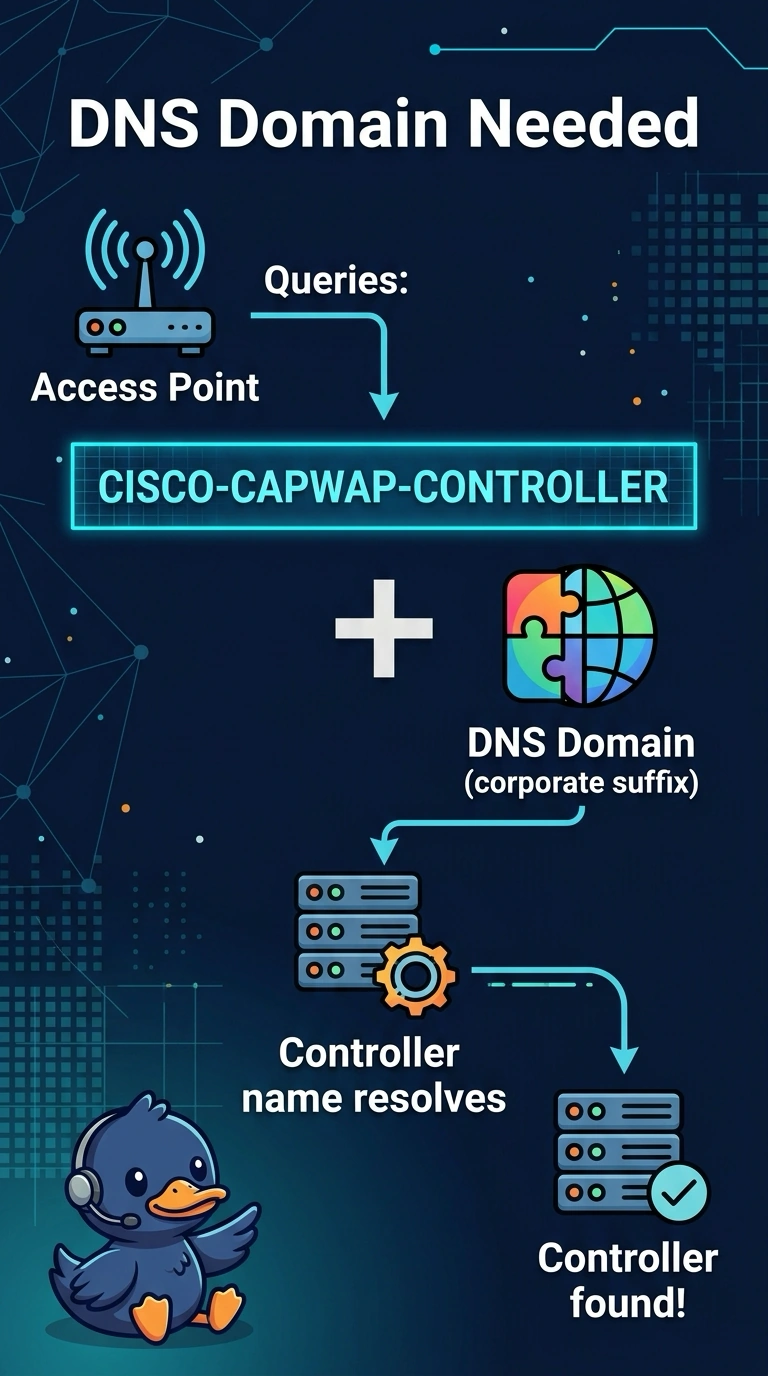
Your access points are looking up a short name, but they have not been told which DNS domain it belongs to. The record is under the corporate suffix, so give them that DNS domain; sniffer mode will not complete the name.
Full Explanation
DNS discovery looks up CISCO-CAPWAP-CONTROLLER. With no static controller and no DHCP option 43, that lookup is the remaining method, but it fails because the access points have no DNS domain and the record exists only under the corporate suffix. Supplying the DNS domain lets the name resolve under that suffix. Sniffer mode does not supply a DNS domain during the join, so it cannot fix the lookup. A hidden SSID is a beacon setting; it is not required for a resolver to answer the controller-name query. A client exclusion does not add the corporate suffix to an access point. The key distinction is that the missing information is the DNS domain, not a wireless setting or a client policy. Exam caveat: DHCP option 43 could also provide controller discovery information, but it is absent in this scenario. For a practical check, set the domain, renew one access point, confirm its controller-name lookup succeeds against the resolver it received, and verify that it joins before changing the rest.