
A Catalyst 9800 shows the correct time from NTP. New access points fail the secure join and their logs show the time as years off. The access points are not configured with a time source. What is missing?
Select an answer to reveal the explanation.
Short Explanation
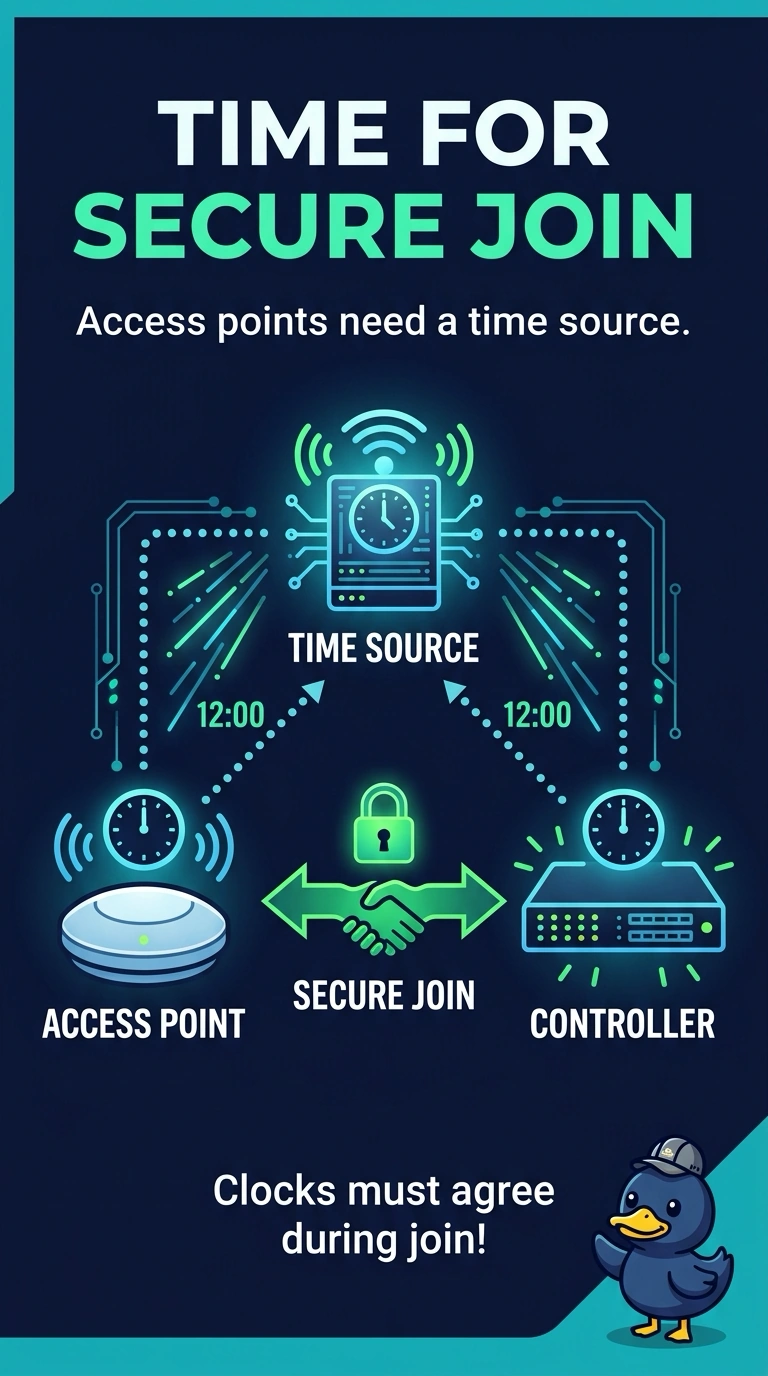
The controller knows what time it is. The new access points do not, and the secure join cares about both clocks. Give your access points a time source, because a faster beacon will not set a clock that is years off.
Full Explanation
The secure join checks certificates against the clock. A controller on NTP can still reject access points whose own clocks are years off, because the access point side of the check fails. These access points have no time source configured. They need one, typically NTP, so their clocks agree with the controller. The beacon interval does not carry a usable clock set. Shortening it does not move a clock that is years wrong. The guest VLAN is a client network. An access point does not use it as an NTP server, and a VLAN number is not a time source. A higher data rate changes modulation. It does not correct a clock. Exam caveat: the access point has to be able to reach the NTP server from the VLAN it uses before it is fully joined, or you set time another way the platform supports. Naming an NTP server it cannot route to leaves the clock wrong. Operational check: compare an access-point clock with the controller, give the access points a reachable NTP server, and confirm the next join succeeds.