
An IP camera on a plant WLAN is identified by profiling. The team wants only that camera type placed on a camera VLAN, and they do not want the WLAN disabled. Where does that per-device rule belong?
Select an answer to reveal the explanation.
Short Explanation
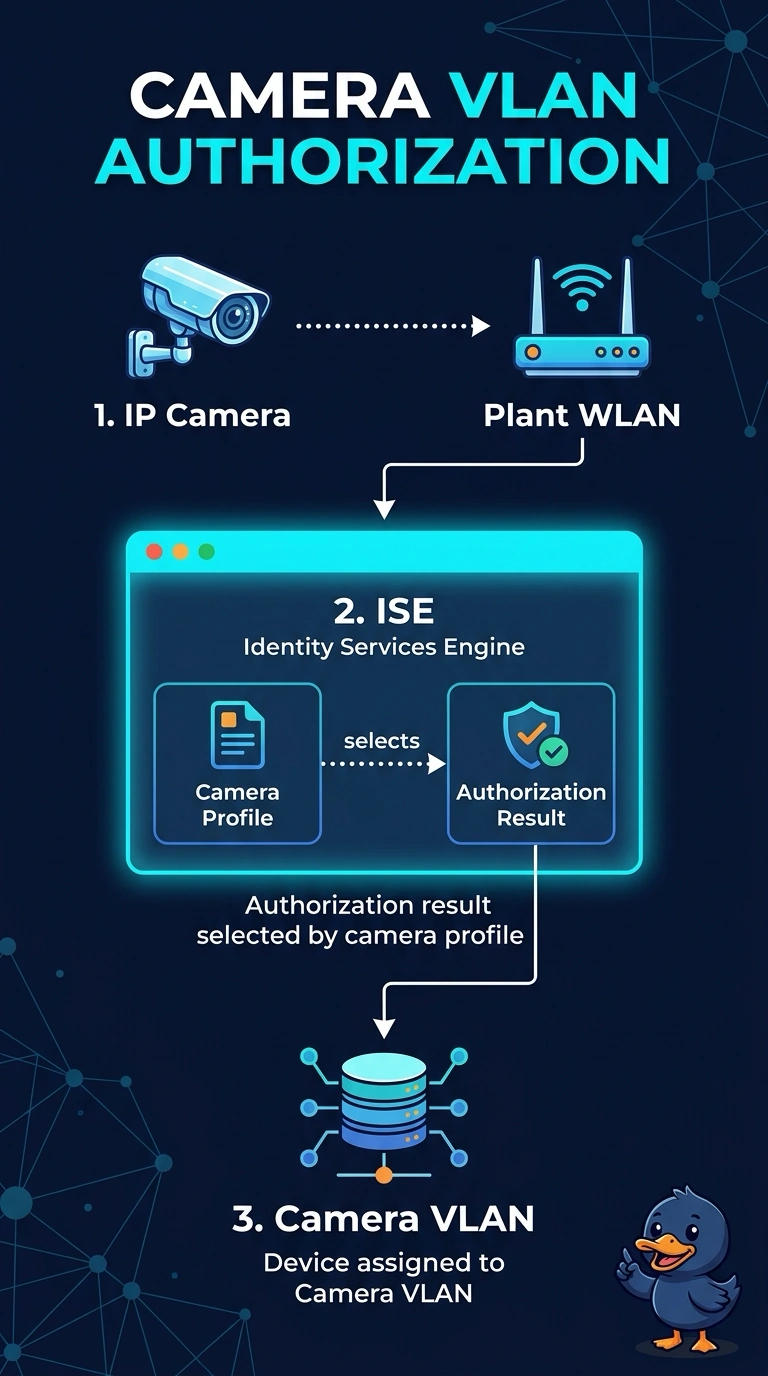
Profiling already told you this device is a camera. The rule that parks only that type on the camera VLAN belongs in ISE, as an authorization result. A short lease is not an identity.
Full Explanation
ISE profiling classifies the device, and an authorization rule can match that profile and return a VLAN or an ACL for the camera only. The WLAN stays up for everything else. That is the per-device rule the plant asked for, and it belongs on ISE. An RF tag groups radio profiles for access points. It does not read a profiling result or map a camera to a VLAN based on signal strength. A sniffer access point copies frames to an analyzer. It does not assign VLANs, and captured frames are not an authorization result. A DHCP lease timer controls how long an address is held. A short lease does not identify a camera, and DHCP does not choose the VLAN after profiling. The VLAN has to be selected before or as the session is authorized. Exam caveat: the profile has to be accurate. If the camera is still unknown, the authorization rule never matches and the device stays on the default result. Operational check: in the ISE log for that camera, confirm the profile and the authorization rule that returns the camera VLAN, and confirm a laptop on the same WLAN does not receive it.