
Several engineers share one local admin account on a Catalyst 9800, and the security team wants a separate accounting record for each engineer's management login. Which change provides that?
Select an answer to reveal the explanation.
Short Explanation
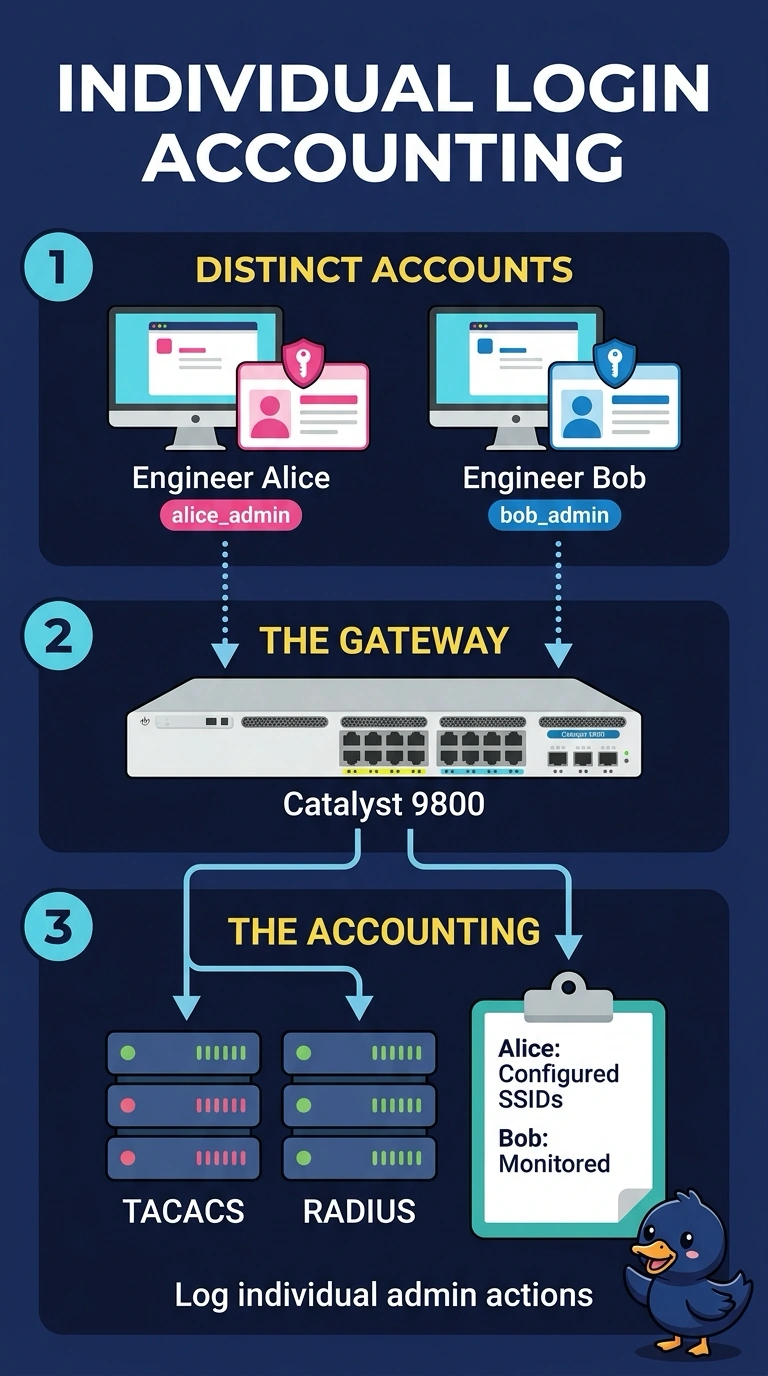
A shared local password is one signature for the whole crew. You want each engineer to sign in as themselves, and TACACS or RADIUS is what writes that signature down. A guest passphrase is not a management login.
Full Explanation
Management authentication is separate from client WLAN authentication. Pointing administrator logins at TACACS or RADIUS, with a distinct account per engineer, gives the security team a per-person accounting record of who configured the controller and when. The shared local admin account cannot do that, because every session looks like the same user. A guest passphrase admits visitors to a WLAN. It does not authenticate SSH or the controller GUI, and it does not write a management accounting record for an engineer. An RF profile sets radio parameters for a group of access points. It is not an account, and a channel change is not a login record. Monitor mode changes what one access point does over the air. It does not replace the controller's admin login, and engineers would still need a management session to configure anything. Exam caveat: keep a local break-glass account for the day the AAA server is down, and do not use the same policy you wrote for wireless clients as if it were automatically the admin method. Operational check: log in as one engineer, confirm the AAA accounting log shows that username, and confirm a second engineer shows up as a different record.