
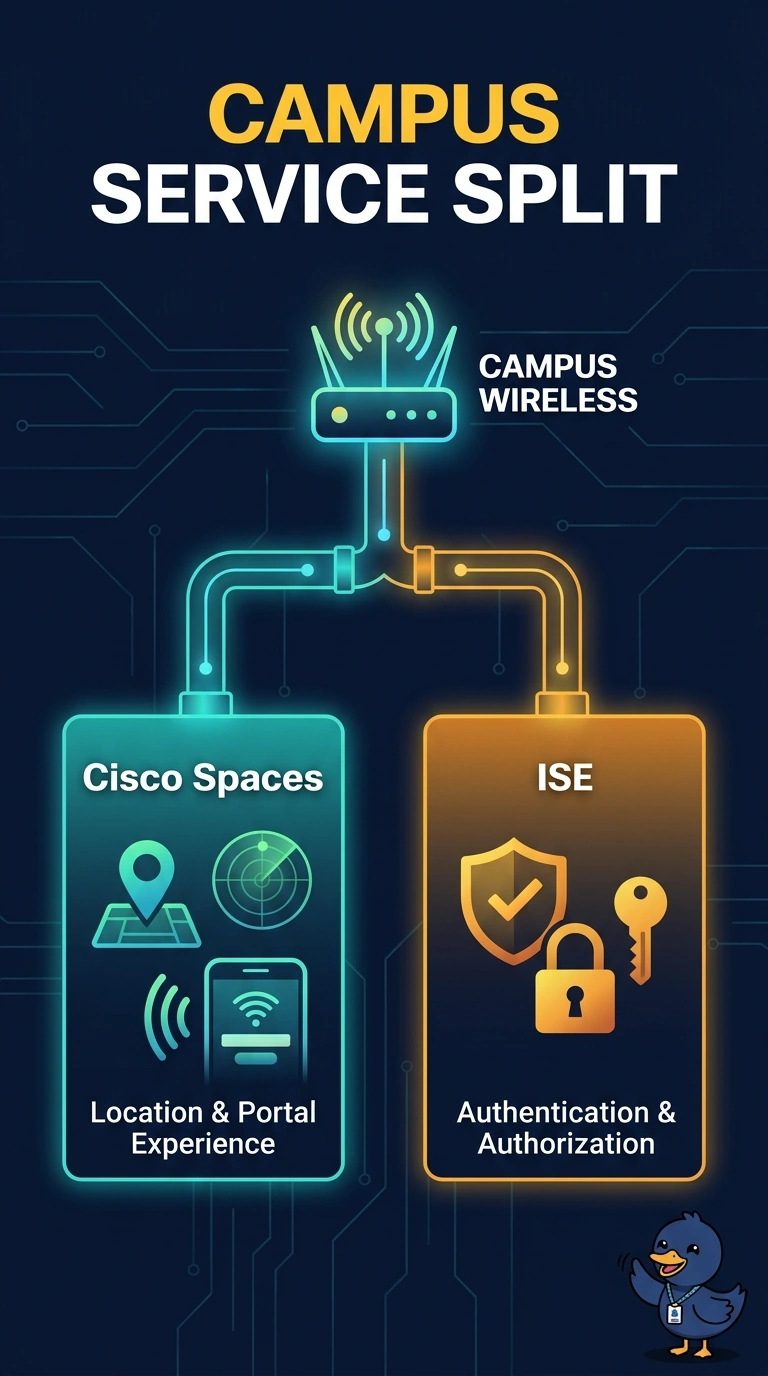
A SaaS campus wants location analytics and a captive-portal experience from Cisco Spaces, while authentication and authorization decisions stay on ISE. Which split matches those products?
Select an answer to reveal the explanation.
Short Explanation
Spaces watches where people are and can host the portal they click through. ISE is the policy desk that decides who gets on. You do not ask the location product to mint 802.1X certificates or to plan channels.
Full Explanation
Cisco Spaces provides location analytics and engagement tools, including captive-portal experiences. ISE is the policy server that authenticates and authorizes network access. The split the campus described, Spaces for location and the portal, ISE for authentication and authorization, matches what those products are for. Spaces is not the certificate authority for 802.1X, and ISE does not select antennas. Swapping them assigns each product a job it does not do. Spaces is not the RF group leader. RRM leadership is a wireless-controller function, and ISE is not a DHCP server for every VLAN. Using ISE as DHCP would abandon both the policy role and the actual DHCP design. Access-point image predownload is a controller maintenance action, and channel planning belongs to the RF design and RRM, not to ISE. Spaces does not replace the controller upgrade path. Exam caveat: a portal on Spaces still needs the wireless and policy path to redirect or land the client, and ISE remains the authorization point if the design says access decisions stay there. A portal page alone is not the authorization rule. Operational check: confirm a test client hits the Spaces portal and that the ISE live log, not Spaces, shows the accept or deny for that session.