
Clients authenticate while the primary RADIUS server is up. When it is down, they fail. The secondary server is reachable, and its shared secret does not match the controller. What is wrong?
Select an answer to reveal the explanation.
Short Explanation
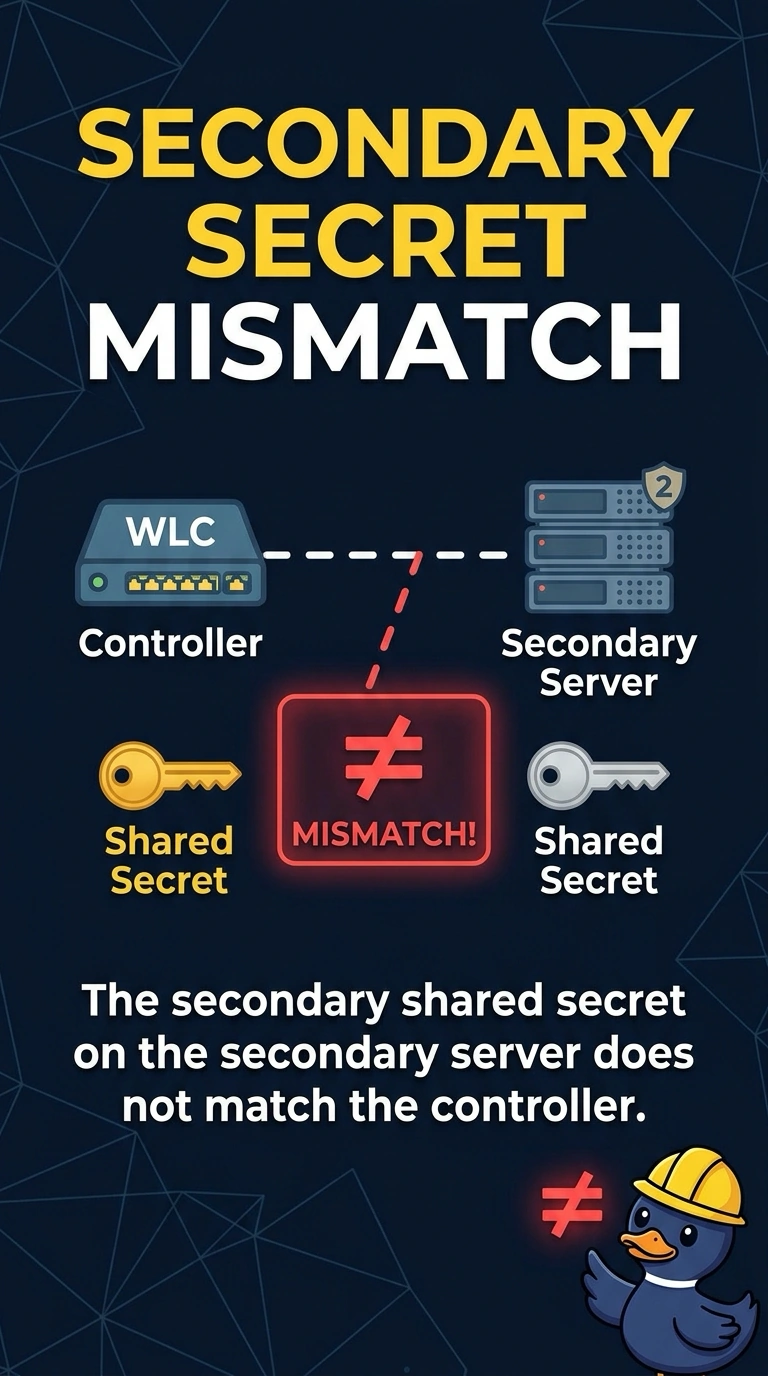
The primary agrees with the controller, and the secondary does not. When your primary goes away, the secret that does not match is the one that fails the clients. Fix the secondary secret.
Full Explanation
A shared secret is checked per server. Clients succeed against the primary and fail when they are sent to a secondary whose secret does not match the controller, even though that server is reachable. The primary secret is not the failure. Clients work while the primary is up. The beacon does not carry a RADIUS secret. The country code does not select one. The primary RADIUS server works. The secondary has a mismatched shared secret, so failover fails when the primary is down. Check one live client after the change and leave the rest of the floor alone until that client matches the result you expected. Confirm the symptom on the next attempt before changing anything else. Confirm the symptom on the next attempt before changing anything else. Confirm the symptom on the next attempt before changing anything else. Exam caveat: the secret has to match on both sides. Changing it only on the controller, or only on the server, leaves the same mismatch. Operational check: shut the primary in a test, confirm a client succeeds against the secondary, and then restore the primary.