
Hotel guests get an address on the guest WLAN and never see the ISE portal. DHCP works. The WLAN is meant to use central web authentication, and the session is not being redirected. What is missing?
Select an answer to reveal the explanation.
Short Explanation
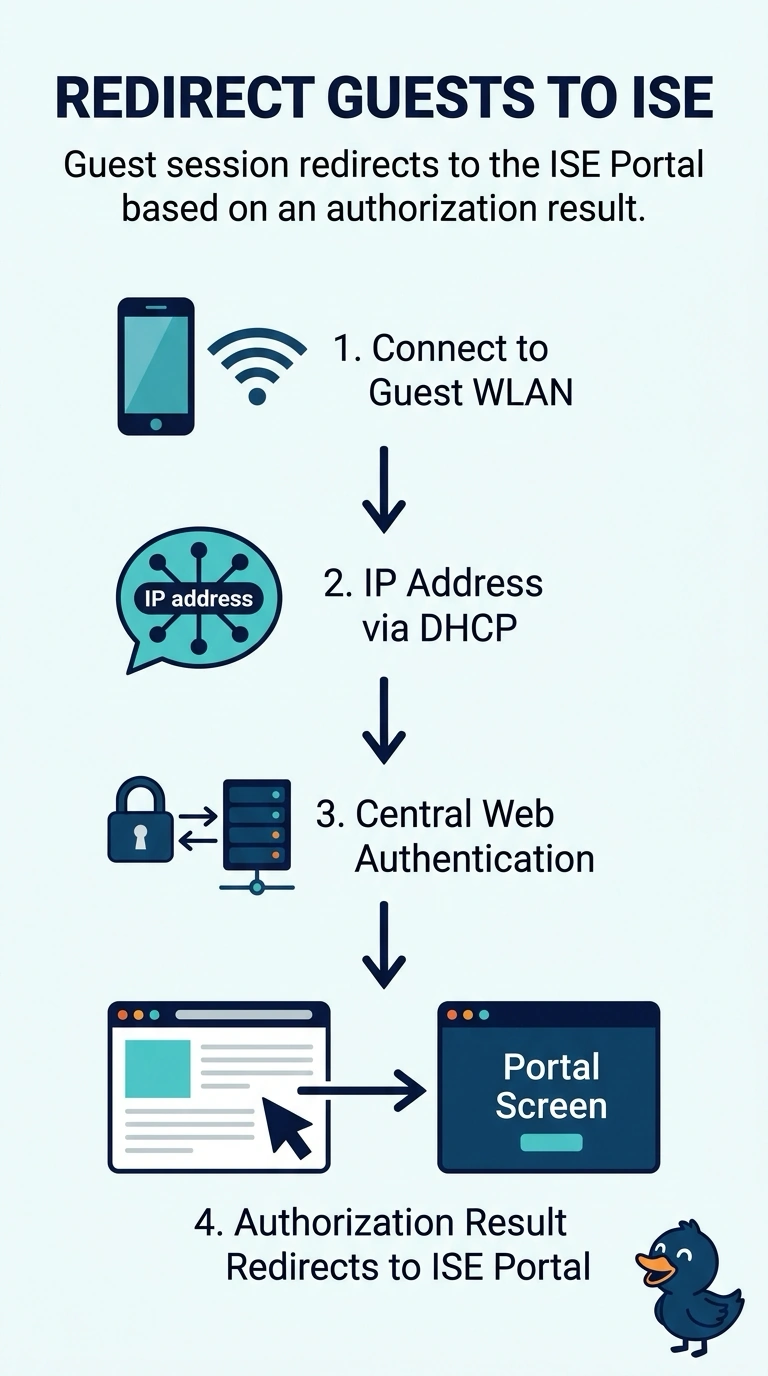
Your guest already has an address, so this is not a lease problem. Central web auth still has to tell the controller to redirect that session to the ISE portal. A wider channel will not invent the redirect.
Full Explanation
Central web authentication depends on an authorization result, usually from ISE, that tells the controller to redirect the unauthenticated guest to the portal. DHCP has already worked, and the session is not being redirected, so the missing piece is that redirect result. A pre-shared key would authenticate the guest at association and would not create an ISE redirect. The hotel would no longer be doing central web auth. Monitor mode does not serve clients and does not host the ISE portal. The portal is on ISE, and the access points have to stay in a serving mode for the guest WLAN to exist. Channel width has nothing to do with HTTP redirect. A 160 MHz channel does not trigger a portal, and guests who already have addresses do not need a wider channel to be redirected. Exam caveat: the redirect ACL has to permit the portal and DNS and deny, or redirect, the rest. A result that names a redirect the ACL then blocks still shows a blank browser. Operational check: in the ISE log, confirm the guest hits a rule that returns the redirect, and confirm the controller session shows the redirect ACL.