
A logistics firm's posture policy must check Windows 11 laptops and macOS laptops for disk encryption and current antivirus. No device has a client yet, checks must run again after every reboot when the device reconnects, and IT allows installs only from the ISE server itself. Which client provisioning design meets these needs?
Select an answer to reveal the explanation.
Short Explanation
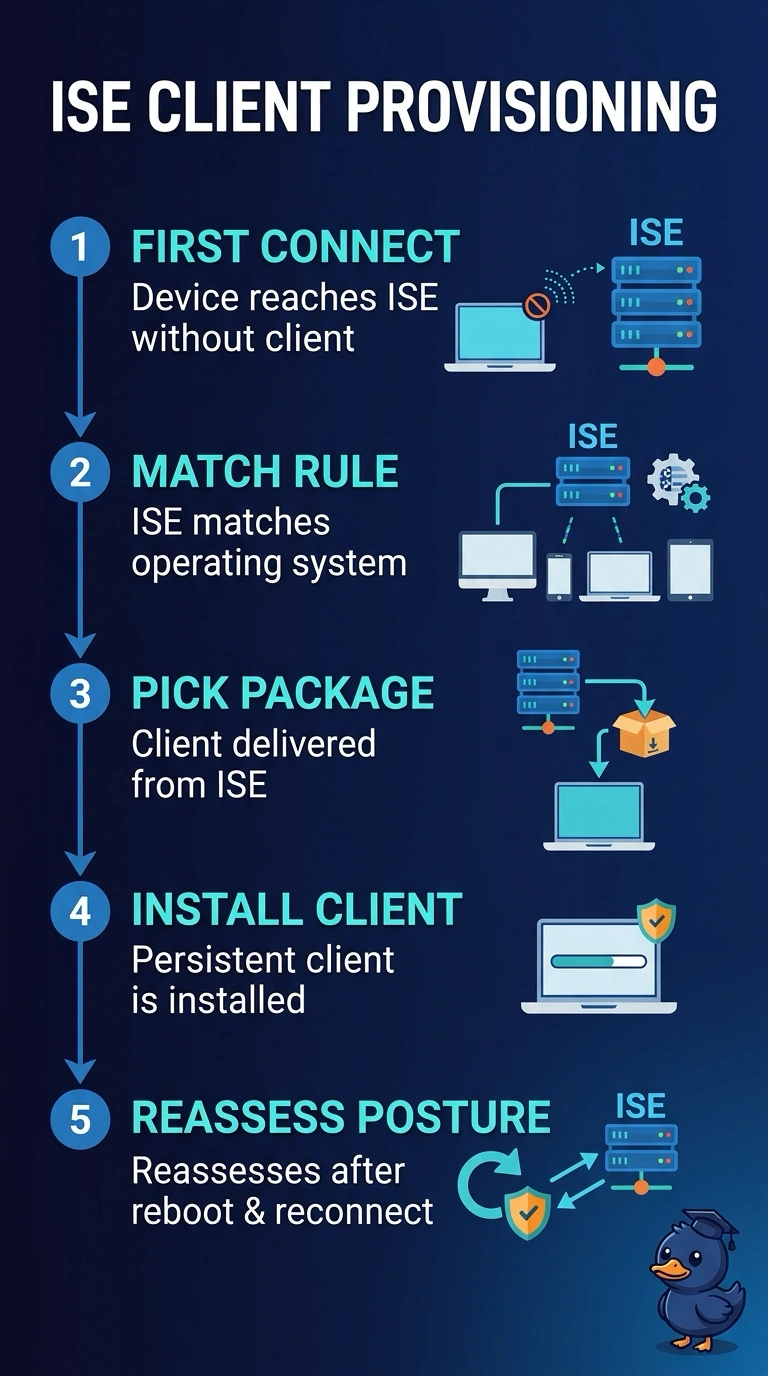
Your client provisioning policy can match each Windows 11 or macOS laptop to the right persistent client and deliver it directly from ISE. Since neither laptop has a client yet, this gets you started, and the client can rerun the disk-encryption and current-antivirus checks when your devices reconnect after a reboot.
Full Explanation
The design uses ISE client provisioning rules keyed to operating system, so each Windows 11 or macOS laptop receives the appropriate persistent client directly from the ISE server. Because the client remains installed, it can perform posture checks again when a device reconnects after reboot; the posture policy can assess disk encryption and whether antivirus protection is current. Deploying platform-matched agents through an external software-management service could meet the platform, assessment, and repeat-check needs, but it violates the requirement that installations come only from ISE. A persistent client that checks whether antivirus is installed can provide durable, cross-platform posture assessment, yet installation status does not establish that definitions or protection are up to date; the policy must evaluate currency. Provisioning only a Windows client from ISE meets the source, persistence, and assessment requirements for Windows, but leaves macOS laptops without the required client and posture coverage. Exam caveat: distinguish antivirus presence from current protection, and a persistent agent from a one-time or agentless assessment; these terms are not interchangeable. Practical check: test a freshly provisioned device from each operating system, verify the client source in ISE, confirm encryption and antivirus-freshness results, then reboot and reconnect to confirm posture is evaluated again.