
A retailer runs one appliance in the data center for centralized policy, monitoring and directory integration, and places a smaller server in each store behind a wireless controller that must authorize shoppers and push re-authorizations on the fly. Store logins must be answered locally without proxying AAA traffic, while logs still roll up to the central collector. Which persona role should run on each store server?
Select an answer to reveal the explanation.
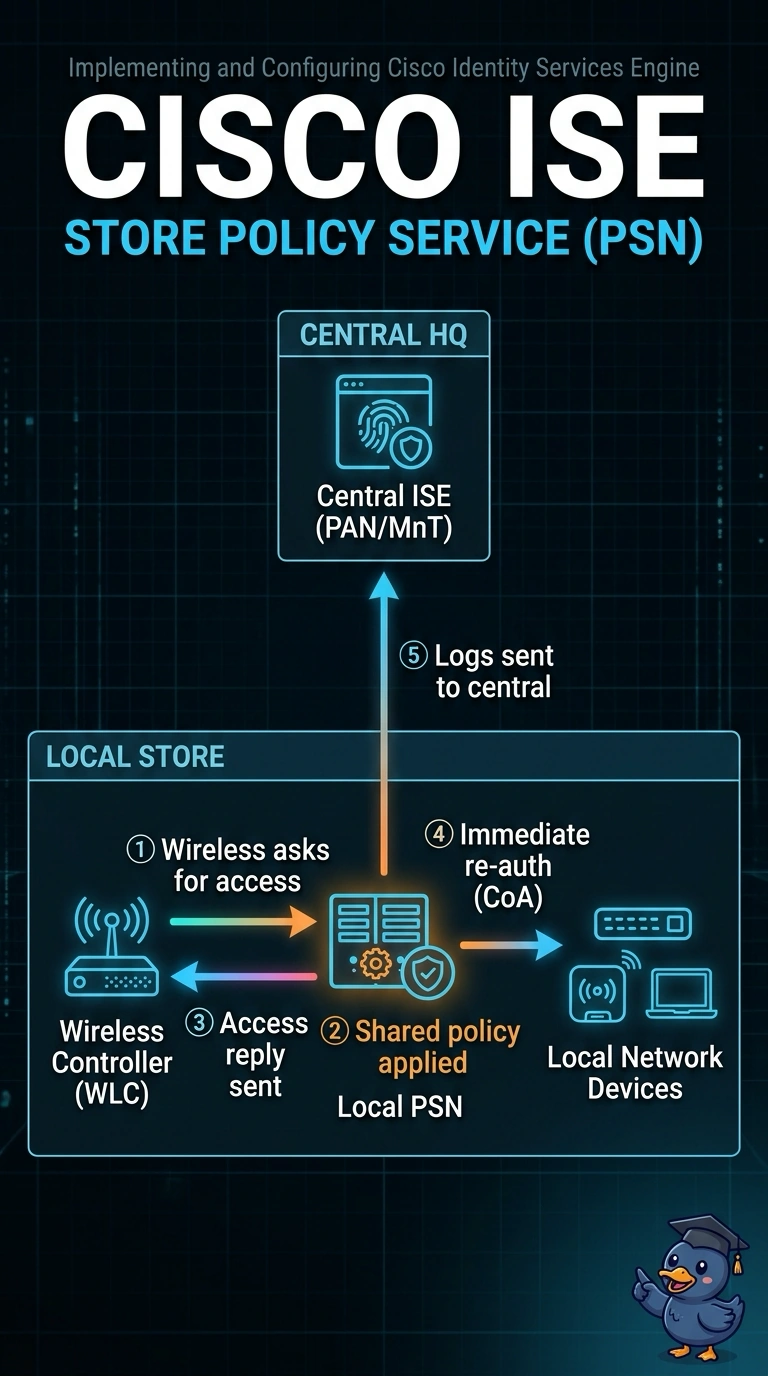
Short Explanation
You want each login decided where the traffic lands, and terminating AAA requests plus pushing a change of authorization is exactly what the Policy Service persona does. It's like a store clerk checking the head office rulebook at the counter: the rules stay central, but the decision happens locally.
Full Explanation
The Policy Service persona is the correct choice because it processes AAA requests and can send re-authorizations to network devices. Placing it at each store lets the wireless controller get authentication decisions locally, without proxying AAA traffic to the data center; logs can still be forwarded to the central collector. The Monitoring and Troubleshooting persona is useful for collecting and reviewing authentication records, but it is not the service that answers AAA requests. In that proposed design, proxying AAA to the central Policy Service defeats the requirement for local AAA responses. The Policy Administration persona supports centralized configuration and policy management; distributing rules from it does not make it an AAA decision point, so the central Policy Service would still have to answer requests. The pxGrid persona shares session and context information with subscribed systems, but that information exchange is not a substitute for AAA processing. Having the controller handle authentication locally would also leave the store server’s required AAA role unfulfilled. Exam caveat: distinguish the Policy Service persona, which makes runtime access decisions, from administration and monitoring functions, even when those functions are deployed alongside policy services. Practical check: verify that each store’s controller targets its local Policy Service for AAA and that a test re-authorization reaches the local network device, while logs appear at the central collector.