
A distributed ISE design must keep every site's policy sets under one administrative point, while each site keeps authenticating even when the central node fails or the wide area link drops. Assuming each site's identity source remains reachable locally, which node layout satisfies both requirements?
Select an answer to reveal the explanation.
Short Explanation
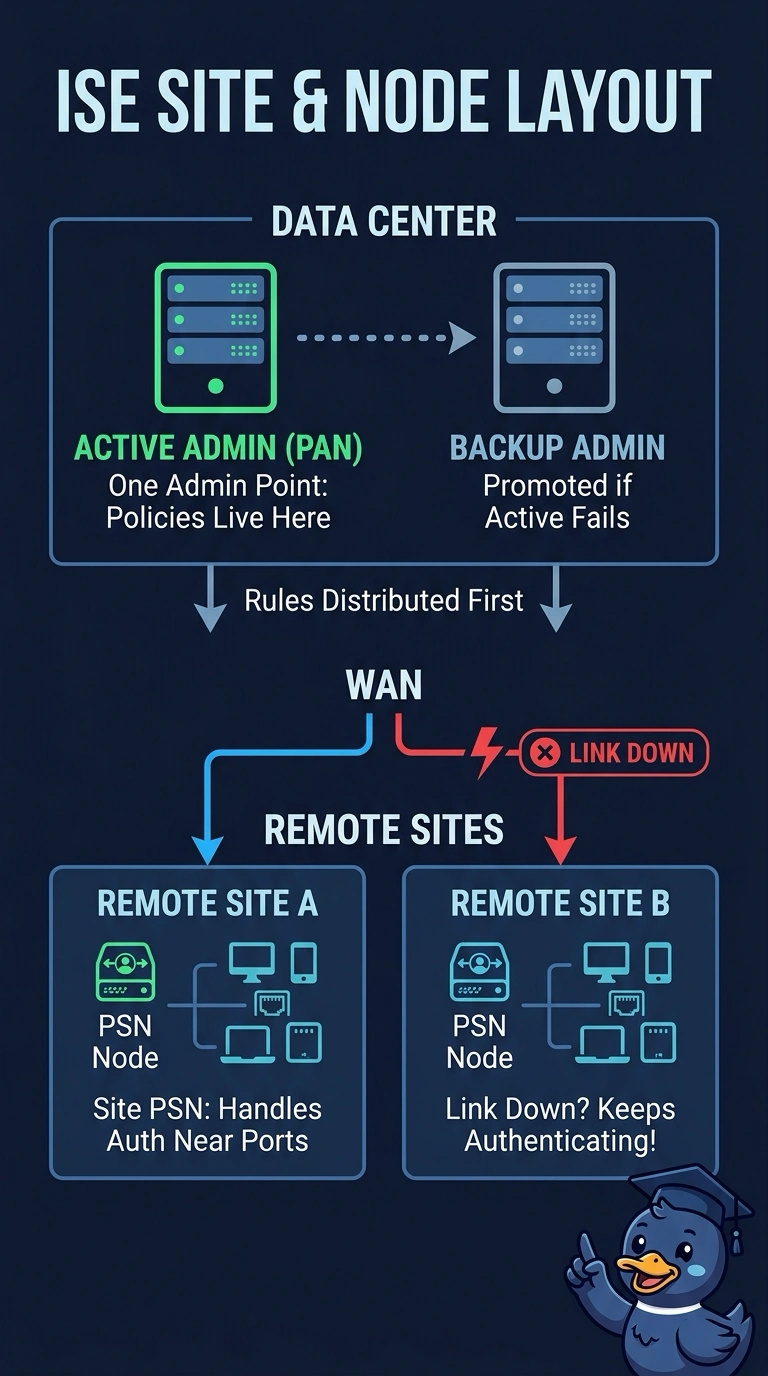
Your design works like a central recipe book with local kitchens: redundant administration and monitoring nodes in the data center keep policy sets under one administrative point, while a policy service node at each site handles authentication locally. If the central node or WAN link goes down, your sites can keep authenticating as long as their local identity source and other required services remain available.
Full Explanation
The correct design separates policy administration from authentication processing: the redundant administration and monitoring deployment provides one administrative point for policy sets, while a policy service node (PSN) at each site can authenticate users locally. With the site's identity source reachable locally, authentication need not depend on the data-center node or WAN connection. A redundant deployment at each site would support authentication during outages, but local policy administration would leave policy sets managed separately rather than under one administrative point. Central administration with a PSN at each site would keep policy centralized, but using the data-center identity source makes authentication depend on that source and its network path; local identity sources would not help if they are not used. Central administration with PSNs in the data center and dual WAN links would centralize policy and provide resilient connectivity, but sites would still lack local authentication if WAN connectivity were lost or the central service were unavailable. Exam caveat: a PSN at a site does not by itself guarantee continued authentication; the required identity source and any other dependencies must also be reachable through the surviving local path. Practical check: test authentication at each site with the WAN disconnected and the central node unavailable, and verify that policy remains centrally managed.