
A logistics company runs MAB for handheld barcode scanners. When profiling finishes, ISE learns a scanner's true vendor and must push the corrected authorization to the live session right away, but the handheld must stay connected, keep its DHCP lease, and see no interruption on the port. Which CoA message should ISE send to the switch?
Select an answer to reveal the explanation.
Short Explanation
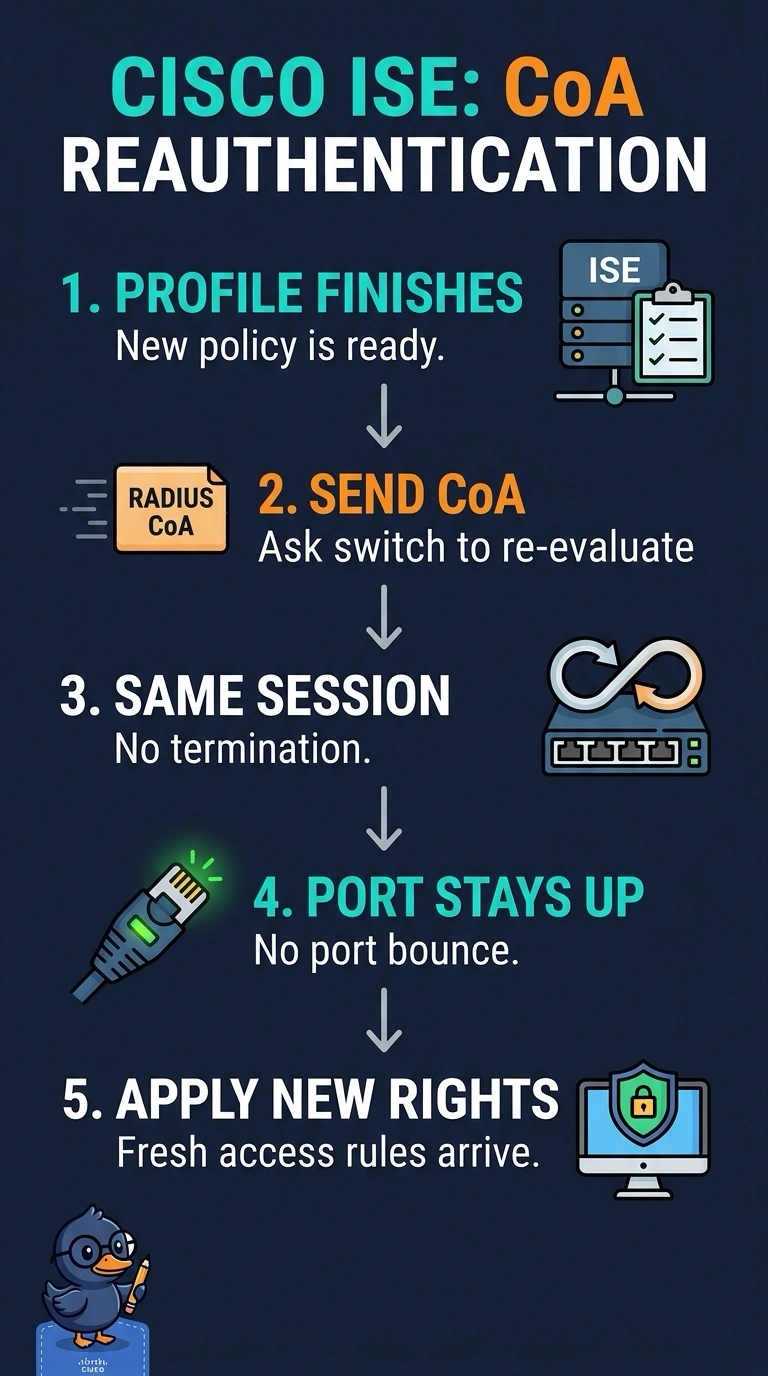
Send a reauthentication CoA so the switch rechecks your scanner’s live session and applies its updated authorization. It’s like refreshing the session’s permissions without unplugging the port, so your scanner stays connected and keeps its DHCP lease.
Full Explanation
A RADIUS reauthentication CoA is the appropriate choice because it asks the switch to authenticate the existing MAB session again, allowing ISE to evaluate the newly learned vendor information and return the corrected authorization profile. In the stated scenario, this updates authorization on the live session while preserving the port connection and DHCP lease. Replacing only the downloadable ACL is a valid way to change a session’s ACL without disconnecting it, but it does not cause ISE to rerun authorization and select the corrected profile; the session could therefore retain the wrong authorization result. A Disconnect CoA followed by MAB can obtain the corrected result promptly, and the existing DHCP lease may remain valid, but terminating access creates an interruption, contrary to the requirement. Waiting for periodic MAB reauthentication avoids a deliberate interruption and can eventually apply the corrected result, but it does not meet the requirement to update the live session right away. Exam caveat: CoA behavior and supported attributes can vary by switch platform and software release, so do not assume every authorization change is applied identically. Practical check: verify the switch’s session details and ISE live logs show the corrected profile on the same session, then confirm the port stayed up and the scanner retained its DHCP lease.