
A manufacturing firm runs one wired policy set covering every plant-floor switch. The team added a rule for contractor groups that should land on a restricted VLAN, but contractors still get the general Engineering department result because that broader rule sits above it. Everyone authenticates to the same directory, and the team wants to keep a single policy set. Which authorization policy change makes the contractor rule match first?
Select an answer to reveal the explanation.
Short Explanation
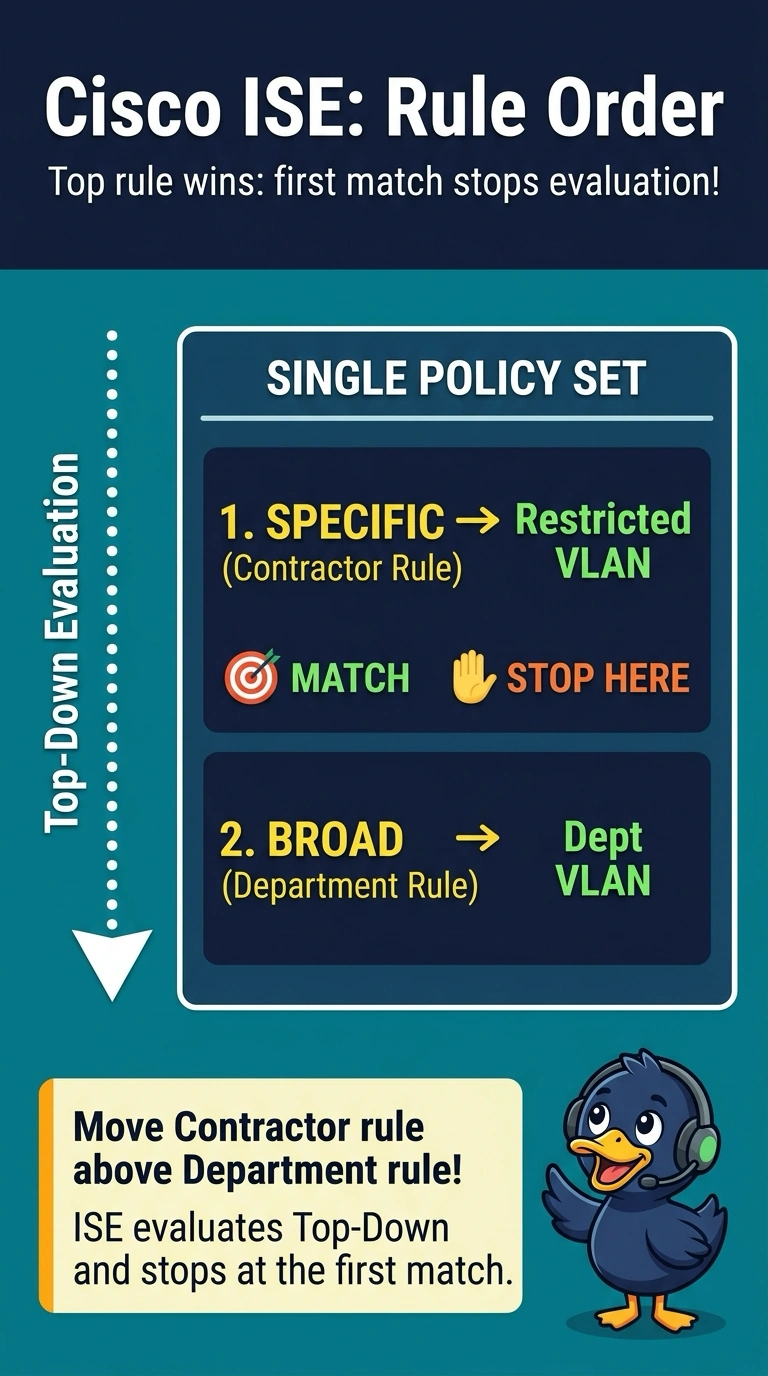
ISE races through authorization rules from the top down and stops at the first one that fits, so placement decides the outcome. Stacking the narrower rule on top of the general pile is how detail wins, and it's what you are changing here. Reordering the authorization rules is the whole fix.
Full Explanation
ISE walks the authorization rules from top to bottom and stops at the first rule whose conditions match the session, so a broad department rule sitting above a narrow contractor rule will win for contractors every time. Moving the specific rule higher is the standard way to layer detail over a general policy: the single policy set stays intact, and only the contractor groups receive the restricted VLAN result. Reordering identity sources in the authentication policy cannot change the outcome, because that policy decides how a username is resolved before authorization ever runs, not which authorization result gets applied. Adding the contractor groups to the department rule merges two populations into a single result, so department staff would also land on the restricted VLAN, which contradicts the need for separate access. Creating a second policy set does technically work, since policy sets are matched in order too, but the team asked to keep one policy set for the wired policy and it splits rules that belong together. Exam caveat: the Hits column beside each rule counts how often its conditions matched, and RADIUS Live Logs name the rule that actually fired. Practical check: send one test authentication from a contractor workstation and read the returned VLAN in RADIUS Live Logs before and after moving the rule.