
A logistics company runs one ISE node holding both the administration and monitoring personas, and adds a second server in the datacenter to absorb 802.1X load for 5,000 handheld scanners. Policy edits must stay on the existing node while the new server answers endpoint requests with the same rules. Which persona assignment and registration step will integrate it correctly?
Select an answer to reveal the explanation.
Short Explanation
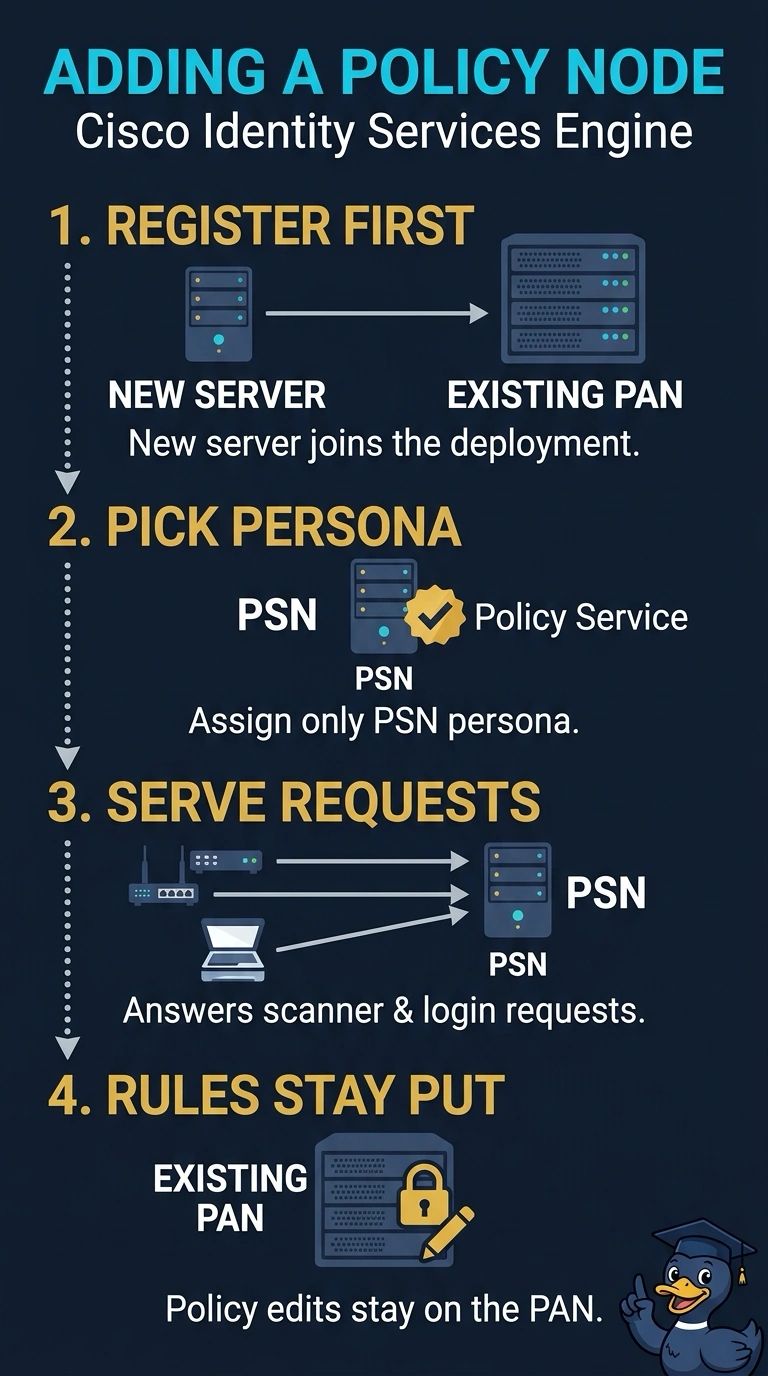
Register the new server with your existing PAN, then assign it only the Policy Service persona so it can handle scanner logins using the deployment’s policies. It’s like adding another checkout lane: your original node still manages policy edits, while the new one helps serve the scanners.
Full Explanation
Registering a node places it inside the existing deployment: the PAN records it as a member, and the node receives its configuration and policies from that PAN. The Policy Service persona handles RADIUS and web requests from endpoints, so a scanner-heavy datacenter node needs that persona to absorb 802.1X load while administration stays on the original server. Copying policy manually fails because a node outside the deployment is not synchronized, so later rule changes can leave the copy out of date. Assigning the Monitoring persona does not address the authentication load; that persona collects logs and supports reporting. Adding the Policy Administration persona is unnecessary for this task: ISE supports a primary and a secondary PAN, but the question requires policy edits to stay on the existing node. A node may hold multiple personas, so the choice is about which work it performs, not how many roles it may carry. Practical check: open Deployment on the PAN and confirm the new server is registered with the Policy Service persona enabled, then verify that a scanner login appears in its live log.