
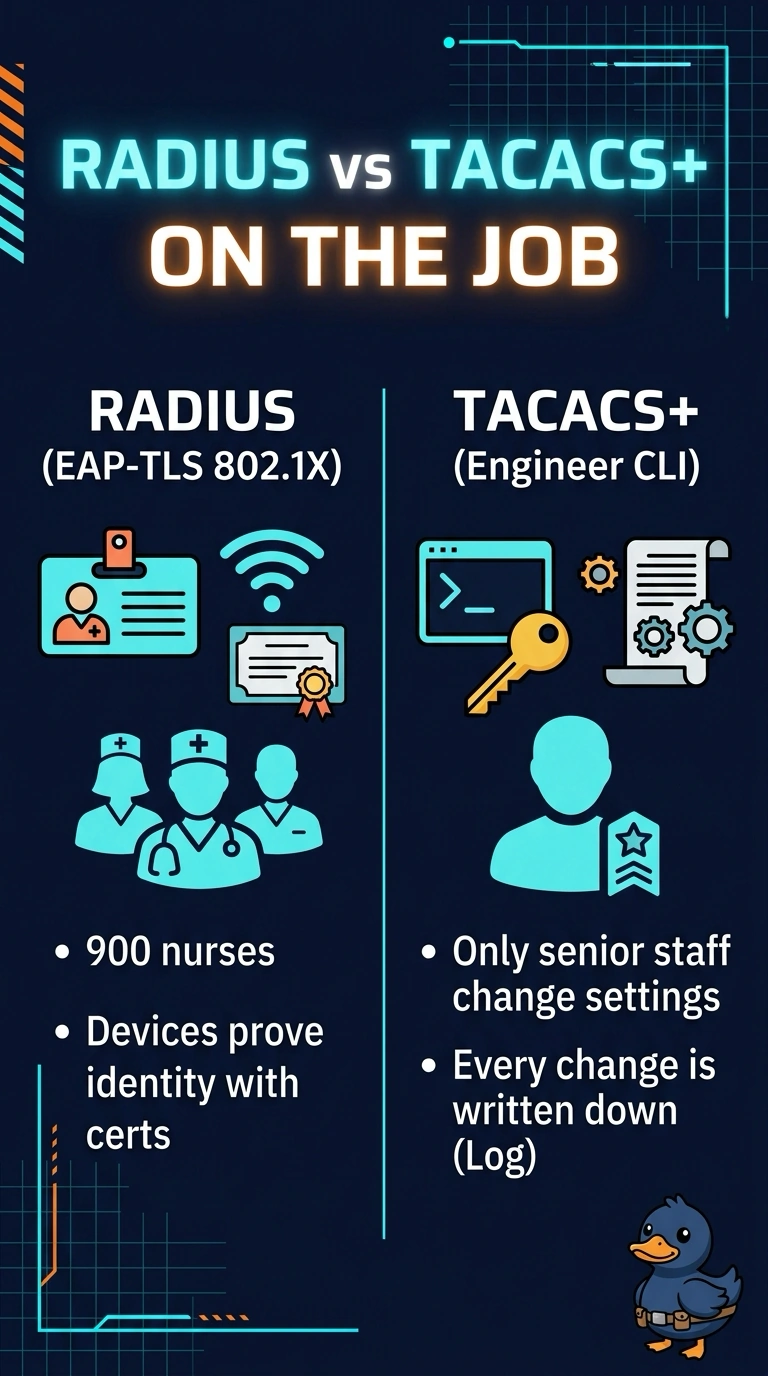
A hospital must place 900 nurses' devices on EAP-TLS 802.1X through ISE while only senior engineers change switch configurations. Every configuration command has to reach the audit log, and administrative traffic must be encrypted beyond the password. Which AAA protocol assignment should the team configure?
Select an answer to reveal the explanation.
Short Explanation
You use RADIUS for the nurses’ EAP-TLS 802.1X sessions and TACACS+ for engineers’ CLI access, with command accounting enabled. That gives you the right fit for both services and a record of each configuration command. You can think of it as choosing the right tool for each job.
Full Explanation
RADIUS is appropriate for the nurses’ EAP-TLS 802.1X sessions, while TACACS+ suits engineer CLI administration because it encrypts the full TACACS+ packet and supports command-level accounting. Enabling command accounting is essential: the audit requirement covers every configuration command, not just the start and end of an administrator’s session. Using TACACS+ for both services provides a strong choice for CLI access and command accounting, but TACACS+ is not the standard protocol for carrying EAP-TLS authentication for 802.1X; that role belongs to RADIUS. Using RADIUS for both services may provide per-command accounting, but its shared secret does not encrypt the entire packet; it protects the password field, so it does not meet the requirement to encrypt administrative traffic beyond the password. Using RADIUS for 802.1X and TACACS+ for CLI access with session accounting but without command accounting can record administrator session events, but not each command, leaving the central audit requirement unmet. Exam caveat: distinguish authentication and session records from command authorization and command accounting; a shared secret does not mean the whole AAA exchange is encrypted. Practical check: test a configuration change on a representative switch, verify that the audit system records the engineer, command, device, and timestamp, and use packet inspection to confirm administrative AAA traffic is protected.