
A branch's Threat Defense appliance shows a stale status in the Management Center after an overnight circuit change, while traffic through its data interfaces flows normally. Its Management Center connection is configured to use the management interface. The engineer needs recorded proof that the appliance's management traffic is still reaching the Management Center, with a filter so only that exchange appears. Which troubleshooting method provides that filtered proof of management connectivity?
Select an answer to reveal the explanation.
Short Explanation
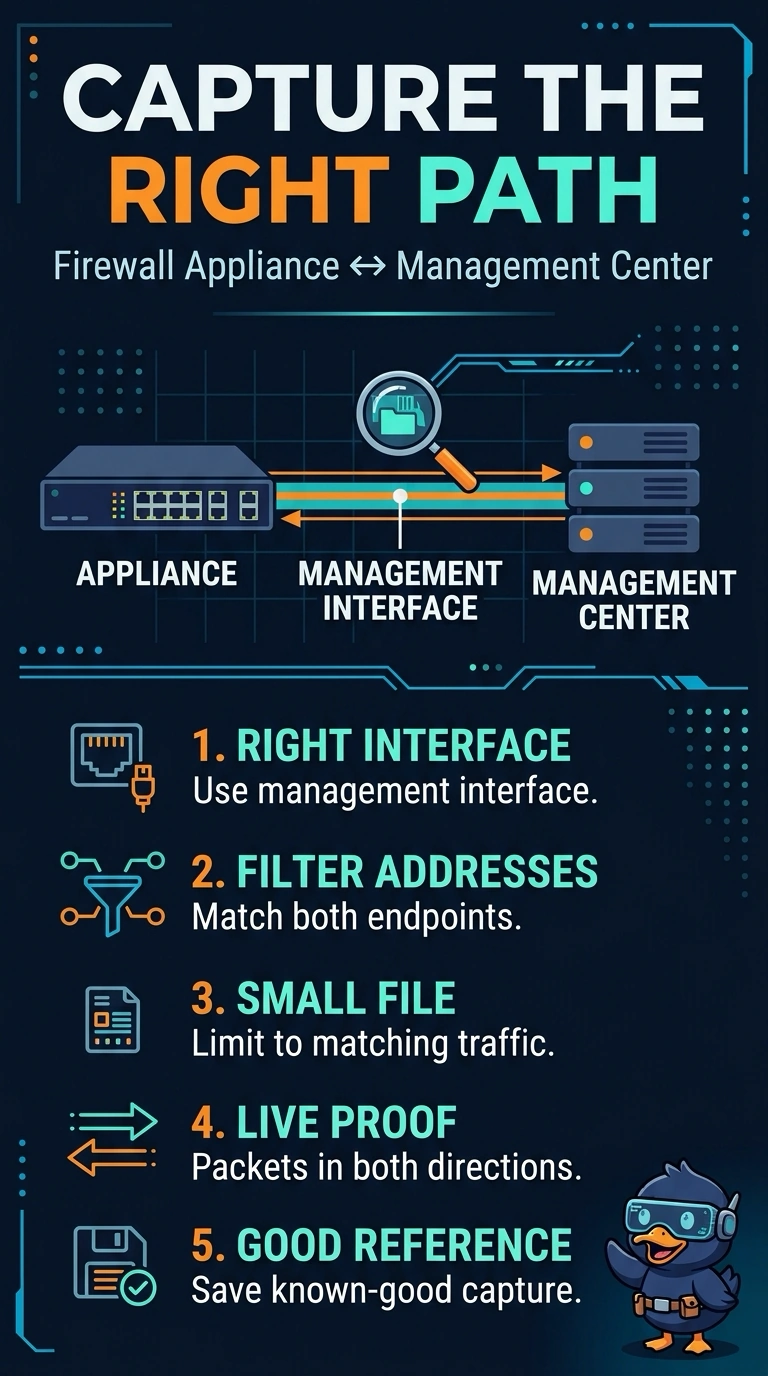
Since your appliance uses the management interface to reach the Management Center, capture there to check that connection. Filter the management interface capture to the appliance and Management Center addresses so you see only their exchange. It’s like aiming a doorbell camera at one doorway instead of recording the whole street.
Full Explanation
The Management Center connection is configured to use the management interface, so a packet capture on that interface is the direct way to establish whether management traffic is reaching the center. Filtering on both the appliance and Management Center addresses narrows the capture to their exchange and gives recorded packet-level evidence, rather than relying on the stale status display. Capturing on an outside data interface is a valid troubleshooting technique when traffic is expected to traverse that interface, but it fails here because the configured Management Center path uses the management interface; packets on the data interface cannot prove that this management connection is working. A management-interface capture filtered only by the Management Center address is also a reasonable diagnostic, but it can include other devices’ traffic to that destination, so it does not isolate only this appliance’s exchange. Connection event logging can provide useful evidence of recorded check-in activity and can be filtered by address, but it is event data rather than a packet capture of the management-interface exchange, so it does not meet the requested proof method. Exam caveat: a capture filter and a display filter may be applied at different stages; confirm which kind the appliance’s capture tool uses, since a capture filter can exclude packets before they are saved. Practical check: verify the appliance and Management Center IP addresses, start the filtered capture on the management interface, and confirm that packets in both directions appear during a check-in attempt.