
A retailer runs four virtual Secure Firewall Threat Defense appliances on its on-premises ESXi cluster and three FTD instances launched from the AWS marketplace. Compliance requires the management console itself to run on premises inside the corporate network, and the team wants one console with shared objects. Which management deployment satisfies both requirements?
Select an answer to reveal the explanation.
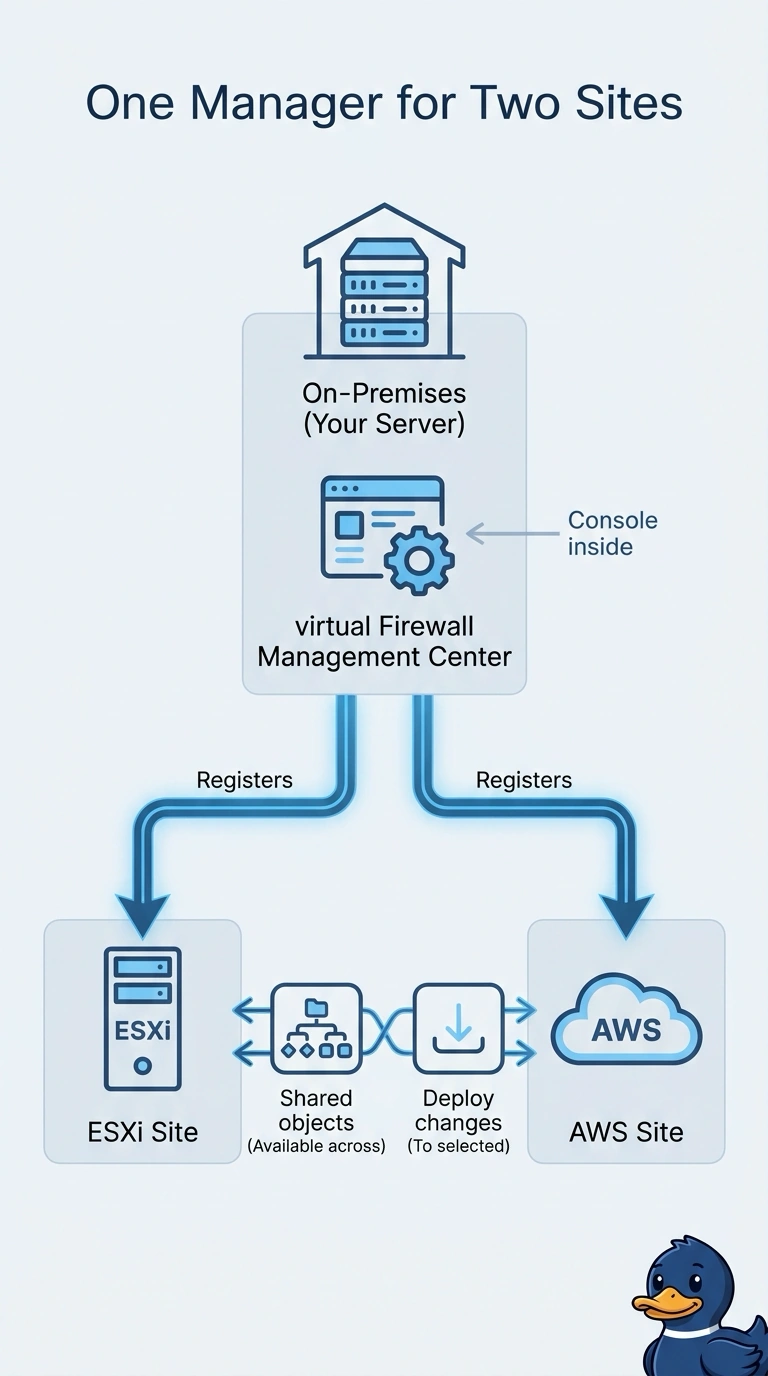
Short Explanation
Run a virtual Firewall Management Center on premises to manage both your ESXi and AWS appliances from one console with shared objects. It’s like a single control desk for both locations, while a hosted console or separate local managers wouldn’t meet your requirements.
Full Explanation
A virtual Management Center hosted on the retailer’s on-premises hypervisor can manage the ESXi and AWS instances, provided the required network connectivity is configured. It provides centralized management and supports shared objects; policies can still be assigned and deployed to the appropriate devices. Managing each instance with its local device manager does not provide a shared central console. Security Cloud Control is hosted by Cisco, and a Management Center running in AWS is not on premises, so neither meets the stated compliance requirement. When moving a device from another manager, plan the transition and verify the effects on its configuration before registering it with the new manager.