
The security team wants access control rules in Secure Firewall Management Center to match on live Cisco ISE session context — the authenticated user, the device type, and the Security Group Tag — instead of static address objects. ISE 3.x is already in production. Which pxGrid publisher/subscriber design lets FMC consume that context as ISE publishes it?
Select an answer to reveal the explanation.
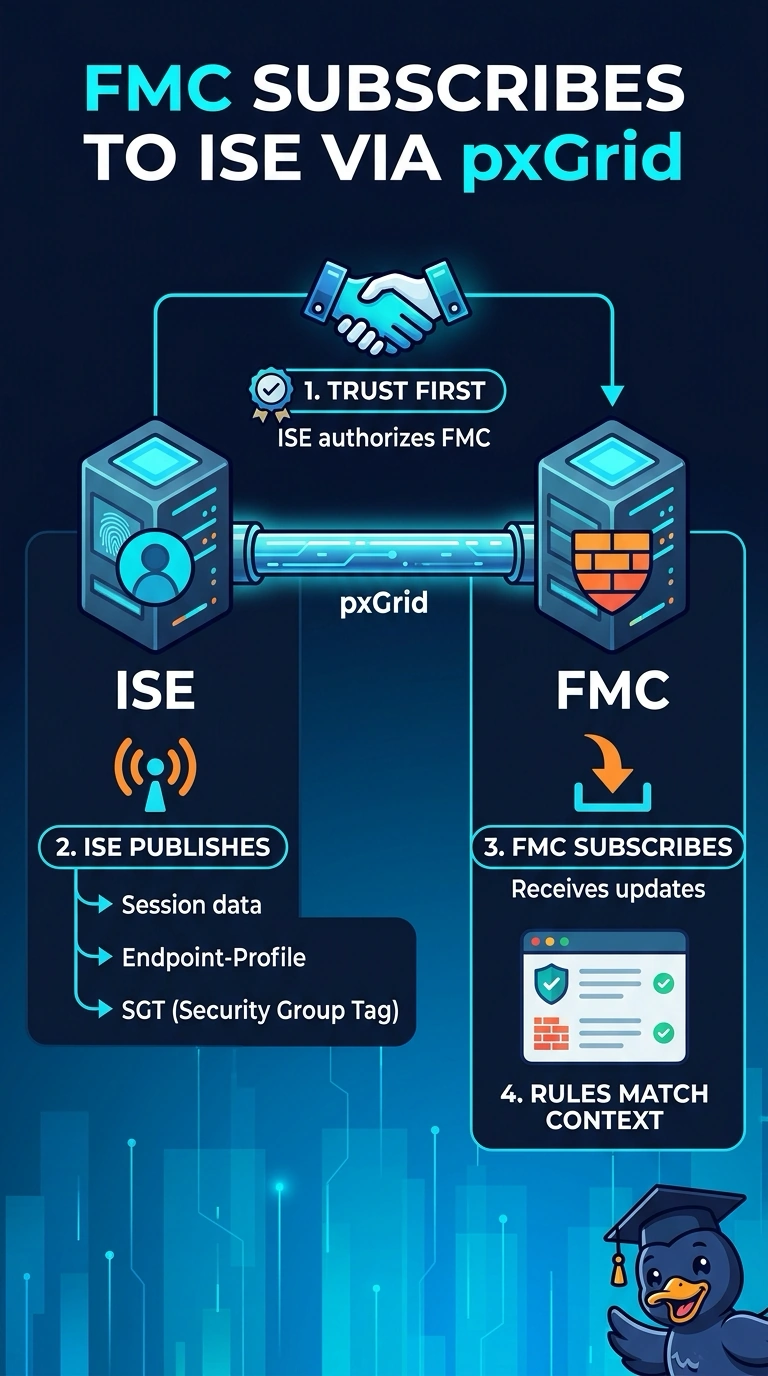
Short Explanation
With pxGrid, you have FMC subscribe to ISE’s published session, endpoint-profile, and Security Group Tag data, so your rules can use the authenticated user, device type, and tag as updates arrive. It’s a live feed, not a periodic snapshot.
Full Explanation
pxGrid is a publish-and-subscribe fabric with a controller at its centre. ISE holds the session records and publishes relevant session, endpoint-profile and Security Group Tag data; FMC registers as a pxGrid client and subscribes to the data it needs. FMC can then use the available identity context in access control rules. Security Exchange Protocol distributes Security Group Tag-to-address mappings, but those mappings alone do not provide the full user and device-type context in the question. An Active Directory realm provides directory user and group information, not the ISE session and tag context requested. A scripted API poll provides updates on its schedule rather than as ISE publishes them. Screen names and pxGrid versions can vary between releases; verify the configured identity source and subscription status in the deployed version.