
A university security team must refresh the vulnerability data behind the intrusion policies on three Threat Defense devices. Every change has to flow through the Management Center, nobody may touch the appliances during the change window, and the fresh data must be live on all three by the end of it. Which update sequence delivers the new vulnerability data to the devices?
Select an answer to reveal the explanation.
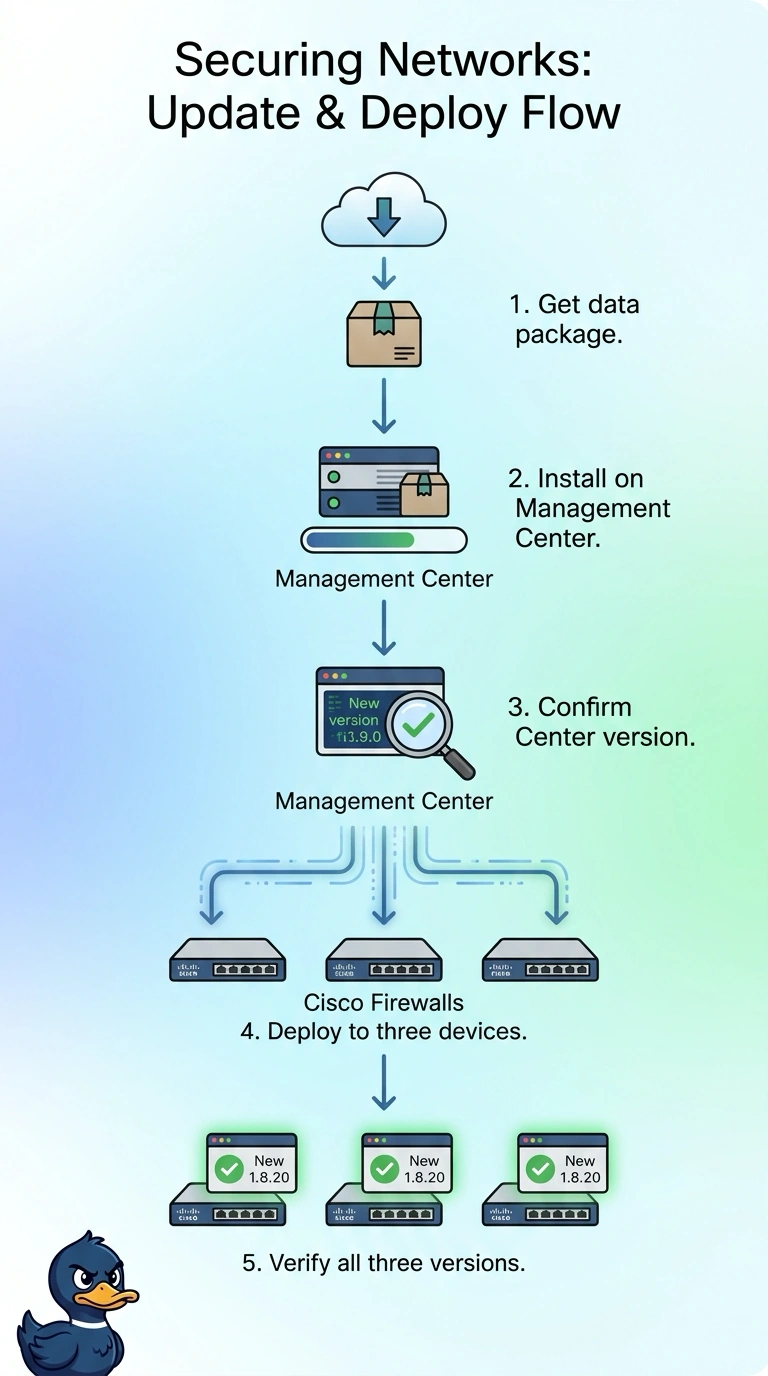
Short Explanation
You can keep the change centralized: install the vulnerability data on the Management Center, then deploy the updated configuration to all three devices within the change window. That sequence makes the fresh data live on each device without anyone touching the appliances.
Full Explanation
Install the vulnerability data on the Management Center first, then deploy the updated configuration to all three Threat Defense devices. The Management Center is the required source of the update, and deployment delivers the resulting configuration to managed devices; completing both steps within the change window makes the fresh data live on every device without anyone working on the appliances directly. Installing the data centrally but waiting for the next scheduled deployment window follows the right workflow, yet misses the deadline, so the data will not be live on all devices by the end of the change window. Deploying existing policies before installing the new data reverses the dependency: that deployment cannot deliver data the Management Center does not yet have, and installing the data afterward does not make the earlier deployment current. Installing the data centrally but deploying only to devices assigned the affected intrusion policy limits the target set; the requirement is for all three devices to receive the update. Exam caveat: distinguish installing shared vulnerability data on the Management Center from deploying configuration that incorporates it to managed devices; installation alone should not be assumed to update every device automatically. Practical check: verify that the Management Center reports the new data version, then confirm deployment completion and the expected version or policy status on each of the three devices before closing the window.