
A bank's policy forbids installing trusted certificates on user devices, so TLS decryption is off the table, yet engineers still need to spot an unusual client application and a bad certificate on outbound encrypted sessions. Which inspection approach should they enable on Secure Firewall Threat Defense to identify this traffic from metadata alone?
Select an answer to reveal the explanation.
Short Explanation
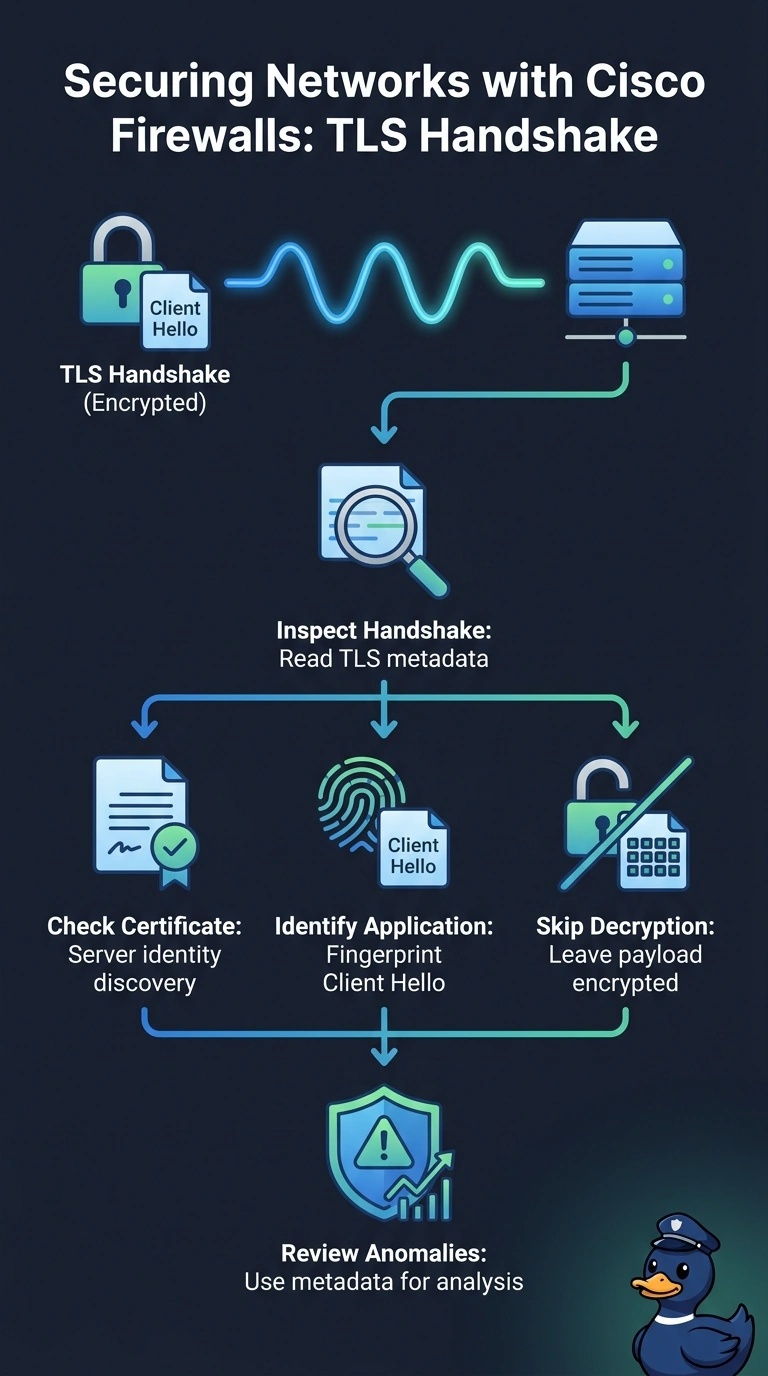
Enable the encrypted visibility engine to identify client applications from TLS fingerprints, and TLS server identity discovery to read the server certificate, all without decrypting payloads. It's like reading a package label without unwrapping the contents, which keeps you inside the bank's policy.
Full Explanation
The encrypted visibility engine fingerprints the TLS Client Hello to identify the client application or process behind an encrypted session, and TLS server identity discovery exposes the server certificate details (such as names and validity) without decrypting the payload or putting trusted certificates on user devices. Together they satisfy the bank's policy constraint and let engineers spot an unusual client and a bad certificate from metadata. NetFlow and DNS analytics can classify and baseline application behavior, but they do not assess the certificate in the TLS sessions; endpoint checks add a separate mechanism rather than network metadata. Relying on fingerprints alone misses the certificate requirement, and the claim that certificate problems appear only after decryption is wrong because the certificate is sent in the clear in TLS 1.2 handshakes. Endpoint inventory with certificate checks depends on agents, so it is not inspection from network metadata alone. Exam caveat: metadata-based visibility is not decryption; payload content stays unavailable, TLS 1.3 hides the server certificate so identity discovery works differently there, and the engine needs a Snort 3 device on a supported release. Practical check: in a test deployment, confirm that a controlled outbound TLS session shows the identified client application and the certificate details in connection events while no decryption is configured.