
A partner registers one public address for an app server and refuses sessions that arrive with translated source ports, while that server's existing auto NAT rule port-translates every session to the outside interface. The team needs a fixed one-to-one mapping for partner traffic only, with the auto NAT preserved for all other clients. Which NAT rule placement should they configure on the Threat Defense device?
Select an answer to reveal the explanation.
Short Explanation
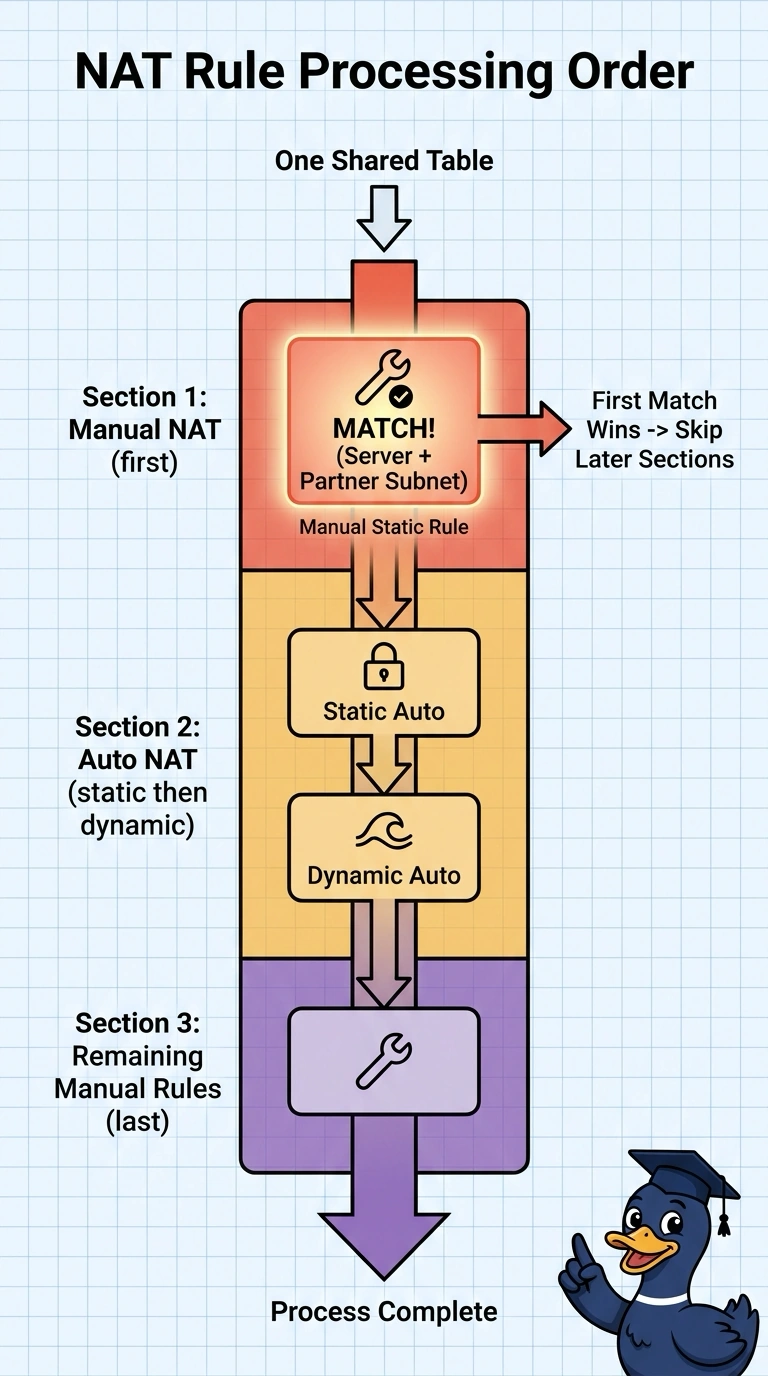
Give your partner traffic an express lane: place a manual static NAT rule in Section 1 that matches both the server object and partner subnet, ahead of auto NAT. That way, partner sessions get the fixed one-to-one mapping, while your auto NAT rule still handles everyone else.
Full Explanation
Threat Defense stores auto and manual NAT rules in one table split into three sections, evaluated in order and stopping at the first match. Section 1 holds manual NAT rules in the order you place them, Section 2 holds auto NAT rules with static rules before dynamic rules, and Section 3 holds the remaining manual rules, so a manual static rule naming both the server and the partner subnet in Section 1 is checked before that server's auto rule. Manual rules can match both source and destination, which is why partner-only translation needs one. Placing the manual static rule in Section 3 comes too late, because the auto rule in Section 2 already matches and evaluation stops there. Converting the auto rule to static changes the mapping for other clients that depend on its PAT behavior, and auto NAT cannot match on a destination address. A manual dynamic rule in the right section would still provide dynamic PAT rather than the required fixed one-to-one mapping. Exam caveat: Section 0 holds system-generated rules that you cannot edit. Practical check: run packet-tracer for the partner address and a normal client and compare the translations.