
A regional hospital is onboarding its first Secure Firewall Threat Defense appliance into the Secure Firewall Management Center. During TLS decryption, clients must trust the presented certificate from the root stores they already have, the SIEM must receive device logs, and operations wants FMC alerts when interface or HA status degrades. Which certificate, platform settings and health policy choices meet all three needs?
Select an answer to reveal the explanation.
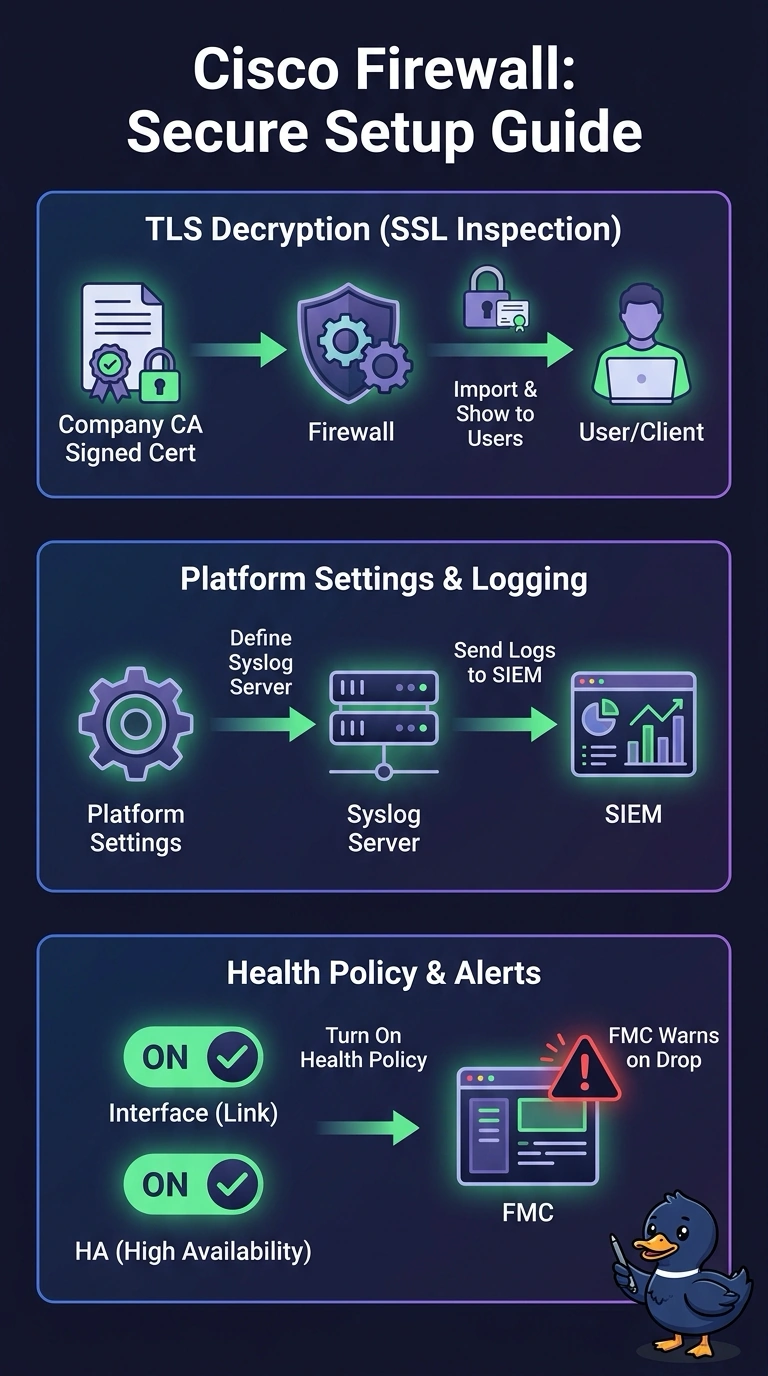
Short Explanation
Each requirement lives in a different place: the decryption certificate must chain to a CA your clients already trust, syslog sits in platform settings, and monitoring runs through the health policy. It's three switches on one panel, and flipping the wrong one leaves the circuit dark. Pull the certificate from your internal PKI so browsers accept the firewall's signature with no extra installs.
Full Explanation
Decrypt re-sign works only when the internal certificate the firewall presents chains to a certificate authority your clients already trust, so you import a CA-signed internal certificate and reference it in the decryption rule, and browsers accept the swap with no new installs. Platform settings are the home for device service configuration, including the syslog server that ships logs to the SIEM, while the health policy holds the monitoring modules such as interface status and Firewall Threat Defense HA status, and the management center raises its health alerts from those modules once the policy is applied. Generating a self-signed certificate fails the trust requirement, because no workstation has that issuer in its store. Reviewing logs in a local buffer fails the delivery requirement, since a buffer is a debugging aid that rolls over. Depending on SNMP traps from platform settings fails the alerting requirement, because traps are sent outward by the device instead of producing the management center's own health alerts on interface and HA state. Exam caveat: certificates serve different jobs such as management, remote access and decryption, so confirm the purpose before you assign one. Practical check: send a test log to the SIEM and open the health policy to confirm the interface and HA modules are enabled and applied to that device.