
A partner security team publishes command-and-control indicators as a STIX/TAXII feed that refreshes hourly, and every observable in it is an IPv4 address. Three FTD devices behind one Management Center must drop matching perimeter traffic with no manual list upkeep as the feed changes. Which Threat Intelligence Director setup meets the feed requirement?
Select an answer to reveal the explanation.
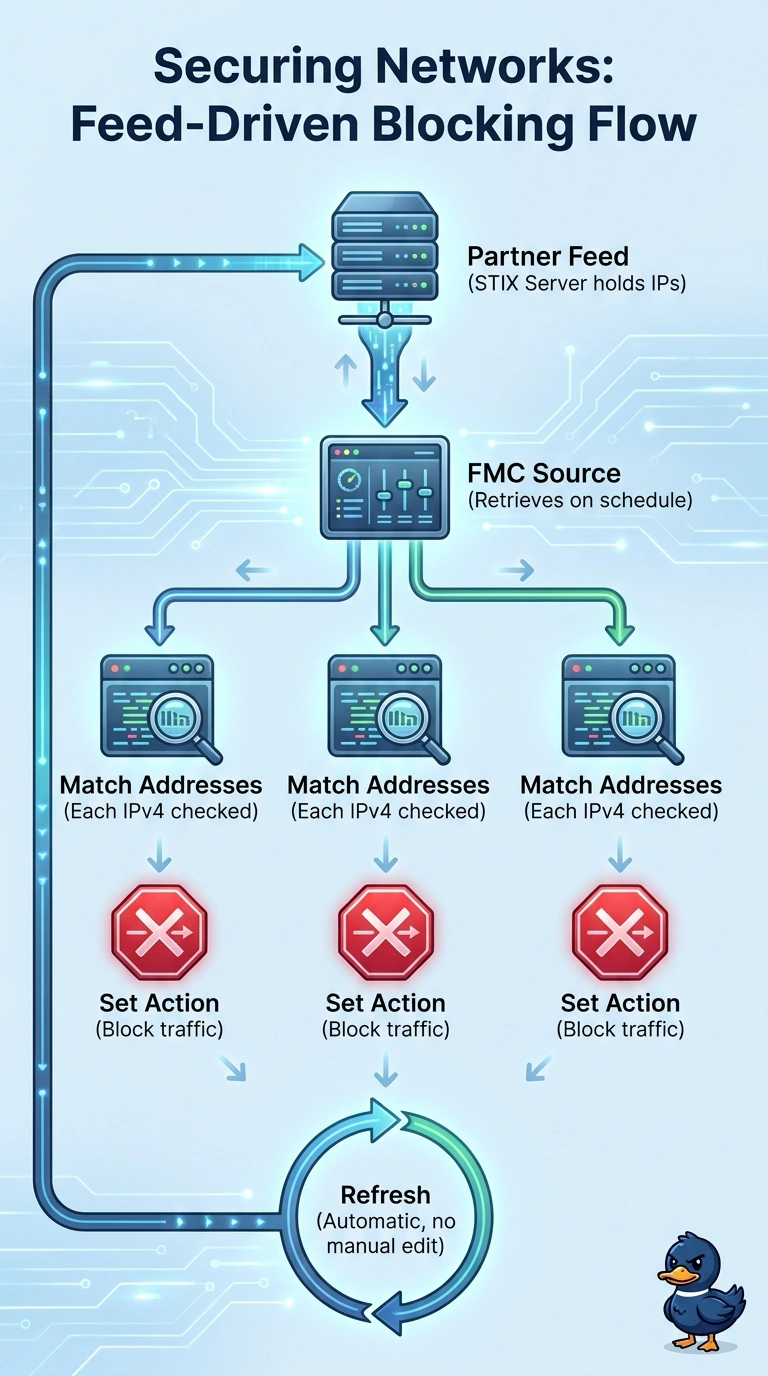
Short Explanation
The Management Center retrieves the feed on its schedule, so you don't have to maintain a list by hand. Threat Intelligence Director matches the IPv4 observables on the selected devices and blocks matching traffic after the feed is retrieved.
Full Explanation
A Threat Intelligence Director source points to the partner STIX/TAXII server, and the Management Center retrieves the feed on its configured schedule. You can apply the source to the selected devices and set the action to block, so matching traffic is blocked after the feed is retrieved and the updated indicators are applied. A rule using built-in Cisco reputation lists does not use the partner feed. A manually maintained object group requires an analyst to update the addresses when the feed changes. An inline intrusion rule can block matching traffic, but it does not ingest the feed automatically. Practical check: change one test address in the feed and confirm that a matching connection is blocked after the next successful retrieval and deployment.