
A university team is piloting Secure Firewall Threat Defense to inspect traffic flowing between its student VLANs and its server VLANs. The core switch stack must keep production traffic forwarding at all times, and the pilot's only approved resource is one spare 10 Gb capture port on that stack. Which passive monitoring deployment design meets every constraint?
Select an answer to reveal the explanation.
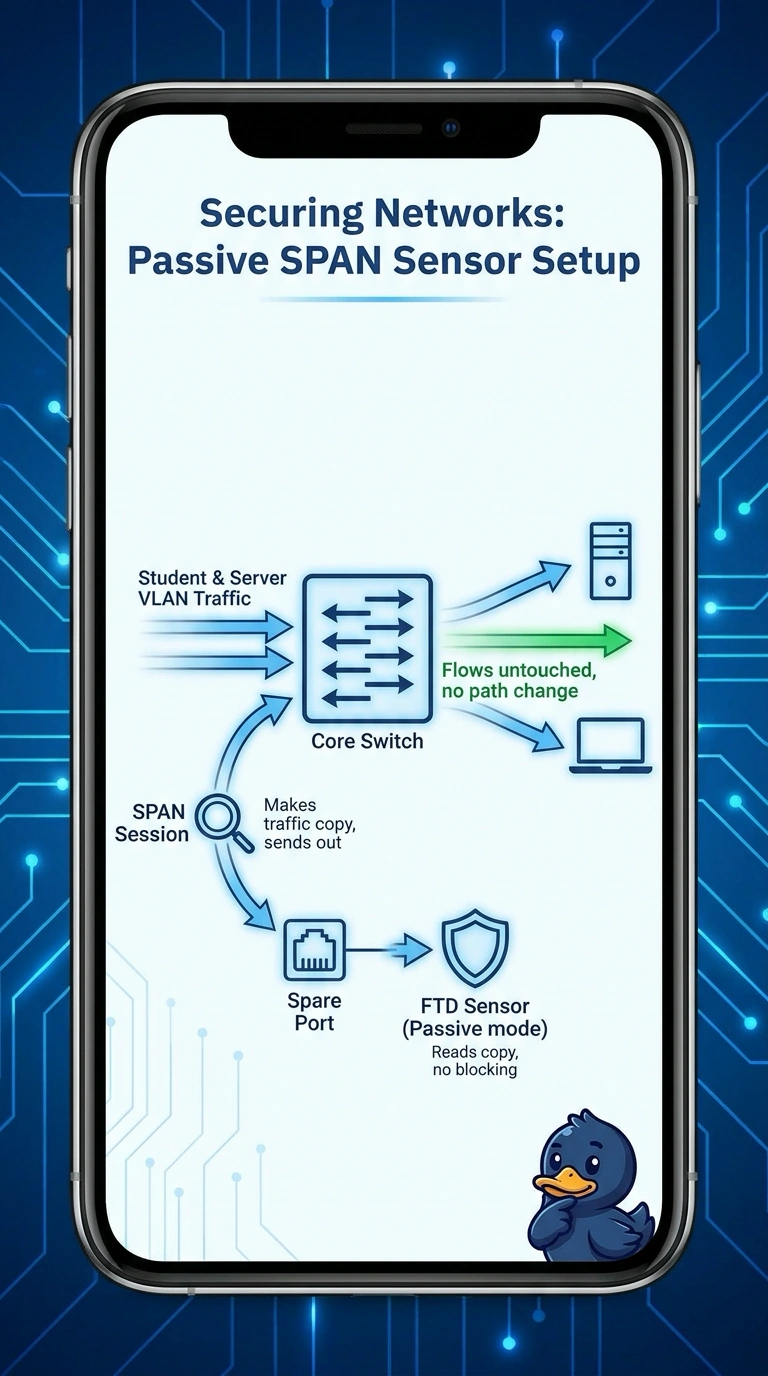
Short Explanation
You picked the copy that covers the right VLANs: the SPAN session mirrors student and server traffic to the spare port while the FTD just listens. That keeps production forwarding independent of the sensor, exactly what the stack demands. It's like having a second pair of eyes on the wire, so passive mode with SPAN gives you visibility without hardware in the path, and that's the win.
Full Explanation
In passive mode the FTD monitoring interface only receives a copy of frames, so it can inspect and alert while never becoming part of the forwarding path, and a SPAN session on the core switch stack replicates the student and server VLAN traffic to the single spare capture port, meeting both the coverage requirement and the rule that production forwarding must never depend on the sensor. An inline bridge pair with bypass set to fail open still leaves the stack's continuity riding on transceivers, patch cables and the bypass module, so that approach fails the requirement that forwarding continue unconditionally. A passive fiber tap in the server-facing trunk gives clean full-rate copies of exactly the right traffic, but the tap hardware and its cabling exceed the pilot's single approved resource. Mirroring only the guest and IoT links suits those segments, yet those links do not carry the student-to-server flows the pilot must inspect, so coverage misses the target traffic. Exam caveat: a SPAN egress port that is oversubscribed can silently drop mirrored packets, so passive visibility is not automatically lossless. Practical check: confirm on the switch that every VLAN and interface carrying the target flows is listed as a SPAN source, then watch the sensor interface counters for input drops.