
A city data center needs encrypted, policy-controlled connectivity from the civic DC to a cloud GPU region for hybrid AI. Which evaluation best addresses that requirement?
Select an answer to reveal the explanation.
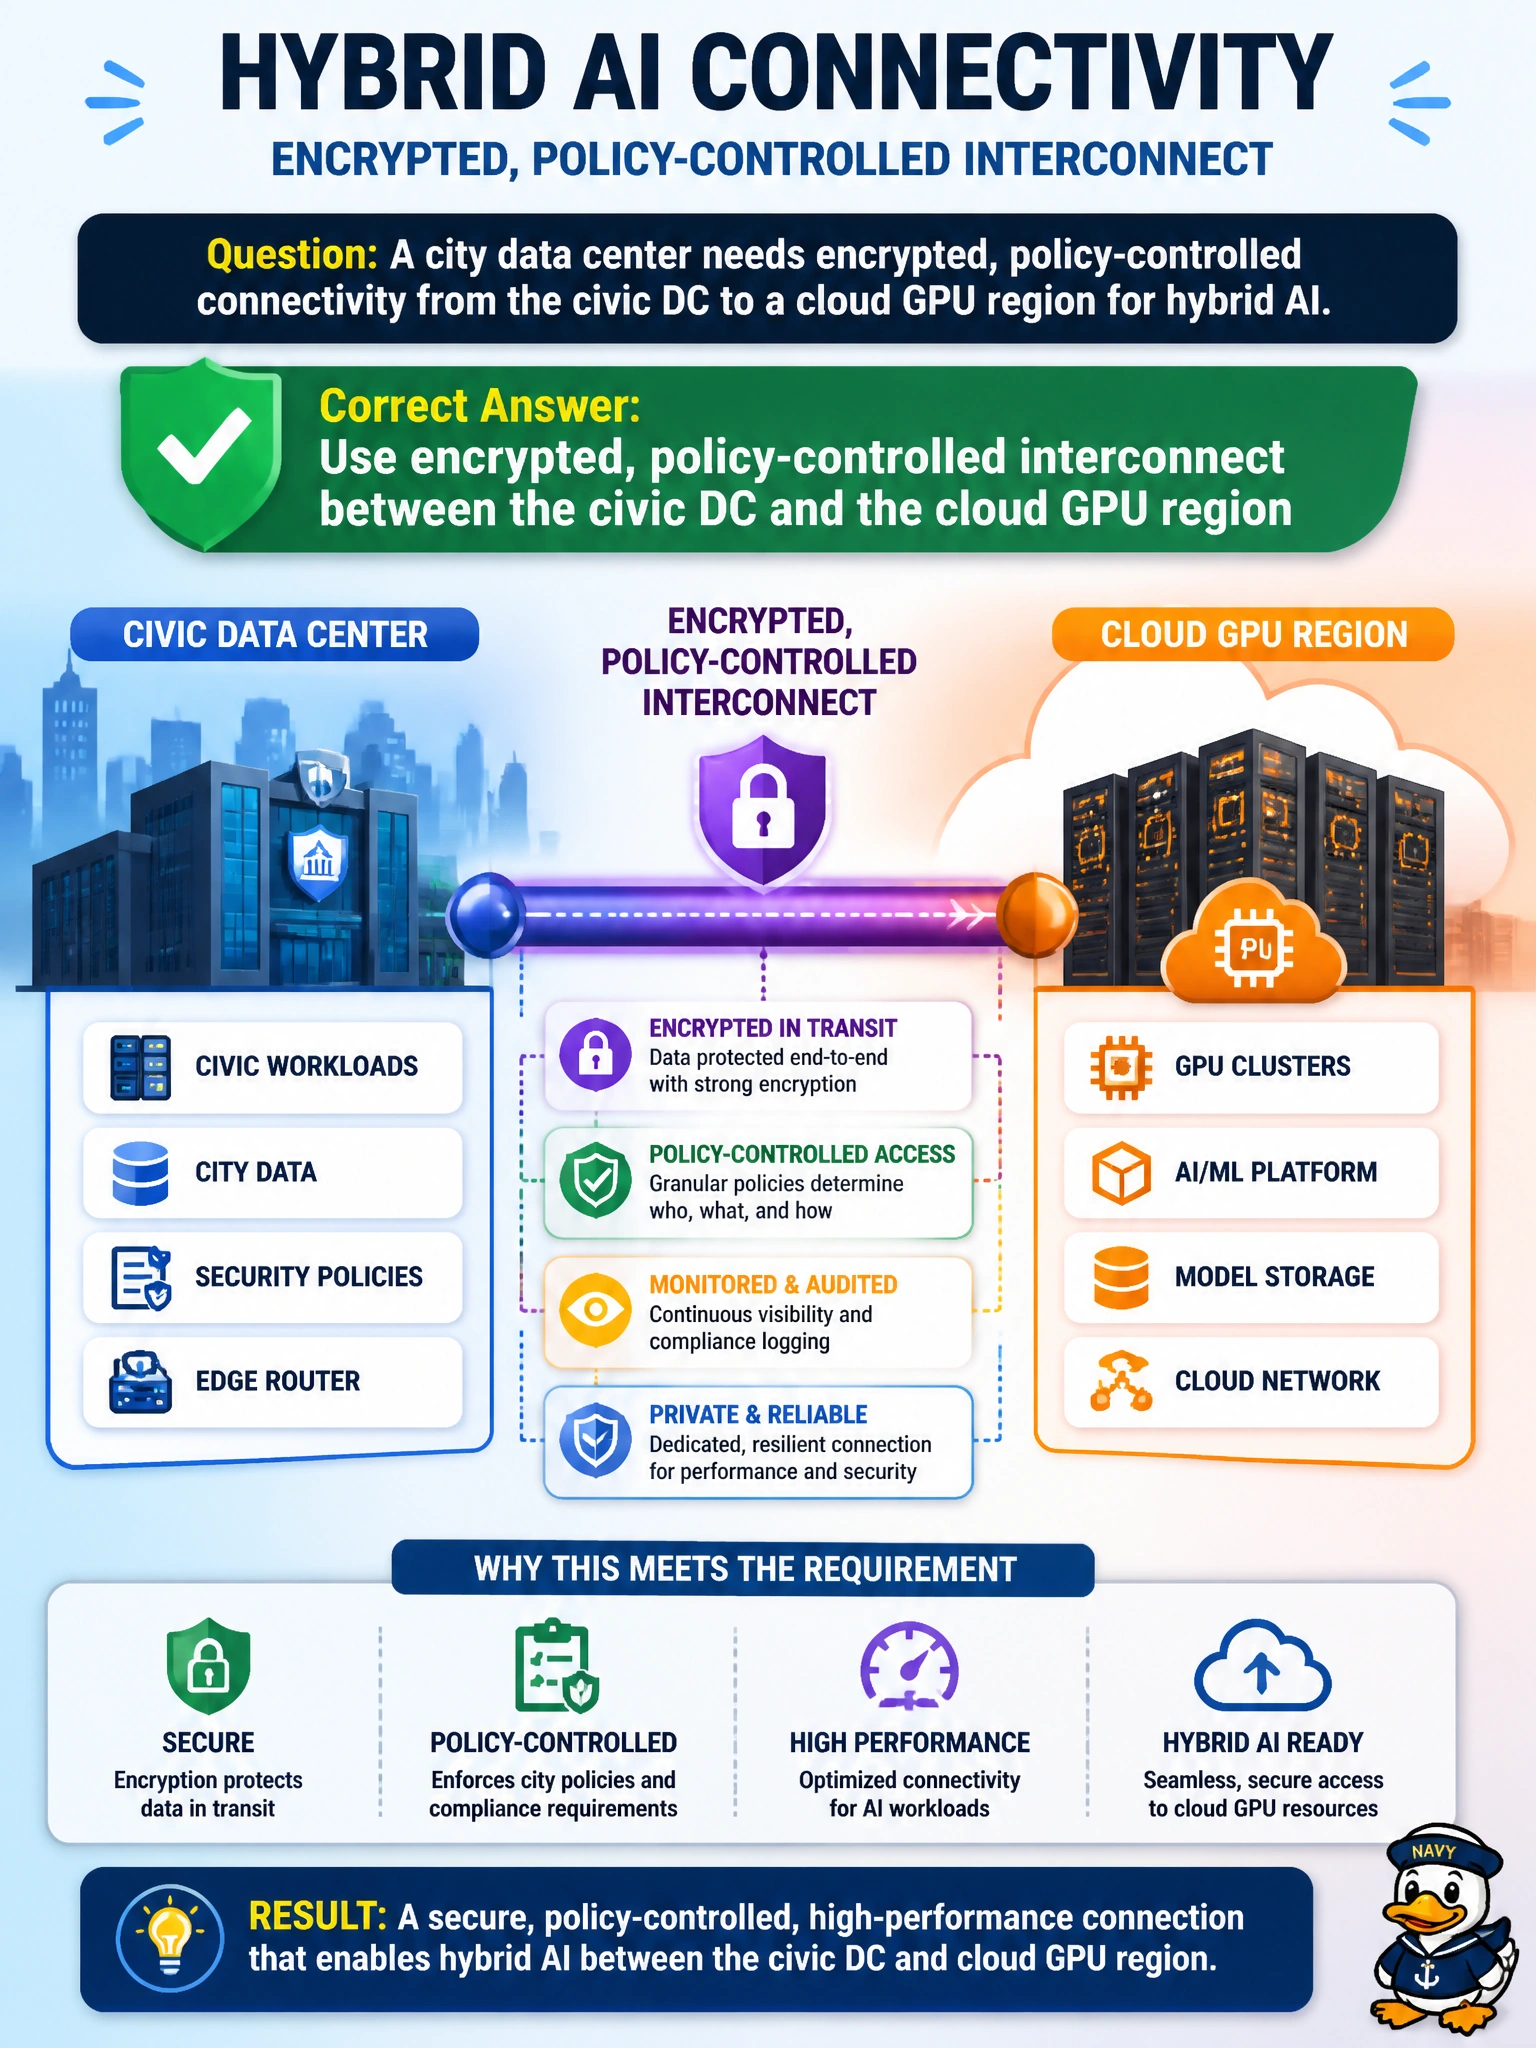
Short Explanation
Hybrid AI is fine — you're seeing an encrypted backup replication session that just copies backups, a policy-controlled DNS forwarding link that just handles name lookups, and an encrypted east-west peering mesh that's VPC-to-VPC fabric, and none of that's the encrypted, policy-controlled interconnect to the cloud GPU region you need. You want encrypted, policy-controlled pipes to that cloud GPU region. Think locked courier, not postcard.
Full Explanation
A city data center that needs encrypted, policy-controlled connectivity from the civic DC to a cloud GPU region for hybrid AI should use encrypted, policy-controlled interconnect between those sites. Hybrid training and inference exchange tensors, features, and control plane calls that must stay confidential and constrained by municipal policy—encryption in transit plus identity/policy gates on who may use the path. Using an encrypted backup replication session between the civic DC and the cloud GPU region copies backup snapshots on a schedule but does not establish the encrypted, policy-controlled interconnect for live hybrid AI training and inference, so it fails the requirement. Using a policy-controlled DNS forwarding link between the civic DC and the cloud GPU region controls name-resolution forwarding but does not provide encrypted transport for AI tensors, features, and control-plane calls, so it does not satisfy the requirement. Using an encrypted east-west VPC peering mesh between the civic DC and the cloud GPU region provides VPC-to-VPC east-west fabric but does not provide the policy-controlled hybrid interconnect from the civic DC to the cloud GPU region, so it fails the requirement. Exam caveat: Domain 2.5 evaluates hybrid AI for secure connectivity to cloud integration points; "we have a backup, DNS, or peering link somewhere" only counts if it is the enforced, policy-bound interconnect path for the GPU workloads in scope. Operational check: verify hybrid city-DC ↔ cloud GPU flows traverse the designated encrypted interconnect, fail closed without valid identity/policy, and never fall back to cleartext Internet for the same workloads.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.