
A firm has two secure internet gateway providers configured. Regulated web must use the approved provider. The data policy sends it to the other provider. Both tunnel sets are up. What should the policy use?
Select an answer to reveal the explanation.
Short Explanation
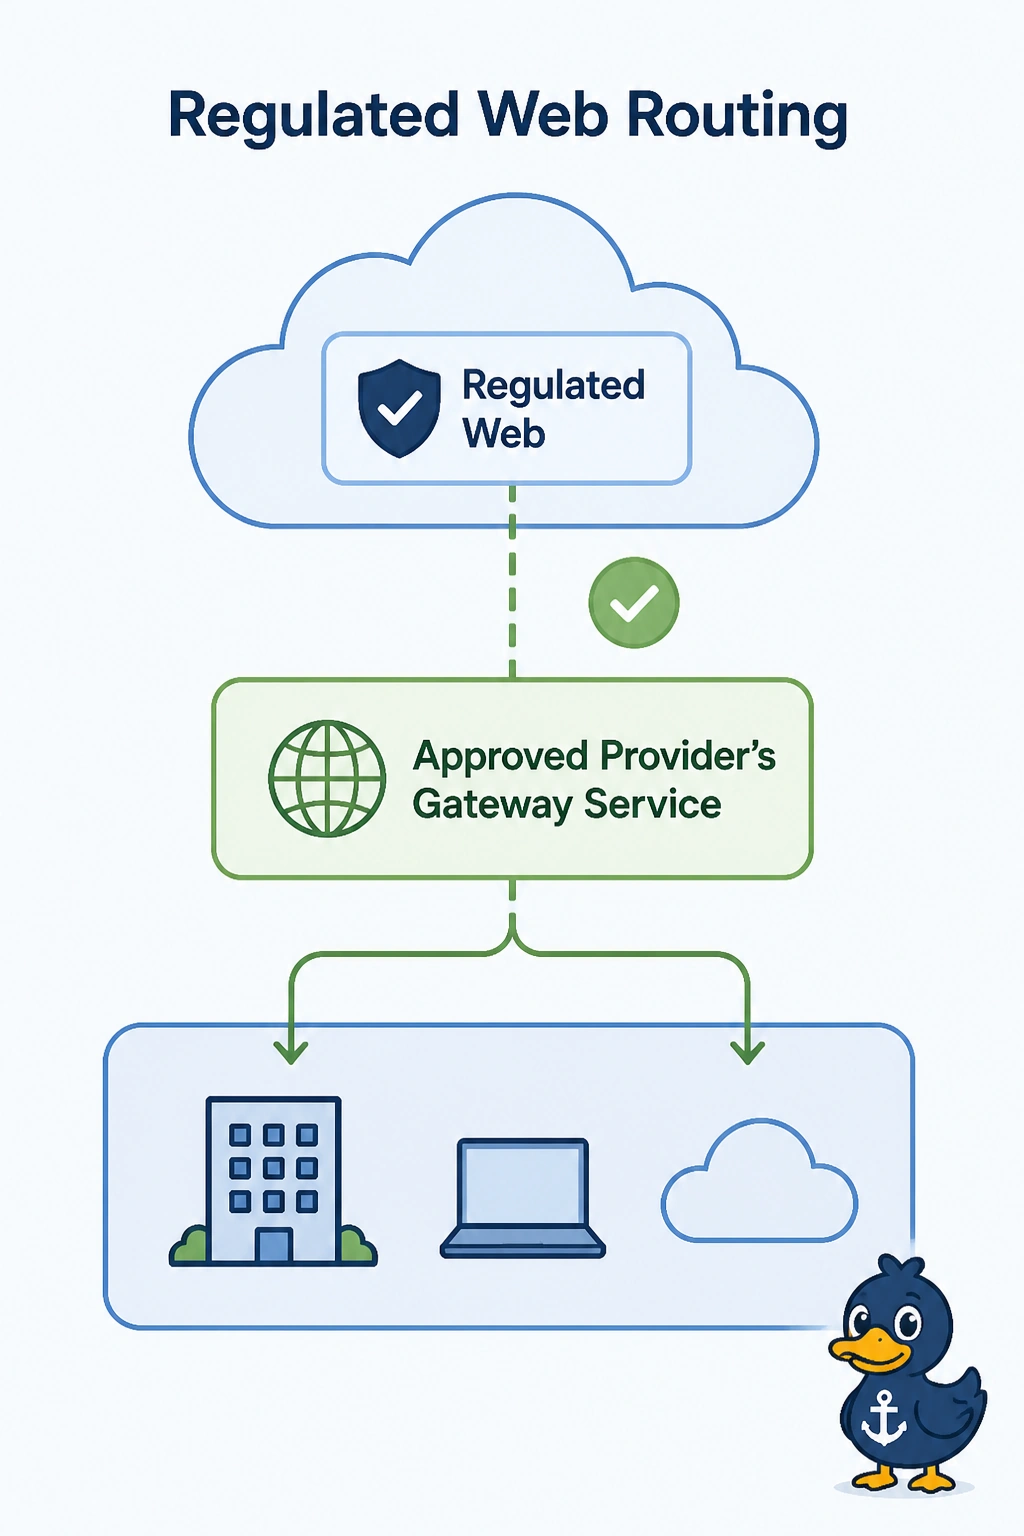
Both inspection tunnels are up, and you sent the regulated web to the one that was not approved. You point that policy at the approved provider. The other provider being reachable does not make it the one the rule named.
Full Explanation
The Secure Internet Gateway feature can build tunnels to more than one provider. The data policy decides which service a flow uses. Regulated web is matching the provider the firm did not approve, so change that match to the approved provider's service. A tunnel that comes up first is not automatically acceptable. The IaaS cloud gateway reaches a private VPC. It does not apply the approved provider's inspection. VPN 512 is management and does not select a provider for user web. Exam caveat: an earlier sequence that matches all web can still send regulated traffic to the wrong provider after you fix the later line. Put the specific match first. Operational check: a regulated session should appear in the approved provider's log and not in the other provider's log.