
Cloud OnRamp for Multicloud already builds the path from a branch into a VPC. An older manual IPsec tunnel on the same edge also aims at that VPC and blackholes some flows. What should carry the VPC?
Select an answer to reveal the explanation.
Short Explanation
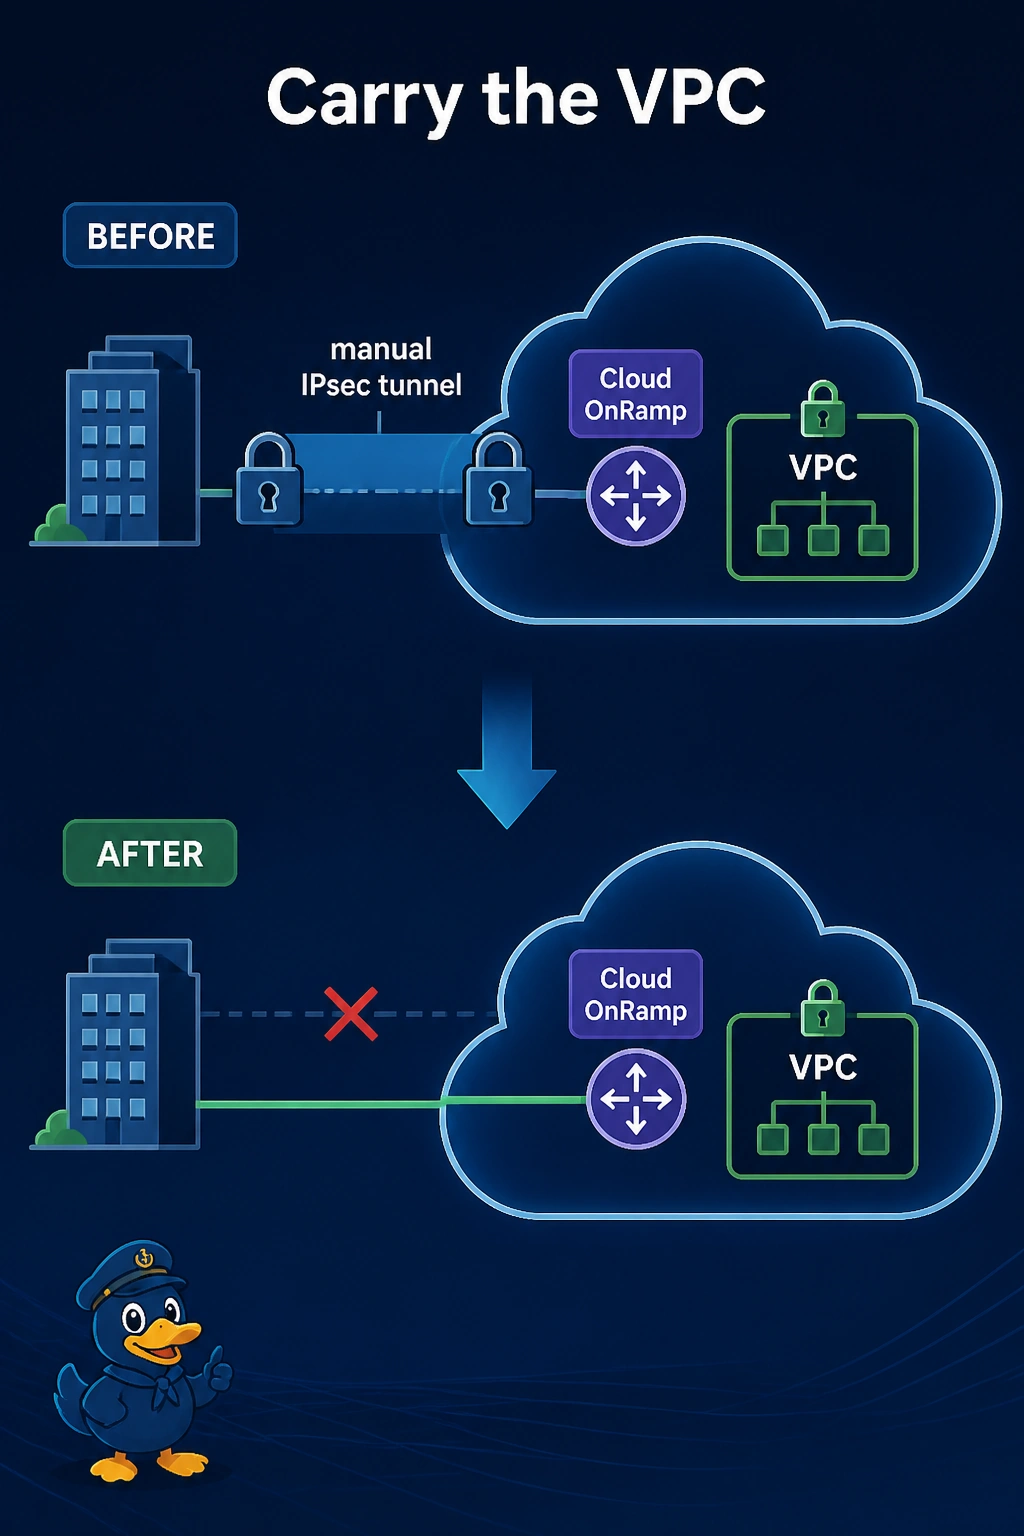
Two paths into the same VPC are arguing, and the old manual tunnel is the one that was not supposed to stay. You keep the Cloud OnRamp gateway and remove the manual IPsec tunnel. VPN 512 does not carry the VPC for you.
Full Explanation
Cloud OnRamp for Multicloud is the overlay path into the VPC. A leftover manual IPsec tunnel on the same edge, aimed at the same prefixes, can win a route or a policy and blackhole flows the gateway would have carried. Remove the manual tunnel and let the gateway own the VPC. Keeping the manual tunnel and dropping OnRamp throws away the overlay the branch is supposed to use. VPN 512 is management. It does not replace either path. A voice SLA does not choose between a manual tunnel and OnRamp. Exam caveat: remove the route and the data policy that point at the manual tunnel, not only the tunnel interface. A route left behind still blackholes the prefix. Operational check: the branch should show the VPC only through the cloud gateway TLOC, and the manual peer should be gone from the IPsec session table.