
A new Catalyst SD-WAN edge has its internet interface in VPN 0 and no default route in that VPN. BFD to the Azure cloud gateway's public address never starts. What is missing in VPN 0?
Select an answer to reveal the explanation.
Short Explanation
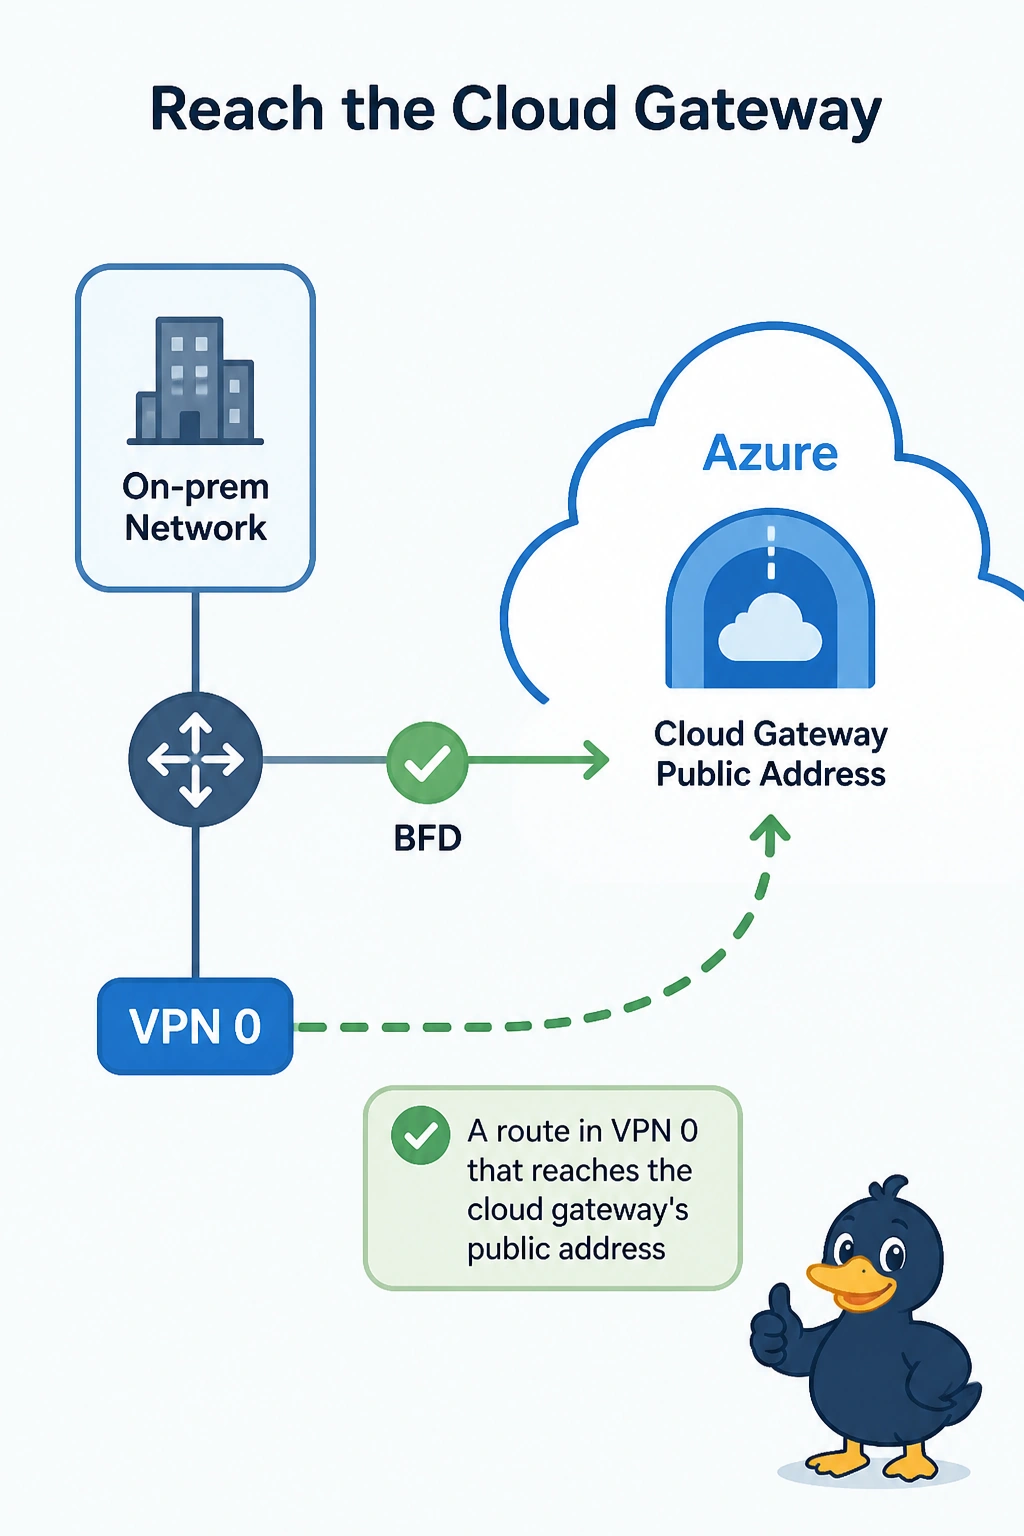
The interface is in the right VPN and the map in that VPN is blank. You add a route in VPN 0 that reaches the cloud gateway's public address. A default in the user VPN does not steer the underlay, and BFD does not wait for a BGP session that would ride the tunnel.
Full Explanation
BFD to a public cloud gateway is sent from VPN 0. The internet interface is already there, and VPN 0 has no route that can reach the gateway's public address, so the session never starts. Add a default or a specific route in VPN 0 out that interface. A default in VPN 10 is a service-side route. It is not the transport route used to reach a public TLOC. An OSPF default in VPN 512 stays in the management VPN. It is not copied onto the internet transport. BGP to the cloud gateway is not a prerequisite for the underlay route. The route has to exist before BFD, and the gateway is not a BGP neighbor inside VPN 0. Exam caveat: do not point the route to the gateway's public address back at a tunnel that is not up yet. Use the physical internet interface. Operational check: show ip route vpn 0 for the gateway address should list the internet interface, and show sdwan bfd sessions should then start.