
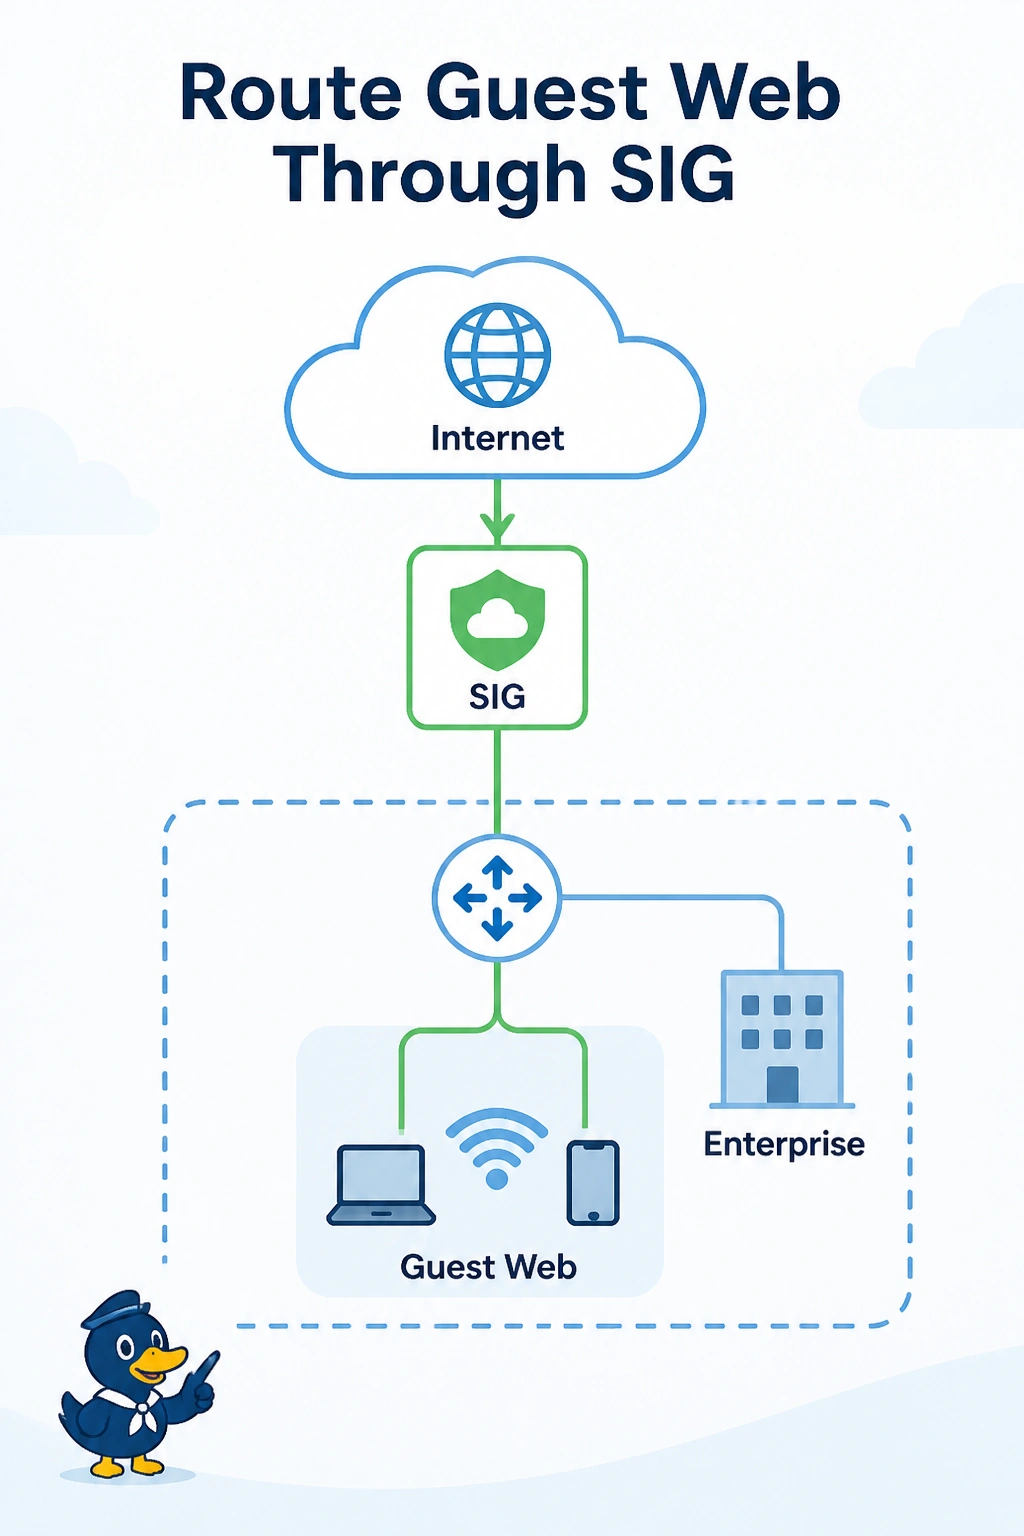
A resort's SIG tunnels are up. Guest web still exits uninspected. The data policy matches guest web and sets the next hop to the local internet interface, not the SIG. What should that policy set?
Select an answer to reveal the explanation.
Short Explanation
The inspection lanes are built, and the policy is waving guest traffic out the raw internet door. You set the SIG as the next hop for guest web. A cloud gateway TLOC is a different attachment, and VPN 512 will not carry those sessions.
Full Explanation
SIG tunnels being up does not inspect traffic that a data policy sends somewhere else. This policy matches guest web and then sets the local internet interface as the next hop, so the flow leaves uninspected. Change that action to the SIG. A cloud gateway TLOC belongs to IaaS connectivity. Pointing guest web at it does not turn a DIA next hop into SIG inspection. VPN 512 is management. Guest web is not carried there by raising an OMP preference. A BGP neighbor in VPN 10 is not how a SIG tunnel is selected. The steer is a data-policy action. Exam caveat: match only the guest VPN. A next-hop change that also catches staff traffic will drag staff onto the SIG if that was not the design. Operational check: after the action names the SIG, a guest session should disappear from the uninspected interface counters and appear in the provider log.