
A branch internet interface is up and has no NAT. Cloud OnRamp for SaaS is enabled for Microsoft 365, and local probes from that interface do not run. A second interface with working NAT does probe. Why is the first interface skipped?
Select an answer to reveal the explanation.
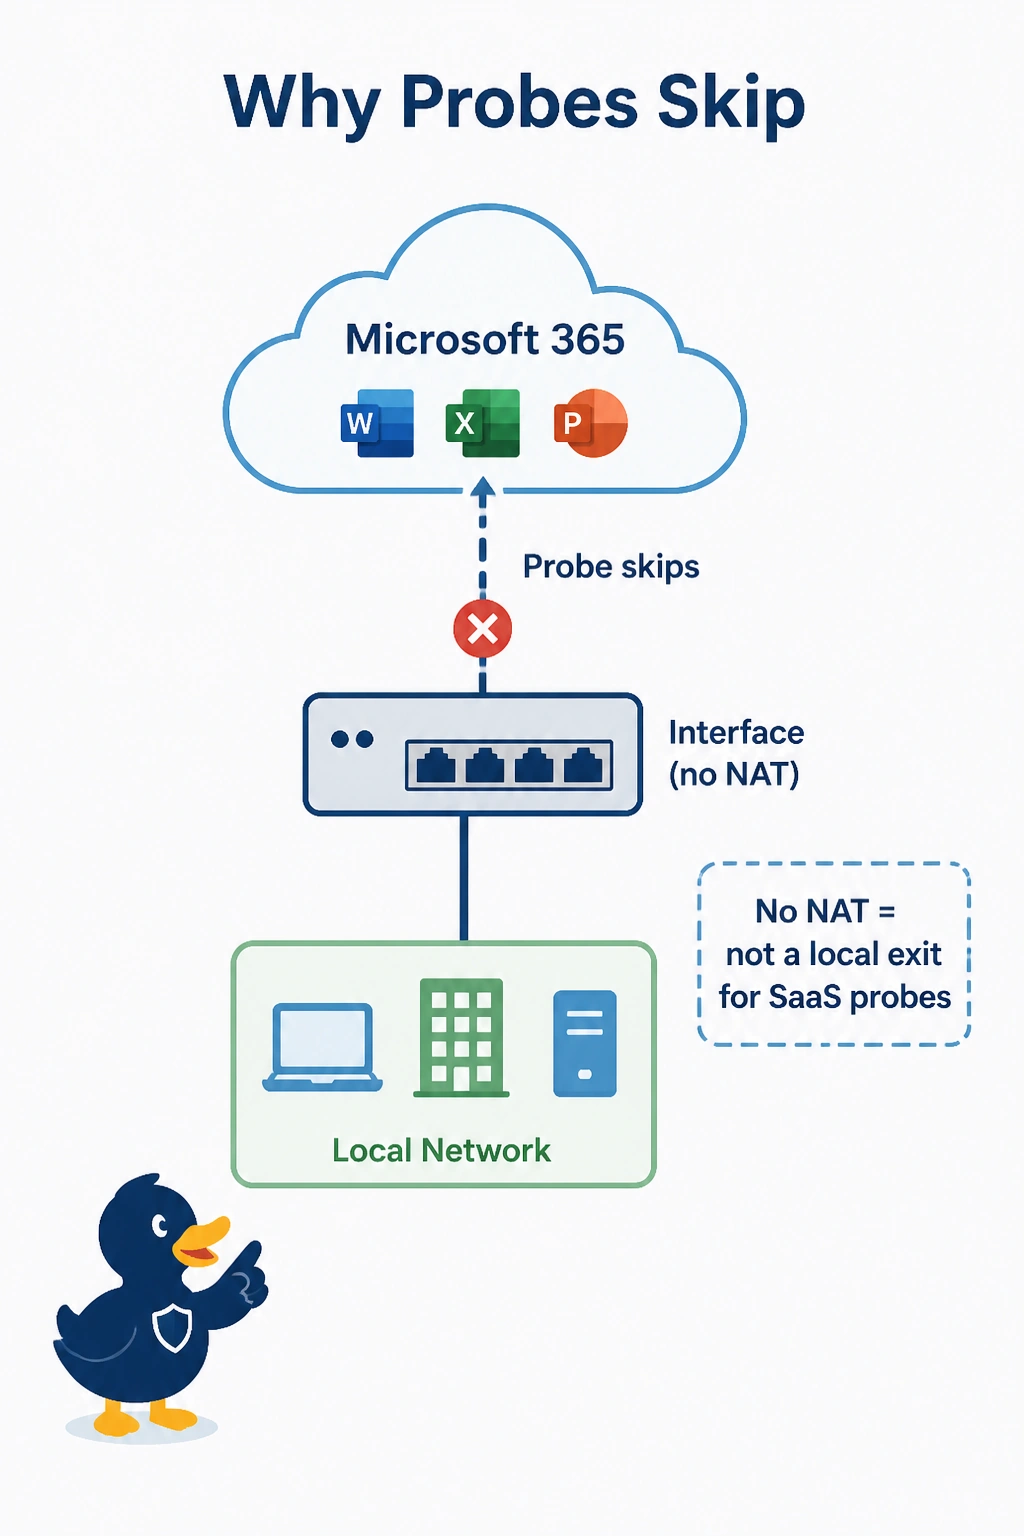
Short Explanation
An interface that cannot hide the branch behind NAT is not a door OnRamp will use for a local probe. You left NAT off the first internet interface, so probes stay on the interface that has working NAT. Shutting OMP would not teach the first interface how to exit.
Full Explanation
Cloud OnRamp for SaaS local probes use a local internet exit that can reach the application, which on Catalyst SD-WAN means a NAT-enabled DIA interface. An up interface with no NAT is not that exit, so probes do not run there. The second interface has working NAT and does probe, which isolates the missing NAT. Probes do not require the interface to be administratively down. That would remove the exit. Disabling OMP is not a prerequisite for probing and would harm the overlay. A zone-based firewall does not select an unaddressed interface as the probe source. Exam caveat: adding NAT later is not enough if a data policy pins Microsoft 365 to a gateway. The probe and the steering policy still have to agree. Operational check: enable NAT on the first interface, confirm it is an accepted DIA exit, and confirm a local Microsoft 365 probe appears on it.