
On a Catalyst SD-WAN edge, staff web through the SIG works and guest web fails. The guest zone pair denies web, the staff zone pair permits it, and both VPNs use the same SIG tunnel. What explains the guest failure?
Select an answer to reveal the explanation.
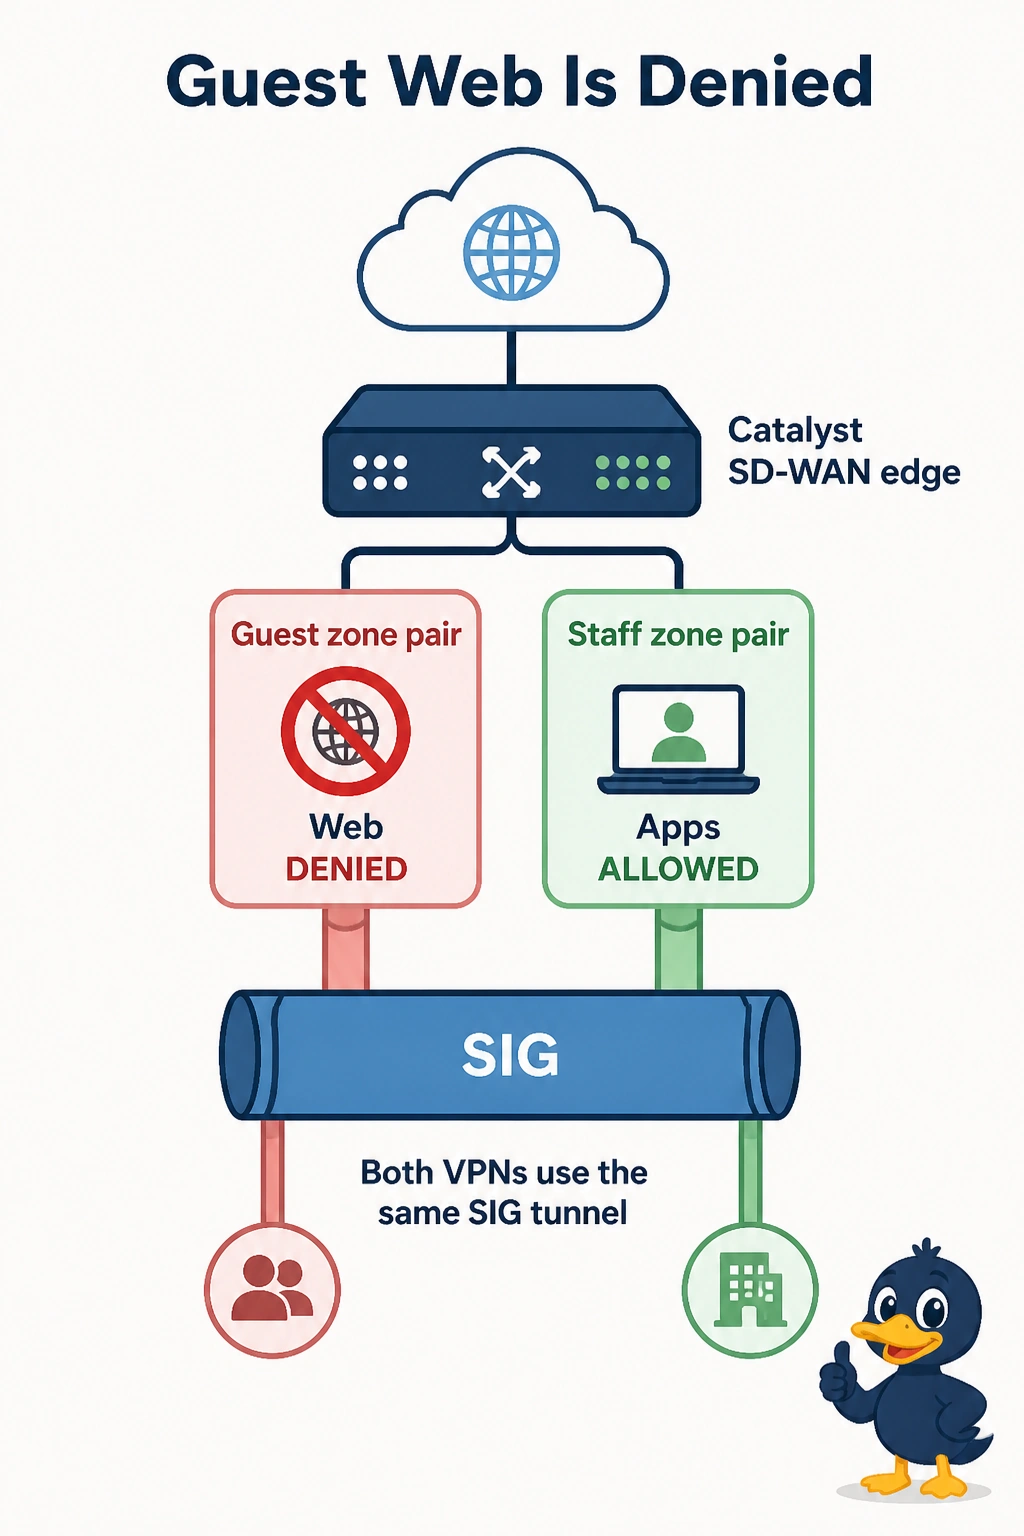
Short Explanation
You can see why staff web works: the shared SIG tunnel is available, but the guest zone pair denies web before guest traffic can reach it. A down tunnel would affect staff too, so the zone-pair policy explains the guest failure.
Full Explanation
The SIG tunnel is shared, but that does not mean every VPN can use it: the zone-based policy still determines which traffic may proceed. Here, the guest zone pair denies web, so guest sessions are dropped before they can use the SIG tunnel; the staff zone pair permits web, which is why staff sessions succeed. A down SIG tunnel would affect both populations, so staff web working is evidence against the tunnel being down. Cloud OnRamp for Multicloud does not, as a consequence of this guest zone-pair denial, replace the guest default with a VPC route; the stated policy already explains why guest web fails. A strict SLA can drop traffic when a matched application’s path misses a quality target, but that does not explain the difference shown here: the guest zone pair denies web while staff web is permitted on the same tunnel. Exam caveat: once the guest zone pair permits web, verify that the data policy still steers guest traffic into the SIG; otherwise, the traffic might not receive SIG inspection. Practical check: confirm the guest zone-pair counter no longer increments drops for web, then check that a new guest session appears in the SIG log alongside staff sessions.