
A hotel set the Catalyst SD-WAN Secure Internet Gateway feature to IPsec. The provider endpoint in the guide accepts only GRE. Both SIG tunnels stay down. What should be changed?
Select an answer to reveal the explanation.
Short Explanation
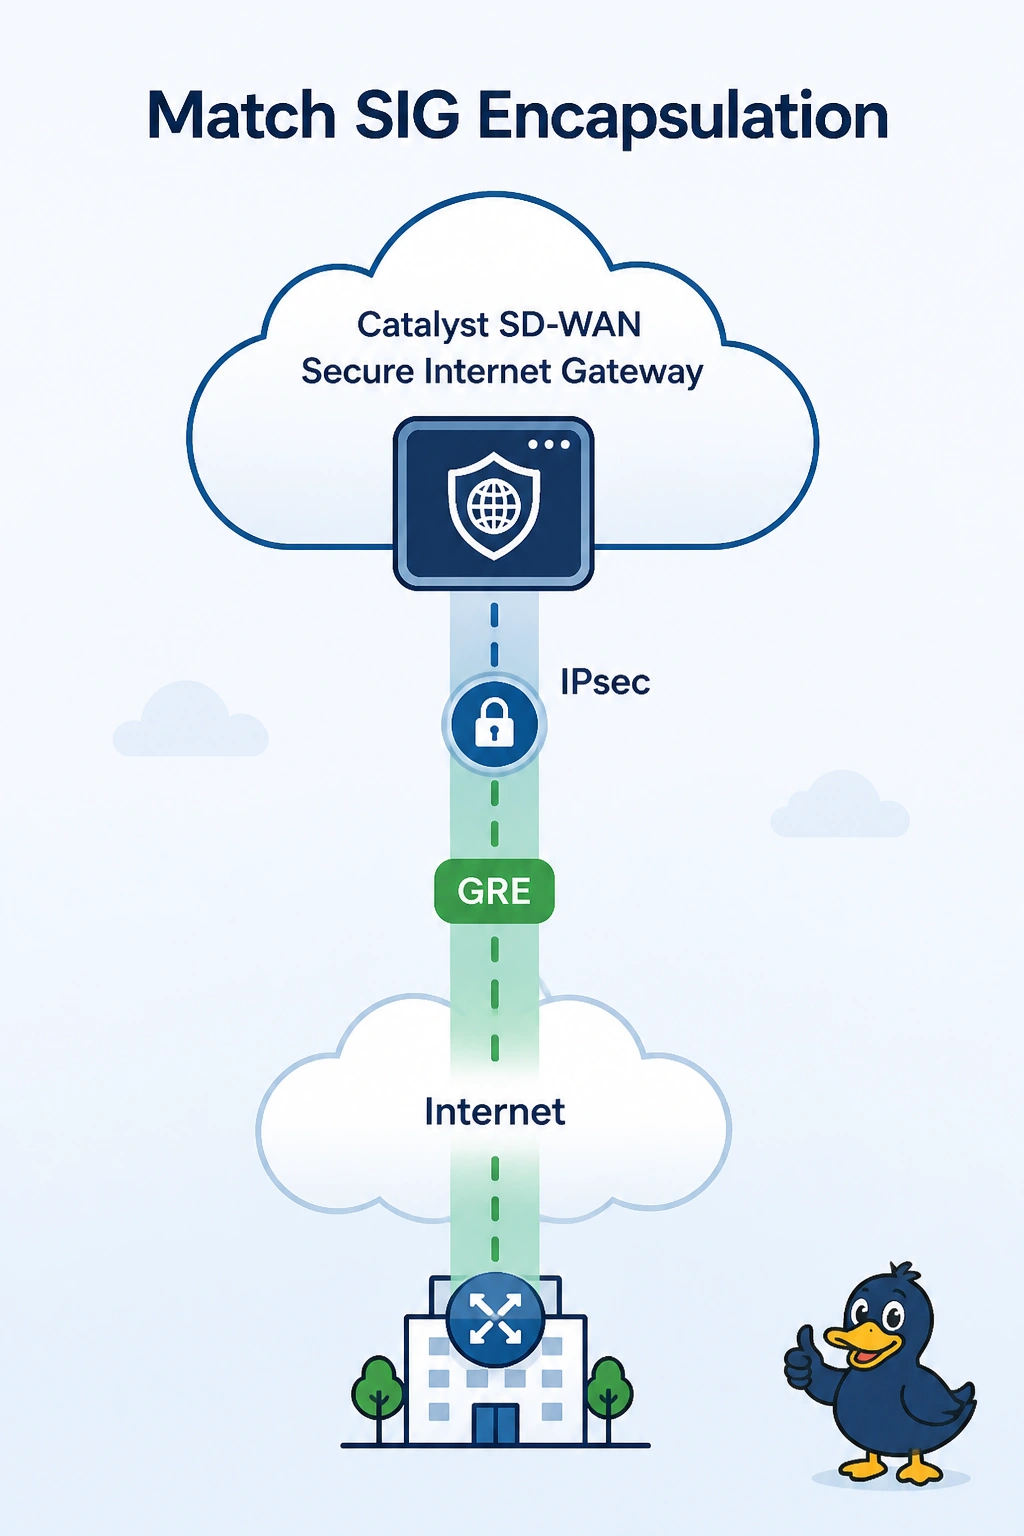
You are speaking IPsec to a dock that only unloads GRE. You change the SIG encapsulation to GRE so it matches the provider guide. The tunnels stay down until that encapsulation agrees, and an AWS cloud gateway is not the device you are failing to reach.
Full Explanation
The Secure Internet Gateway feature has to use the encapsulation the provider endpoint accepts. This guide says GRE only, and the hotel configured IPsec, so the tunnels never establish. Change the feature to GRE and keep the provider destination. An AWS cloud-gateway color belongs to Cloud OnRamp for Multicloud. These tunnels are SIG tunnels, and the far end is the security provider, not an IaaS gateway. The OSPF area on the hotel LAN does not authenticate a SIG tunnel. An Azure BGP ASN does not terminate this provider's GRE endpoint unless the design was built that way, and the stem points at the SIG guide, not at an Azure VPN gateway. Exam caveat: some providers accept both encapsulations on different endpoints. Use the endpoint and the encapsulation from the same line in the guide, not IPsec from one product and a GRE address from another. Operational check: after the feature is set to GRE, both SIG tunnels should come up and a guest web flow should show up in the provider portal.