
After BGP to Azure came up, a campus IOS XE router started sending its own internet traffic into the tunnel. Azure is advertising 0.0.0.0/0, and the router has no inbound filter. What caused the change?
Select an answer to reveal the explanation.
Short Explanation
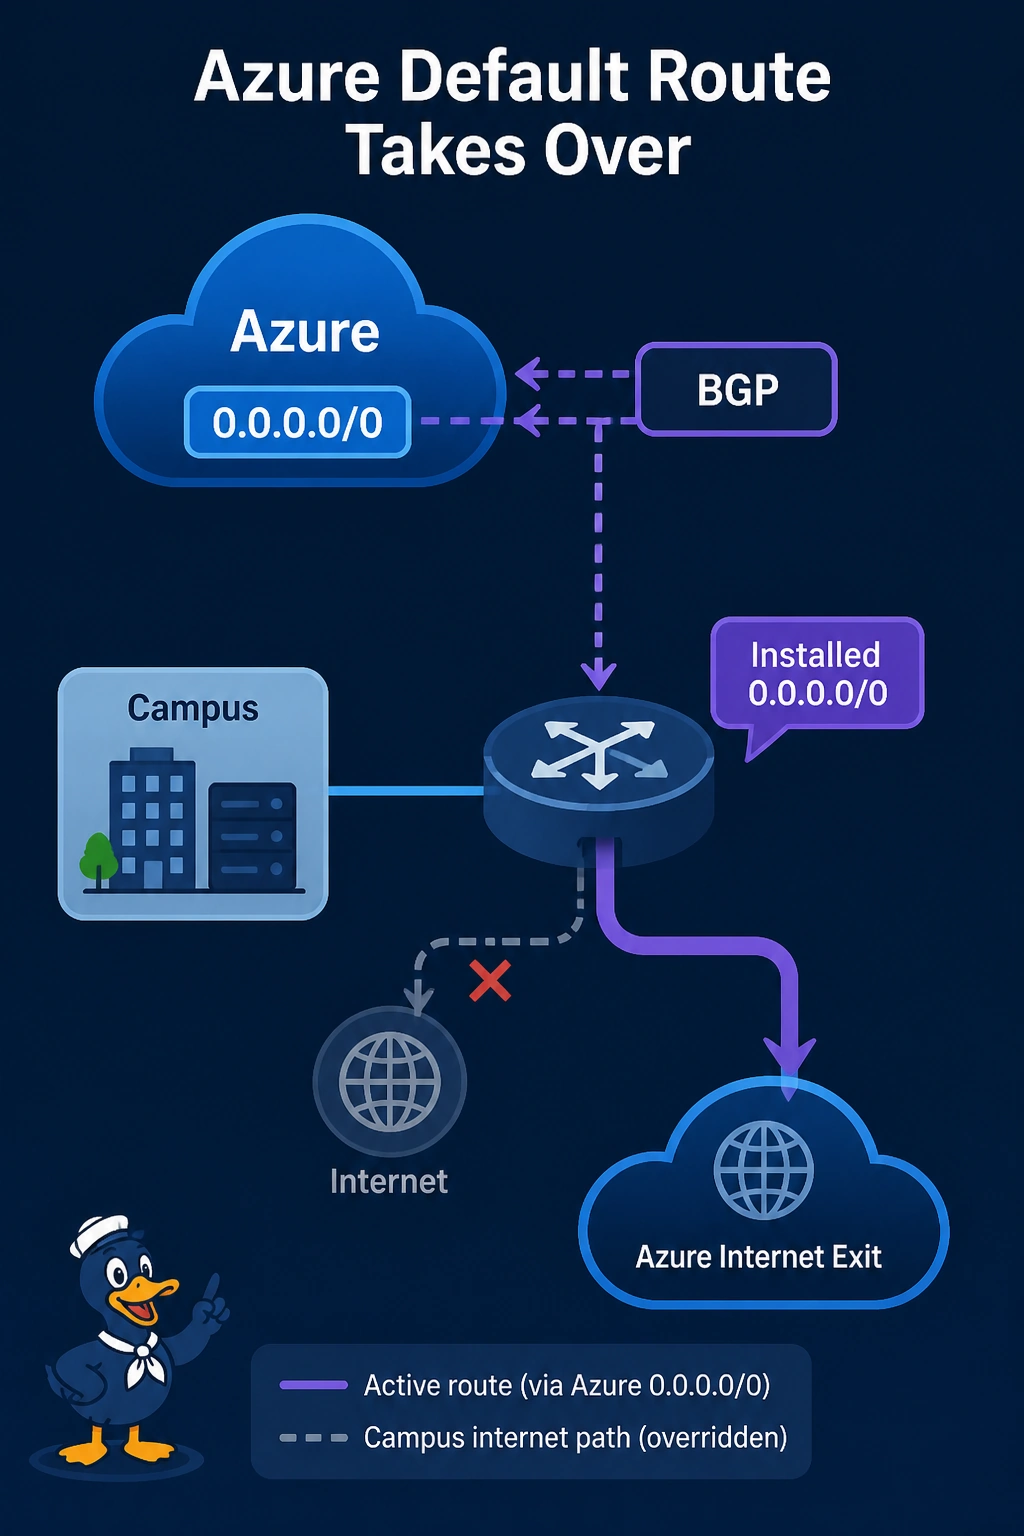
Azure handed you a default route and you put it in the table. You installed 0.0.0.0/0 from BGP, and it stole the campus internet exit because the tunnel is up and the route could be learned. A dead SA would not be installing a BGP default.
Full Explanation
An inbound BGP advertisement of 0.0.0.0/0 from Azure becomes the campus default if nothing filters it and it wins the routing decision. Internet traffic that used to leave locally now enters the tunnel. That matches the change. Filter the default inbound, or lower its preference, if the campus should keep its own internet exit. A failed IPsec SA would drop the BGP session and remove the learned default. It would not install the tunnel as a default only while the SA is down. The Azure VPN gateway does not flood an OSPF default, and OSPF is not the protocol that brought this route in. The IKE lifetime does not rewrite the routing table at rekey. A rekey that succeeds leaves BGP alone. Exam caveat: if the design is forced tunneling on purpose, the Azure default is correct and the campus must be ready to send internet traffic that way. This symptom is an accidental takeover. Operational check: show ip route 0.0.0.0 should no longer point at the Azure neighbor after the inbound filter denies that prefix.