
A plant IOS XE router still targets an AWS tunnel outside address from last quarter's notes. IKE to that address times out. The AWS console shows a different outside address for the up tunnel. What should be updated?
Select an answer to reveal the explanation.
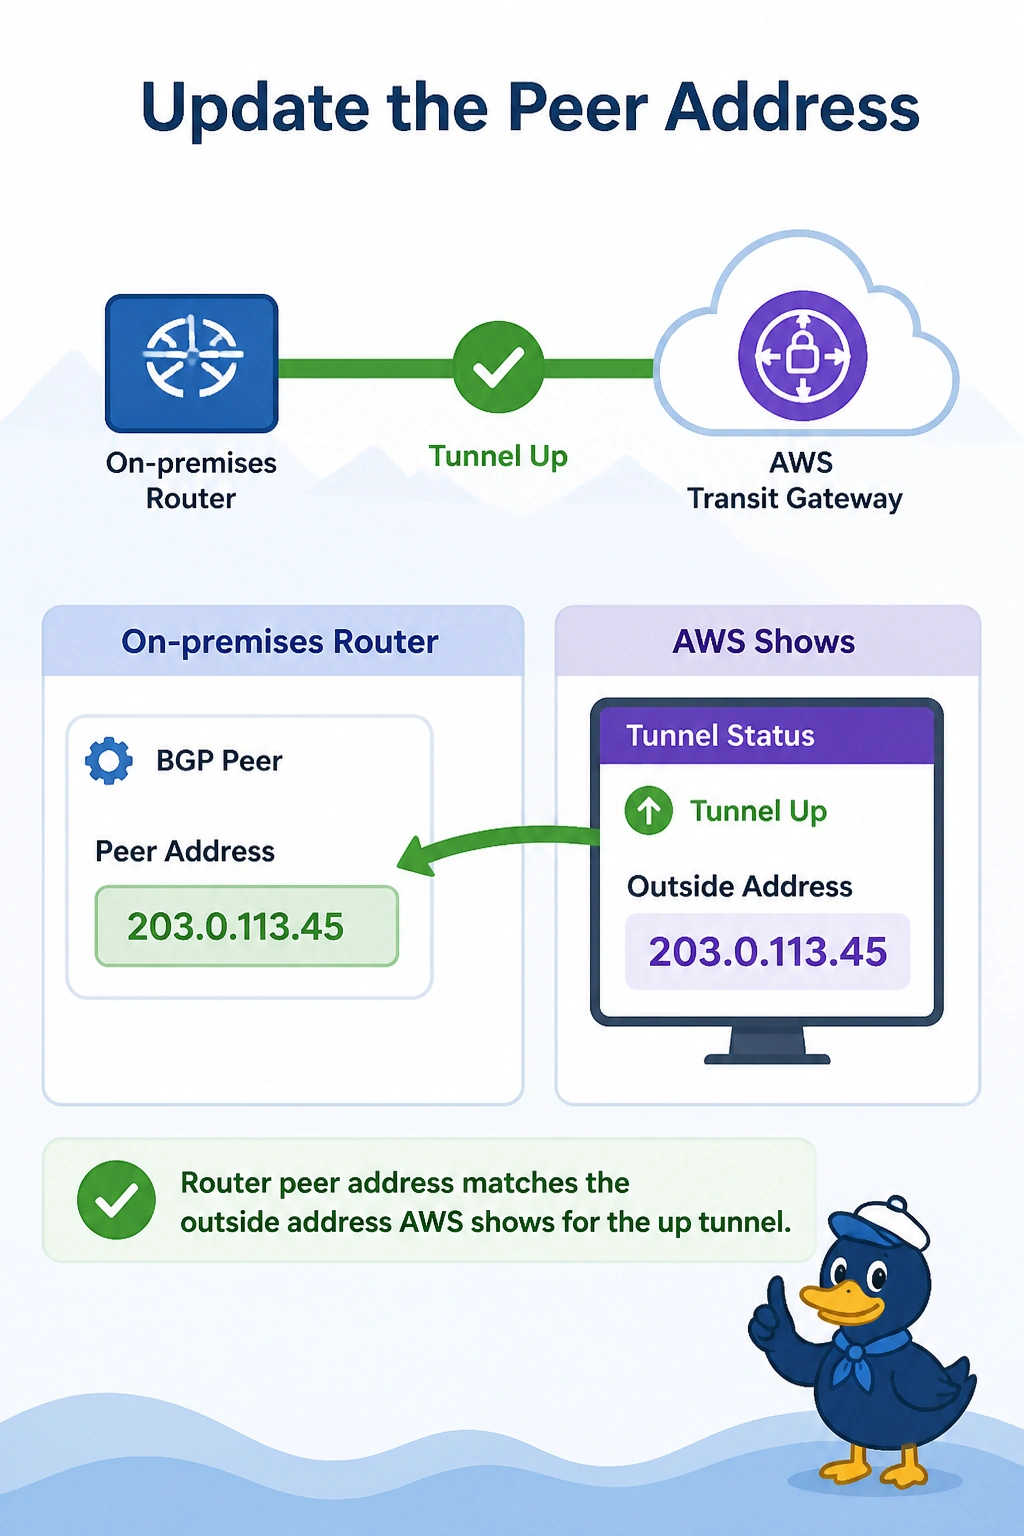
Short Explanation
You are still knocking on last year's door. You point the router at the tunnel outside address the AWS console shows now. A BGP password does not move an IKE peer, and OSPF is not where AWS stores that address.
Full Explanation
AWS tunnel outside addresses are the IKE destinations. If the connection was rebuilt or the endpoint changed, the router must use the address the console shows now. Traffic to the old address times out because nothing is answering IKE there, even if a tunnel exists on the new address. Update the peer and the tunnel destination. A BGP password is consulted only after IKE and the inner TCP session exist. It does not select the outside address. The OSPF router ID is a local OSPF identifier. AWS does not publish it as the tunnel outside address, and the virtual private gateway does not run OSPF. An SD-WAN organization name belongs to a controller overlay. This plant router is a standalone IOS XE peer to AWS. Exam caveat: each AWS VPN connection has two outside addresses. Update the tunnel that failed, and do not copy one tunnel's address onto both. Operational check: the router peer should match the console's outside IP for that tunnel, and show crypto ikev2 sa should then reach that address.