
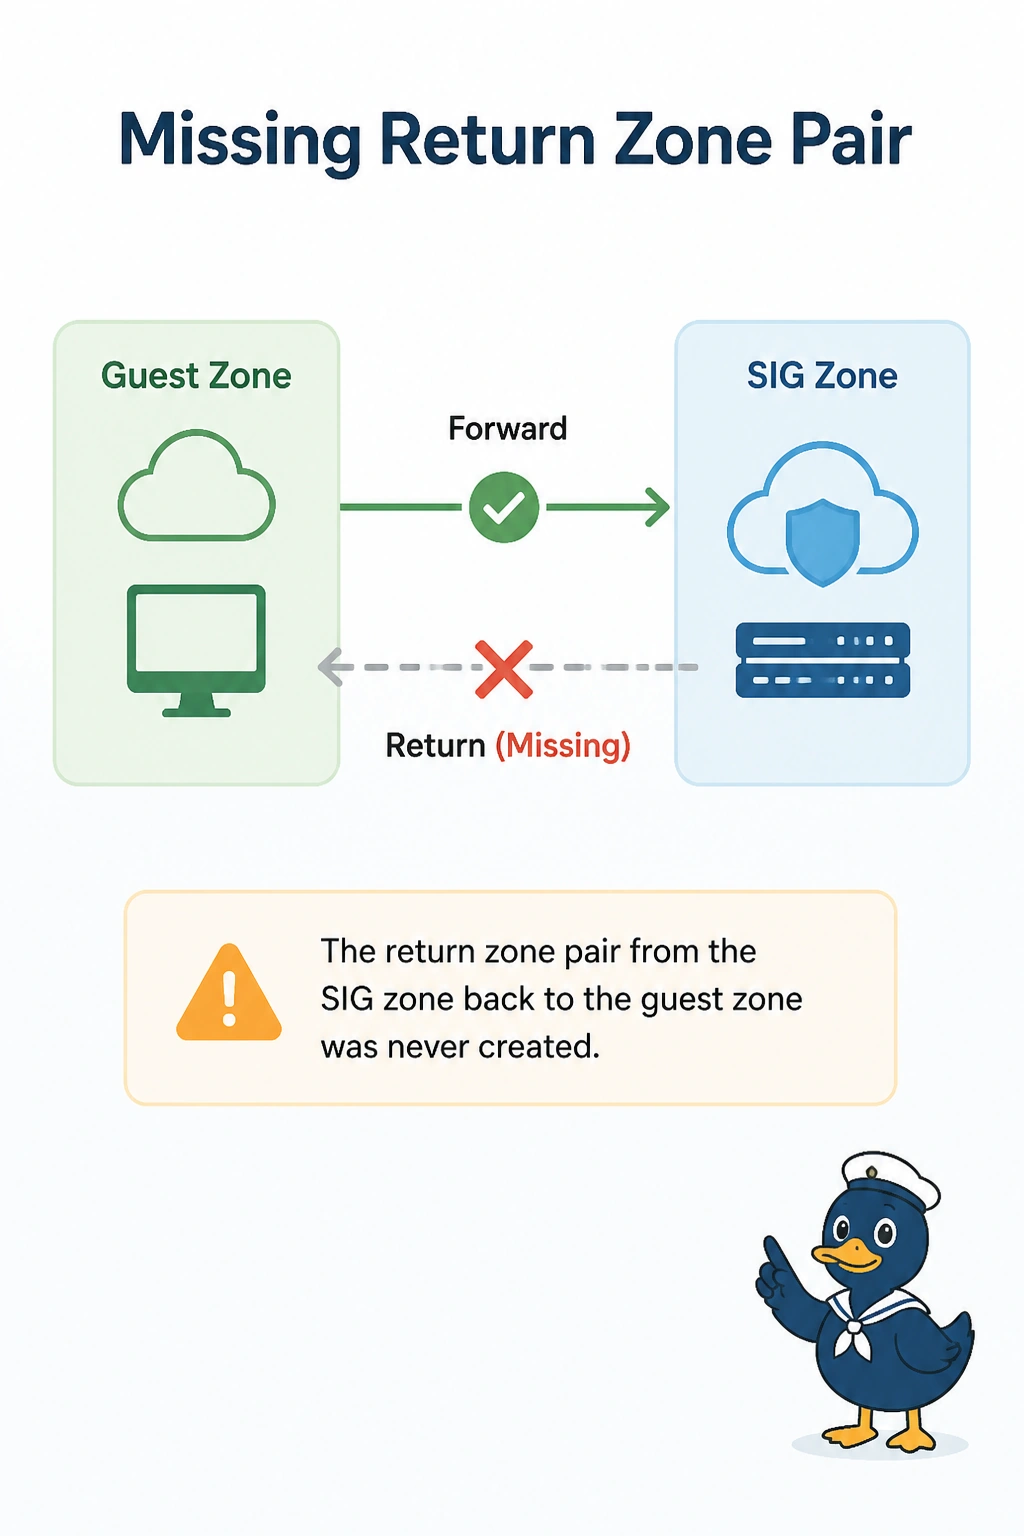
Guest web on a Catalyst SD-WAN edge is steered at a SIG tunnel that is up. The zone pair from the guest zone to the SIG zone permits the traffic, and the reverse zone pair does not exist. Sessions start and then fail. Why?
Select an answer to reveal the explanation.
Short Explanation
You opened the outbound gate and left the inbound gate bricked up. You permitted guest traffic toward the SIG zone and never created the return zone pair, so the session cannot come home. The tunnel is up, which means this is the policy direction and not a dead SIG.
Full Explanation
Catalyst SD-WAN zone pairs are directional. A pair from the guest zone to the SIG zone permits the first packets toward the tunnel. Return packets arrive in the SIG zone and need a pair back to the guest zone, or a stateful inspection rule that this policy does not have, before the session can complete. The missing reverse pair matches sessions that start and then fail. The SIG tunnel is up, so the failure is not reachability to the provider. Cloud OnRamp for SaaS does not move a guest default into a private VPC as a side effect of a zone pair. Application-aware routing does not delete zone pairs when a key rekeys. Those are different policy objects. Exam caveat: if the security policy is stateful for that zone pair, return traffic for a permitted flow may not need a second pair. This symptom says the reverse pair does not exist and the sessions fail, so state is not covering the return. Operational check: add the SIG-to-guest zone pair with the needed permit, then a guest web session should complete and the SIG log should show the full flow.