
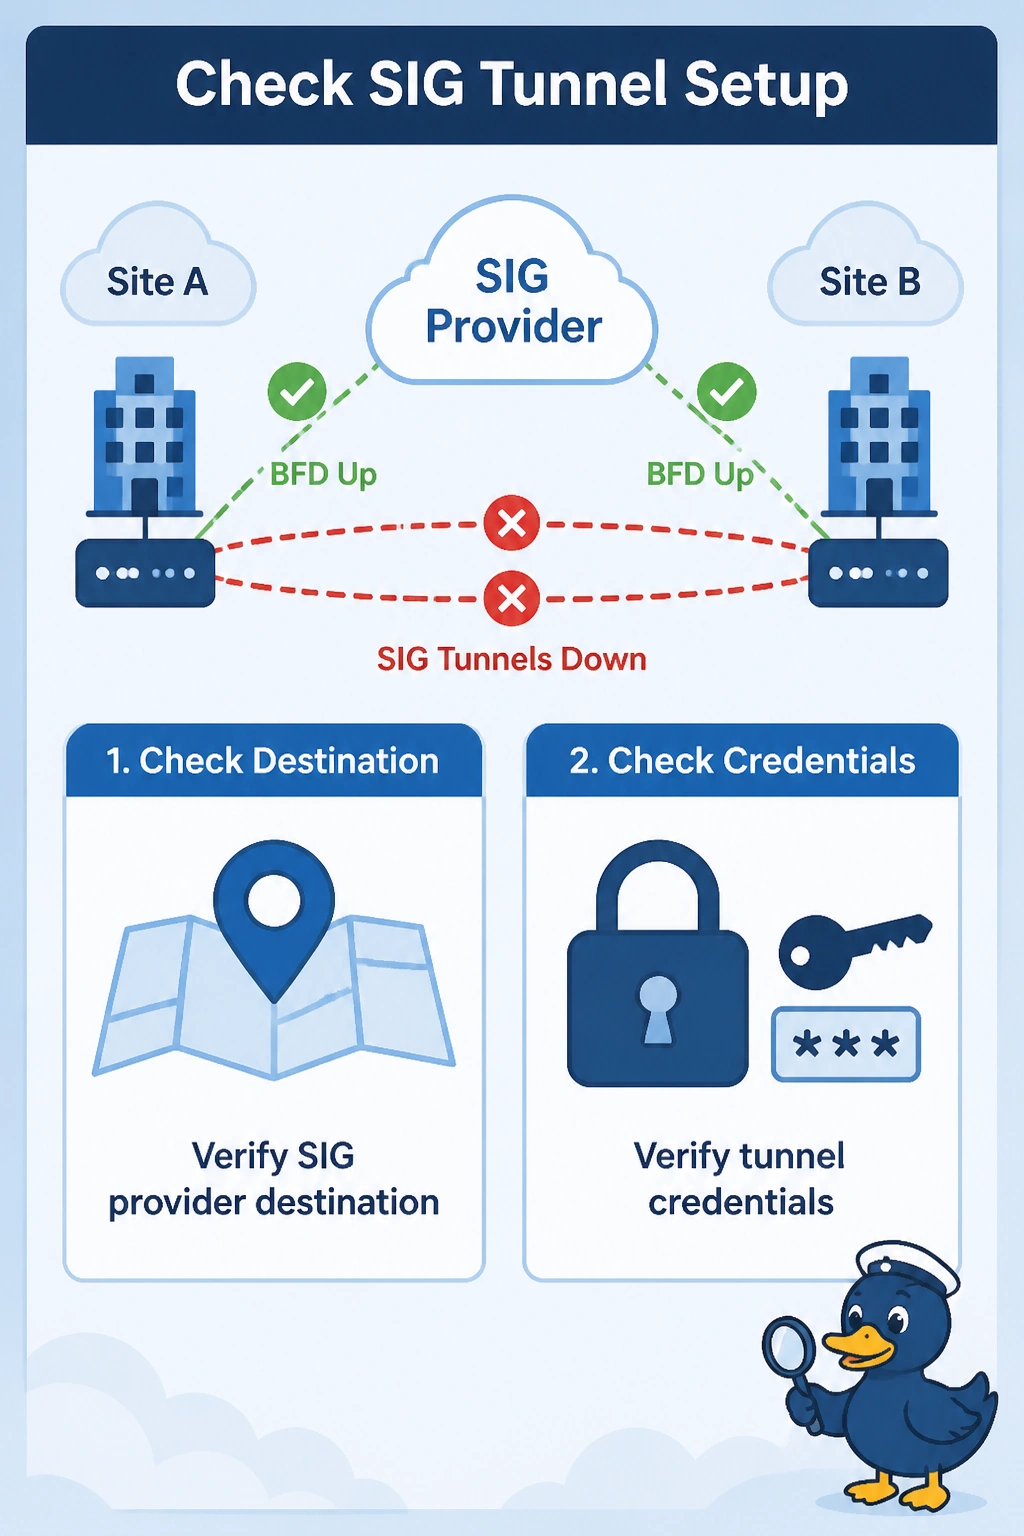
A hotel Catalyst SD-WAN edge has BFD up to its other sites, but both tunnels to the secure internet gateway are down and web traffic that should be inspected is failing. What should be checked first?
Select an answer to reveal the explanation.
Short Explanation
The overlay to your other hotels is fine, so the controllers and the underlay are not the whole story. The two tunnels that end on the secure internet gateway are the ones that are down. Check that provider's destination and the credentials that build those tunnels.
Full Explanation
BFD up to other sites shows that control and the ordinary data plane work. The SIG tunnels are a separate pair of IPsec or GRE sessions to the cloud security provider. When only those are down, the first checks are the configured SIG destination and the credentials or key the feature uses to authenticate. A wrong destination or a rotated credential leaves ordinary BFD up and the SIG tunnels down. The AWS cloud-gateway TLOC belongs to Cloud OnRamp for Multicloud. SIG tunnels are not that IaaS data plane, and this symptom does not say the AWS gateway is down. The OSPF area on the hotel LAN distributes local routes. It does not authenticate a SIG IKE identity. An Azure VPN gateway ASN is for a native Azure IPsec integration. It does not terminate the hotel's SIG tunnels unless the design was built that way, and this failure is the SIG pair. Exam caveat: a data policy can still steer web traffic at a down SIG tunnel and blackhole it. After the tunnels recover, confirm the steer still points at them rather than at an uninspected default. Operational check: the SIG tunnel status on the edge should return up after the destination and credentials match the provider portal, while BFD to the other hotels stays up the whole time.