
Campus and cloud IOS XE routers use IKEv2 certificates. The clocks match and the identity matches. The cloud router does not trust the campus certificate authority. IKE fails. What must the cloud router trust?
Select an answer to reveal the explanation.
Short Explanation
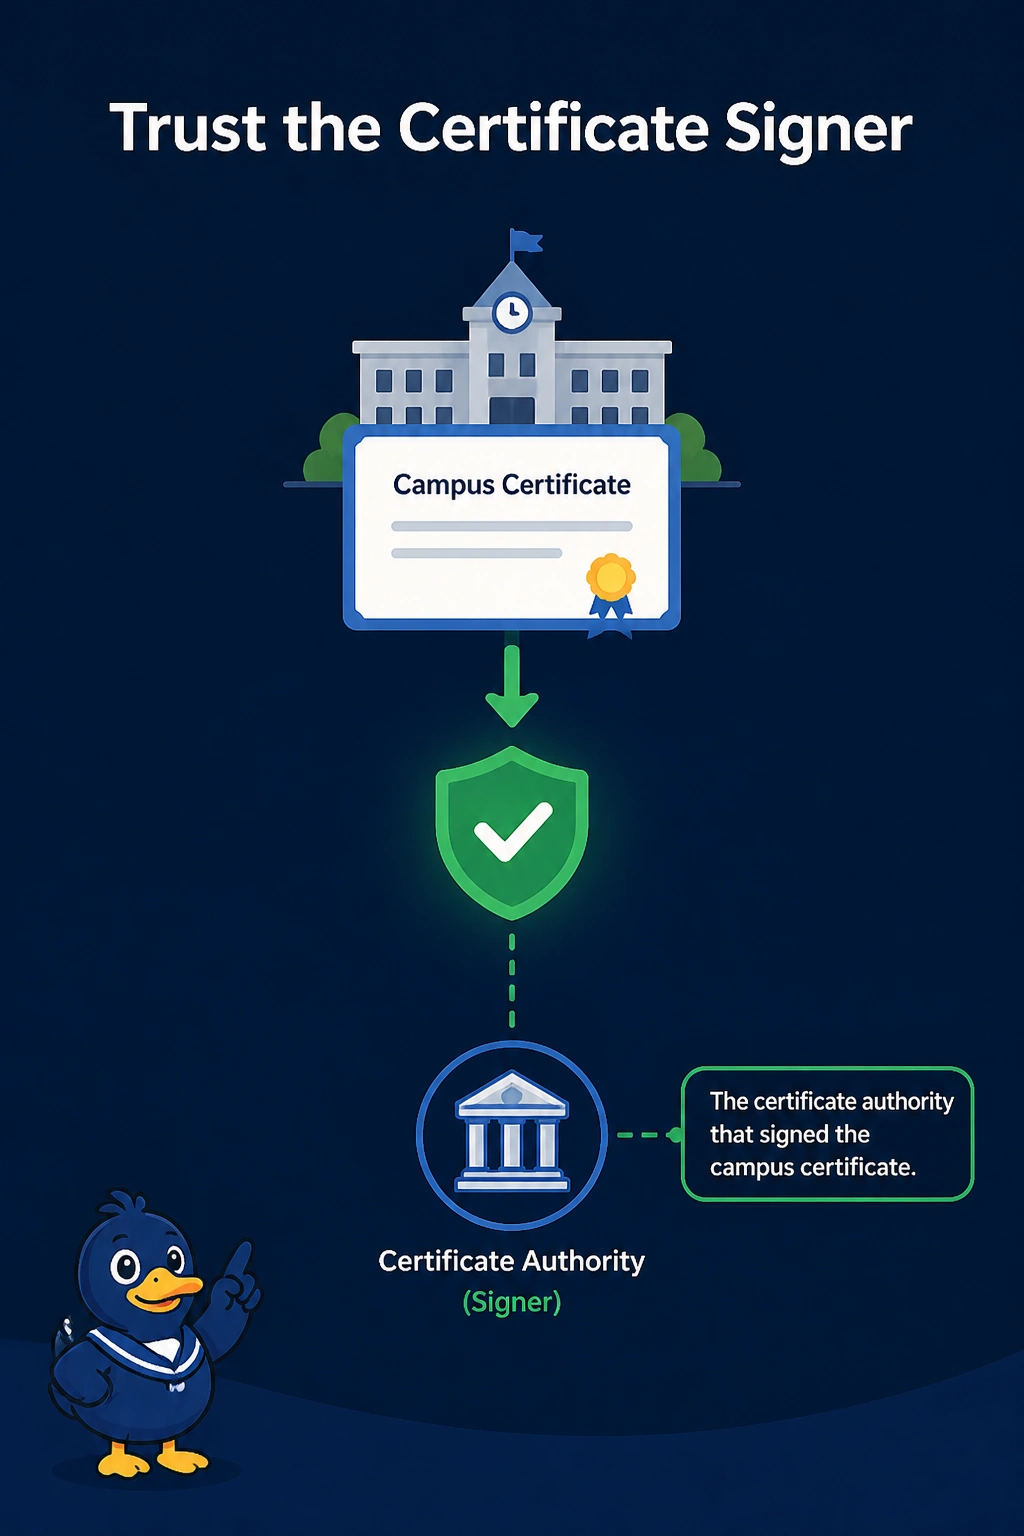
The name on the certificate is right, and you have not trusted the office that issued it. You trust the certificate authority that signed the campus certificate. A matching clock and a matching identity do not make an untrusted signature valid.
Full Explanation
Certificate authentication succeeds only if the peer trusts the authority that signed the certificate it is checking. This cloud router does not trust the campus authority, so it rejects the certificate even though the clock and the identity are already right. Install that authority's trust on the cloud router. The OSPF area is not a substitute for a certificate authority. The BGP ASN is not something the router trusts instead of a signature. Anti-replay never accepts a certificate. It only runs after an SA exists. Exam caveat: trust on one router is not enough if the campus also rejects the cloud router's authority. Each side has to trust the authority it is asked to verify. Operational check: the cloud router should show the campus authority as trusted, and show crypto ikev2 sa should reach a ready state.